The Ultimate 2026 Shodan Cheat Sheet Guide

The Ultimate 2026 Shodan Cheat Sheet Guide
Introduction In the current cybersecurity landscape, understanding an organization’s exposed digital footprint is a core priority. Shodan—often dubbed the world’s first search engine for Internet-connected devices—operates by systematically scanning IP addresses across the globe, grabbing service banners, and indexing raw protocol outputs. Unlike standard web search engines that crawl HTML page content, Shodan indexes everything from SSH servers, web portals, and databases to
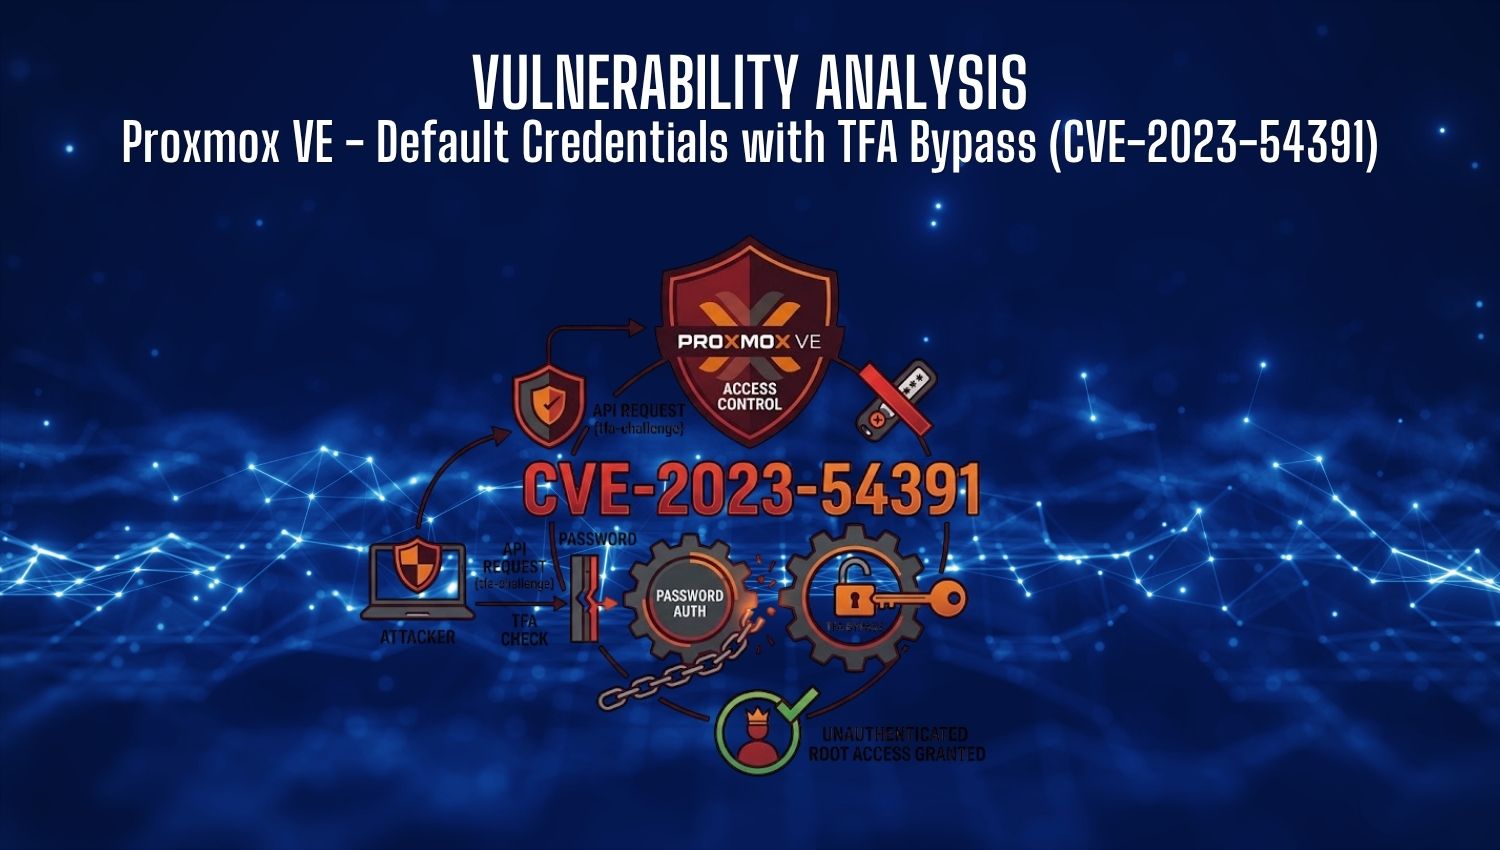
Vulnerability Analysis: Proxmox VE – Default Credentials with TFA Bypass (CVE-2023-54391)

Proxmox VE - Default Credentials with TFA Bypass (CVE-2023-54391)

Introduction CVE-2023-54391 represents a critical pre-authentication authentication bypass vulnerability in Proxmox Virtual Environment (PVE). Operating at a CVSS 3.1 score of 9.8 (Critical), this security flaw allows unauthenticated remote attackers to completely bypass standard password authentication mechanisms. By manipulating parameters in the login API endpoint, an attacker can gain full superuser (root@pam) access to the underlying hypervisor management plane without knowing the victim

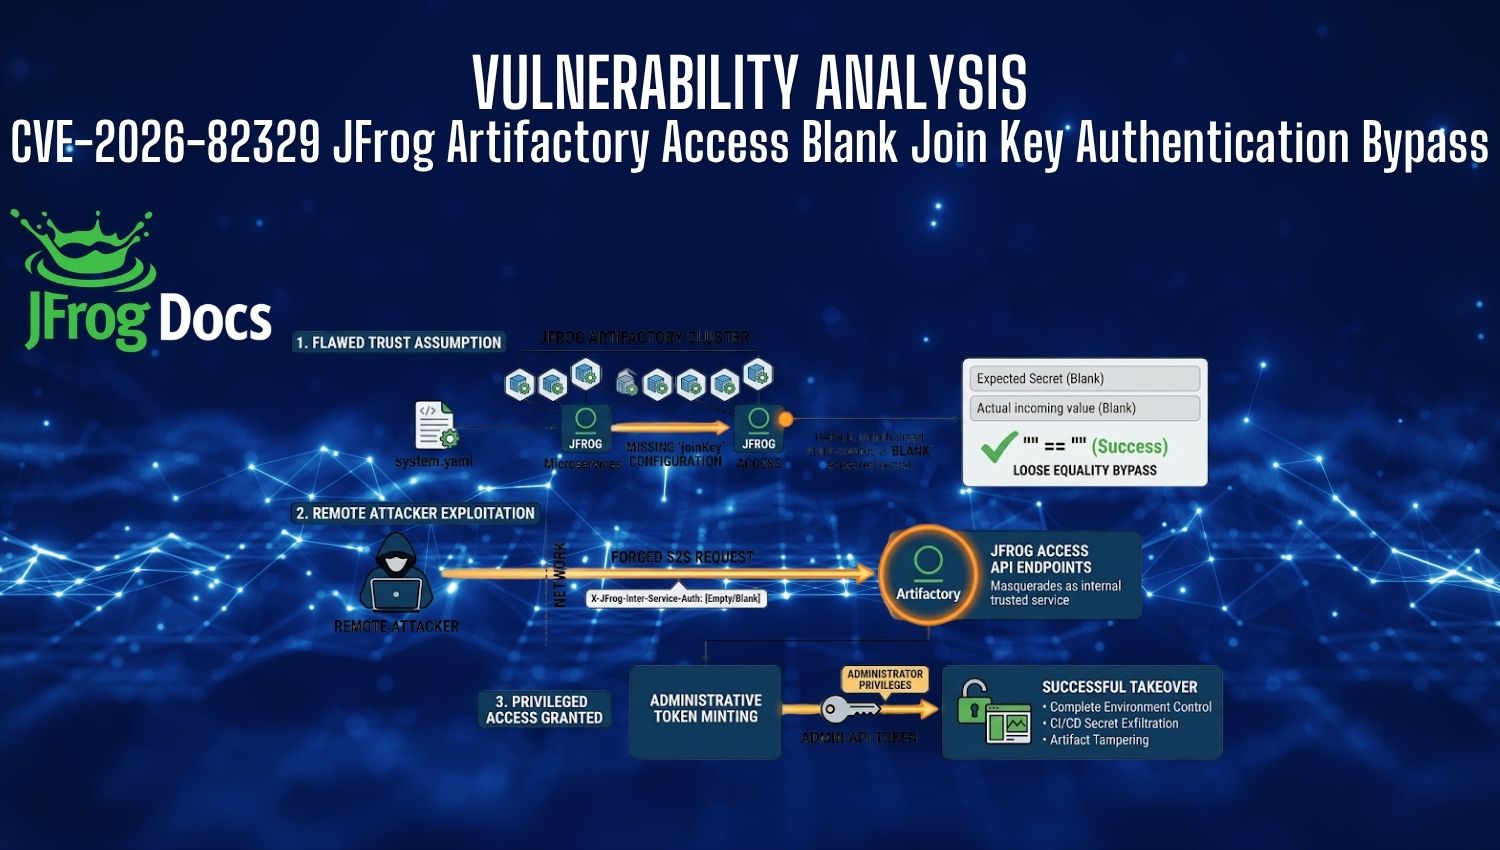
Vulnerability Analysis: CVE-2026-82329 JFrog Artifactory Access Authentication Bypass

CVE-2026-82329 JFrog Artifactory Access Blank Join Key Authentication Bypass

Introduction JFrog Artifactory serves as a central pillar in modern software engineering, providing universal artifact management across continuous integration and continuous delivery (CI/CD) pipelines. Given its privileged position—storing sensitive binaries, container images, AI models, and proprietary source code dependencies—a breach within Artifactory poses significant supply chain risks to global digital infrastructure. Disclosed in late August 2026, CVE-2026-82329 represents a critical security flaw rated 9.8 (Critical) under CVSS

Entry-Level Cybersecurity Roles and Real Required Skills

Entry-Level CybersecurIty Roles and Real RequIred SkIlls

Introduction The cybersecurity industry stands as one of the fastest-growing fields in today’s digital world, accompanied by a critical shortage of skilled talent. However, candidates aspiring to step into the sector frequently encounter a perplexing reality: job postings labeled as “Entry-Level” demand 3 to 5 years of experience, dozens of certifications, and nearly impossible lists of comprehensive competencies. This situation complicates the entry of

What is TerminalFix Attack: The New Dimension of Social Engineering

What is TerminalFix Attack

Introduction The tactics employed by threat actors evolve rapidly alongside advancements in defensive security controls. A newly uncovered campaign dubbed TerminalFix—identified by Microsoft Threat Intelligence—illustrates how traditional social engineering techniques, when blended with multi-stage technical depth, create severe organizational risk. Targeting enterprise environments across various sectors, TerminalFix exploits human trust to bypass traditional perimeter security and grant attackers persistent access to

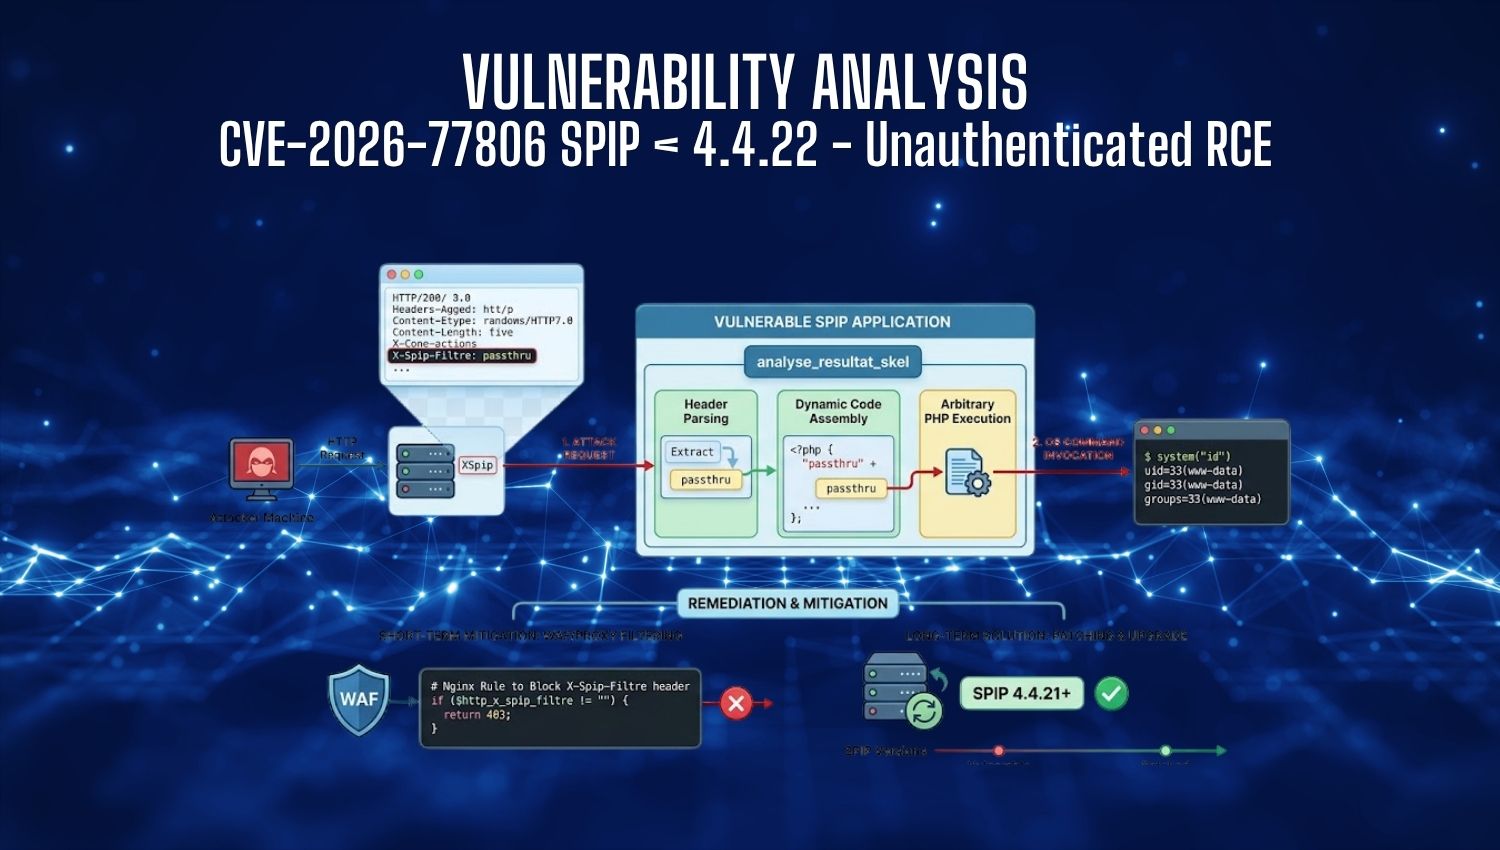
Vulnerability Analysis: SPIP < 4.4.22 – Unauthenticated RCE (CVE-2026-77806)

CVE-2026-77806 SPIP RCE

Introduction Content Management Systems (CMS) form the backbone of millions of web applications worldwide. When a critical vulnerability surfaces within a core CMS framework, the potential blast radius is immense. CVE-2026-77806 represents one such severe threat—a critical, unauthenticated Remote Code Execution (RCE) flaw affecting the SPIP publishing framework in versions prior to 4.4.21. Achieving a CVSS score of 9.8 (Critical), this vulnerability allows unauthenticated remote attackers to

Hiding Your Servers From Shodan Browsers And Creating Firewall Rules

Hiding Your Servers From Shodan Browsers And Creating Firewall Rules

Introduction In the modern cybersecurity landscape, maintaining server privacy and minimizing the exposed attack surface is paramount. Shodan is often described as the “world’s first search engine for Internet-connected devices.” Unlike traditional web search engines such as Google or Bing that index website content and URLs, Shodan actively scans the global IPv4 and IPv6 address space to index open ports, services, banners, control

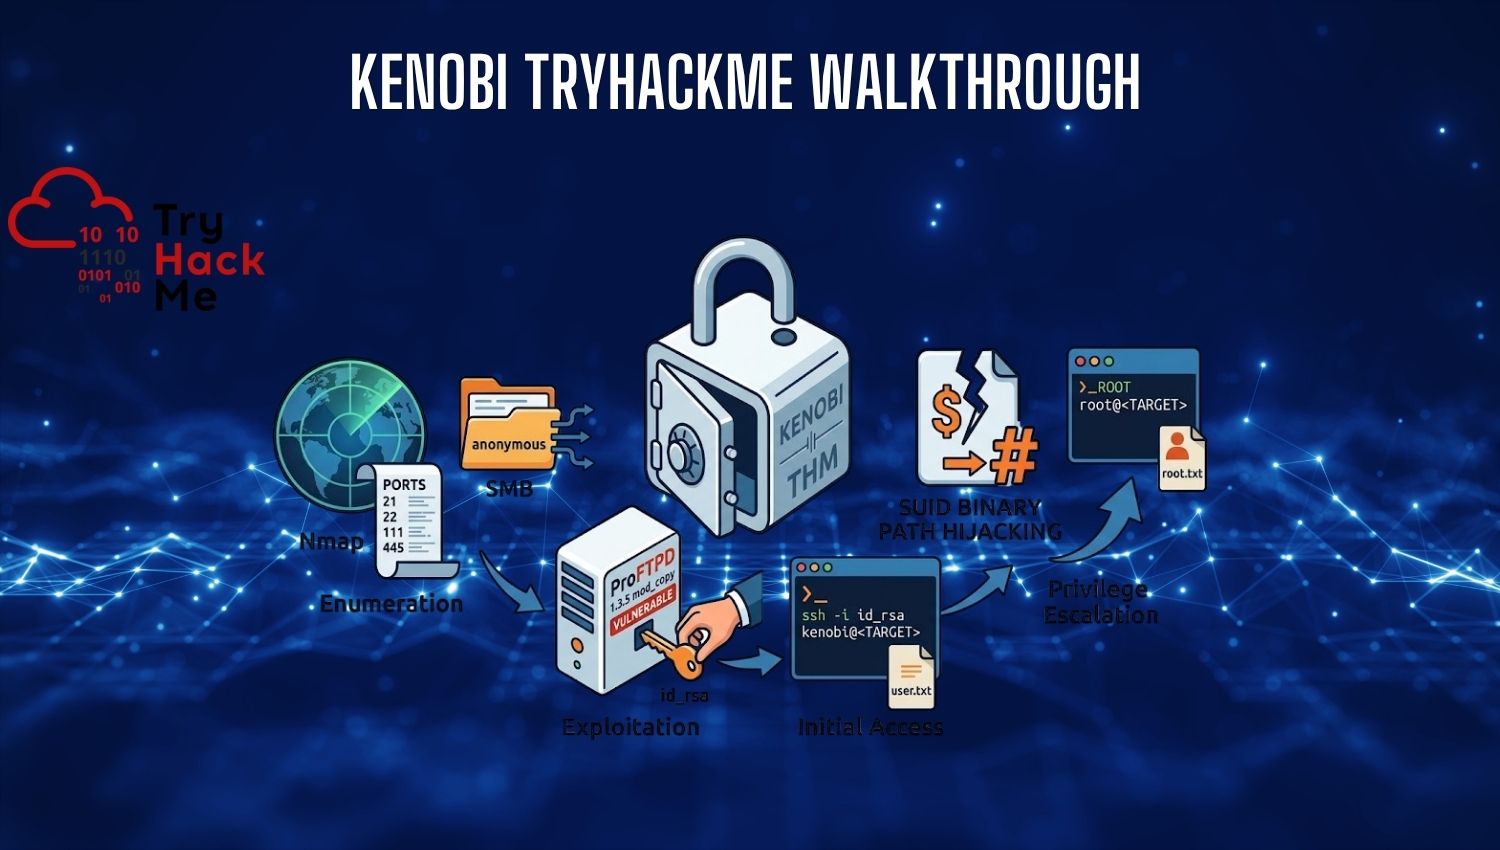
Kenobi TryHackMe Walkthrough

Introduction The Kenobi room on TryHackMe is one of the most fundamental and popular practical labs designed to teach offensive security concepts. Featuring a Linux target machine, this room introduces security researchers and aspiring penetration testers to fundamental network enumeration techniques, service exploitation, and post-exploitation privilege escalation. By walking through a realistic penetration testing scenario, learners gain hands-on experience in identifying misconfigurations and

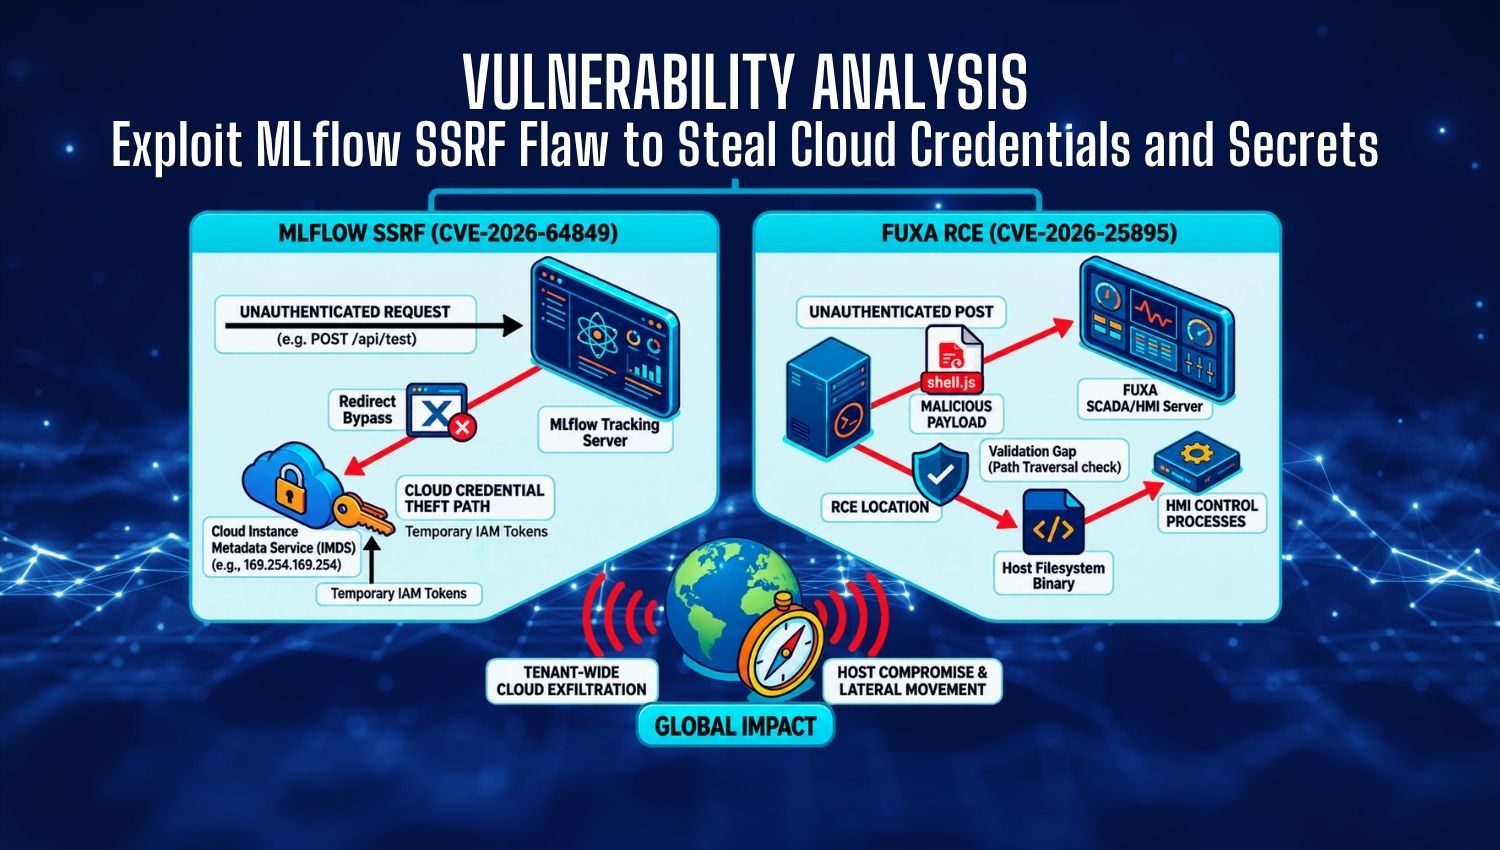
Unauthenticated Infrastructure Exploitation: From MLflow SSRF to SCADA Remote Code Execution

Exploit MLflow SSRF Flaw to Steal Cloud Credentials and Secrets

Introduction Recent security intelligence highlights a wave of sophisticated attacks targeting exposed enterprise infrastructure across modern cloud environments and industrial networks. Threat actors are actively hunting for internet-facing assets to establish initial footholds, systematically weaponizing unauthenticated vulnerabilities in popular AI lifecycle platforms and critical industrial automation systems. By abusing missing access controls and flawed input validation mechanisms, remote attackers

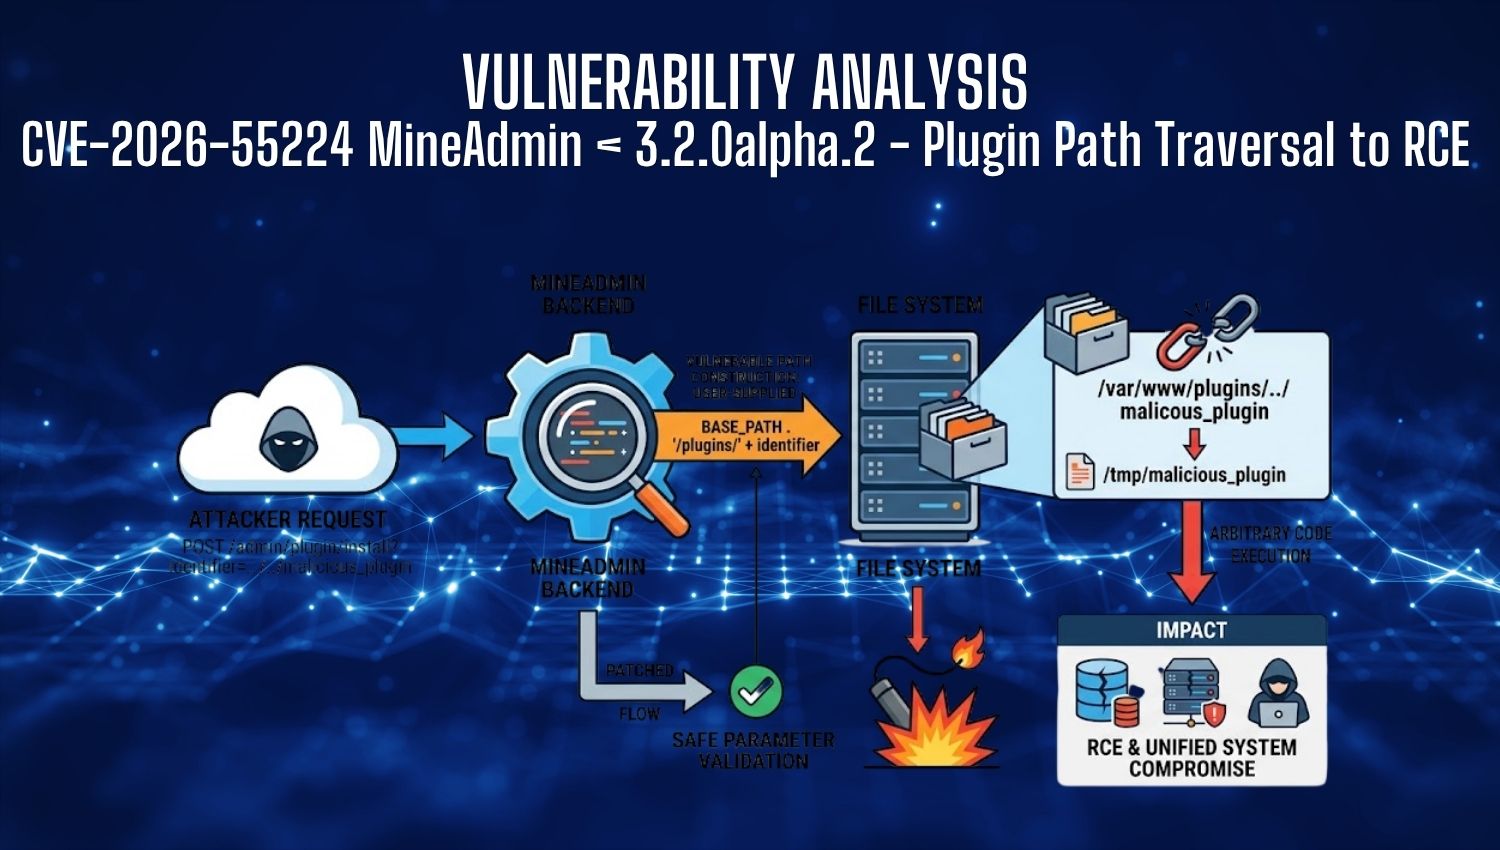
Vulnerability Analysis CVE-2026-55224 MineAdmin < 3.2.0-alpha.2 – Plugin Path Traversal to RCE

CVE-2026-55224 MineAdmin Plugin Path Traversal to RCE

Introduction MineAdmin is a popular open-source administrative framework built on the high-performance Hyperf PHP framework and Vue 3, widely adopted by enterprise developers for managing scalable microservices, backend control panels, and RESTful APIs. Despite its robust architectural design, versions prior to 3.2.0-alpha.2 suffer from a critical security flaw located within its App-Store plugin management service. By manipulating an unsanitized identifier parameter, authenticated attackers can bypass directory