What is TerminalFix Attack: The New Dimension of Social Engineering
What is TerminalFix Attack

Introduction The tactics employed by threat actors evolve rapidly alongside advancements in defensive security controls. A newly uncovered campaign dubbed TerminalFix—identified by Microsoft Threat Intelligence—illustrates how traditional social engineering techniques, when blended with multi-stage technical depth, create severe organizational risk. Targeting enterprise environments across various sectors, TerminalFix exploits human trust to bypass traditional perimeter security and grant attackers persistent access to
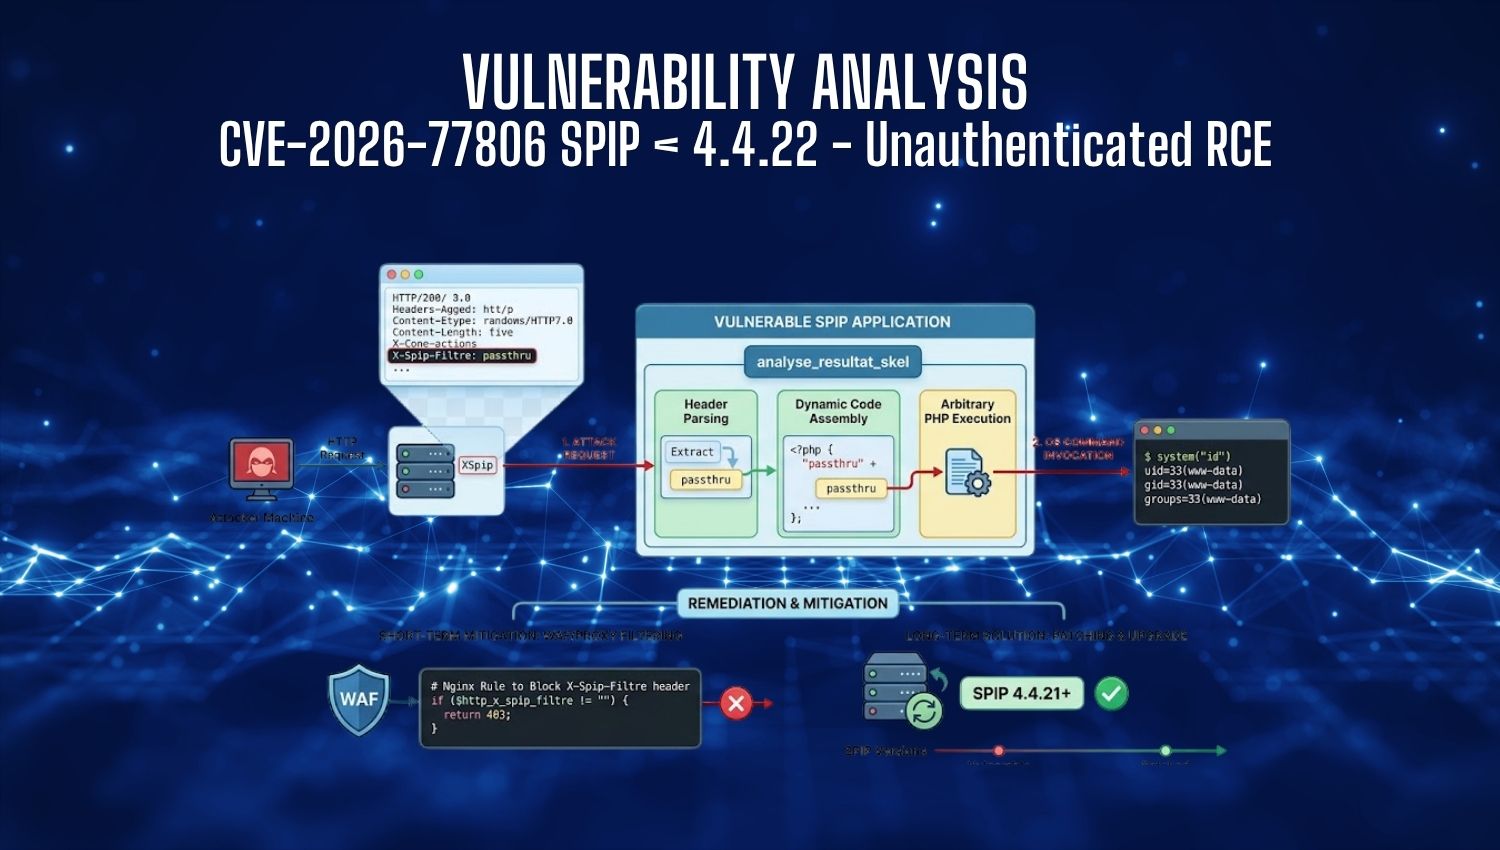
Vulnerability Analysis: SPIP < 4.4.22 – Unauthenticated RCE (CVE-2026-77806)

CVE-2026-77806 SPIP RCE

Introduction Content Management Systems (CMS) form the backbone of millions of web applications worldwide. When a critical vulnerability surfaces within a core CMS framework, the potential blast radius is immense. CVE-2026-77806 represents one such severe threat—a critical, unauthenticated Remote Code Execution (RCE) flaw affecting the SPIP publishing framework in versions prior to 4.4.21. Achieving a CVSS score of 9.8 (Critical), this vulnerability allows unauthenticated remote attackers to

Hiding Your Servers From Shodan Browsers And Creating Firewall Rules

Hiding Your Servers From Shodan Browsers And Creating Firewall Rules

Introduction In the modern cybersecurity landscape, maintaining server privacy and minimizing the exposed attack surface is paramount. Shodan is often described as the “world’s first search engine for Internet-connected devices.” Unlike traditional web search engines such as Google or Bing that index website content and URLs, Shodan actively scans the global IPv4 and IPv6 address space to index open ports, services, banners, control

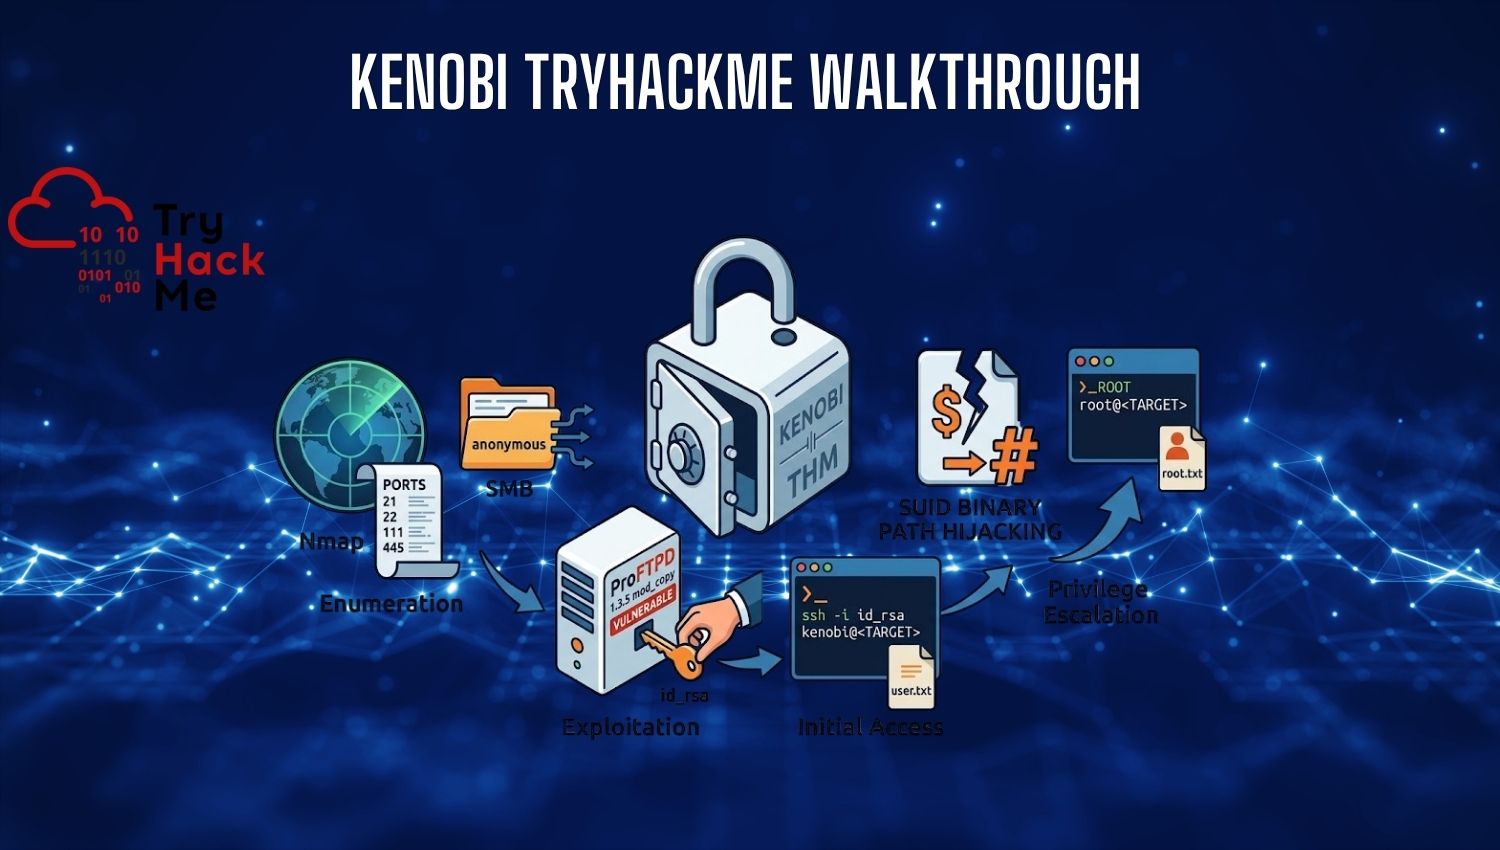
Kenobi TryHackMe Walkthrough

Introduction The Kenobi room on TryHackMe is one of the most fundamental and popular practical labs designed to teach offensive security concepts. Featuring a Linux target machine, this room introduces security researchers and aspiring penetration testers to fundamental network enumeration techniques, service exploitation, and post-exploitation privilege escalation. By walking through a realistic penetration testing scenario, learners gain hands-on experience in identifying misconfigurations and

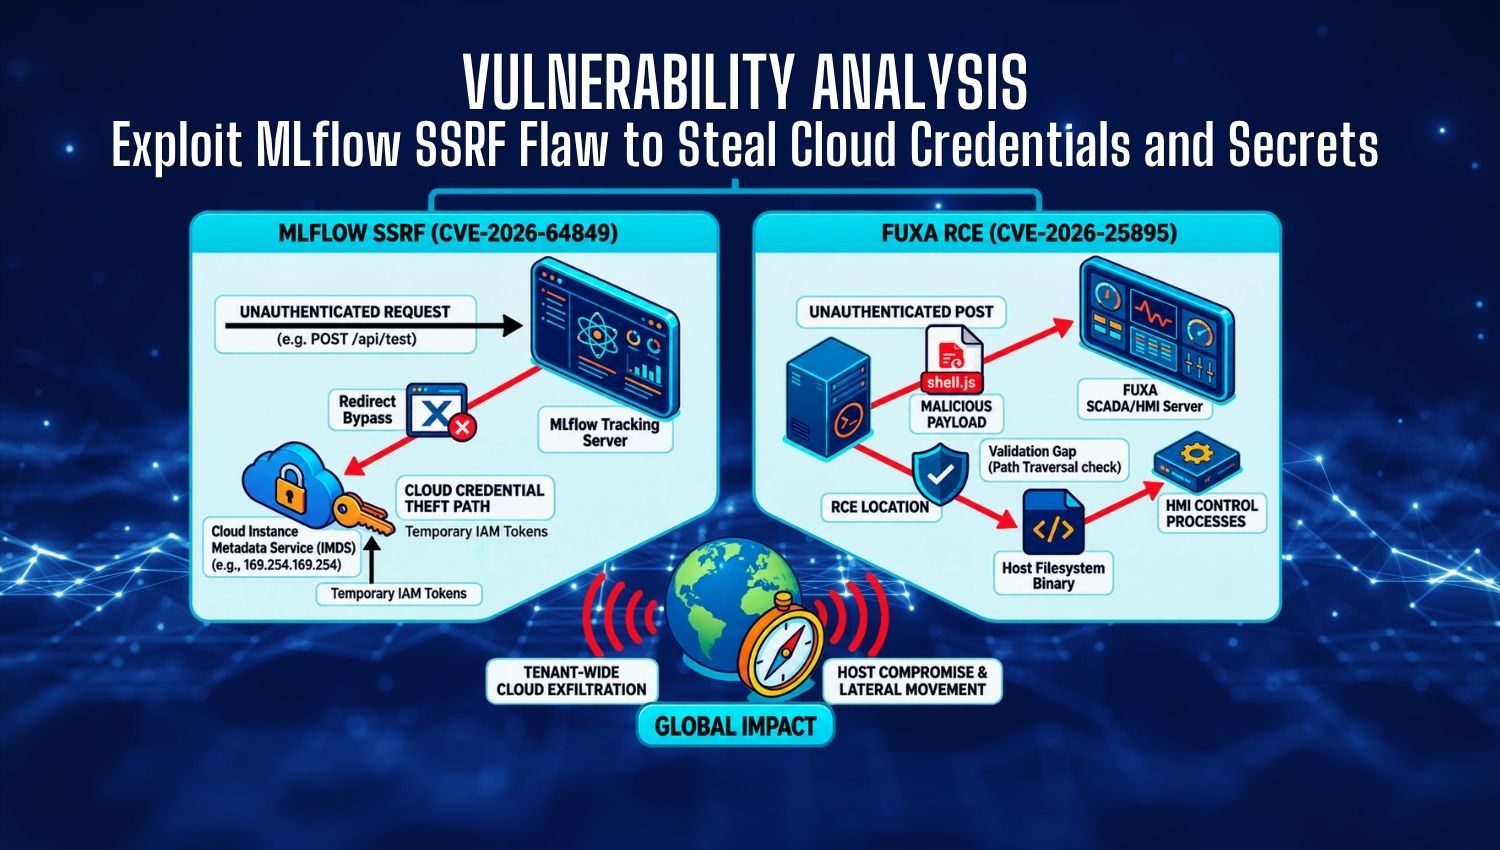
Unauthenticated Infrastructure Exploitation: From MLflow SSRF to SCADA Remote Code Execution

Exploit MLflow SSRF Flaw to Steal Cloud Credentials and Secrets

Introduction Recent security intelligence highlights a wave of sophisticated attacks targeting exposed enterprise infrastructure across modern cloud environments and industrial networks. Threat actors are actively hunting for internet-facing assets to establish initial footholds, systematically weaponizing unauthenticated vulnerabilities in popular AI lifecycle platforms and critical industrial automation systems. By abusing missing access controls and flawed input validation mechanisms, remote attackers

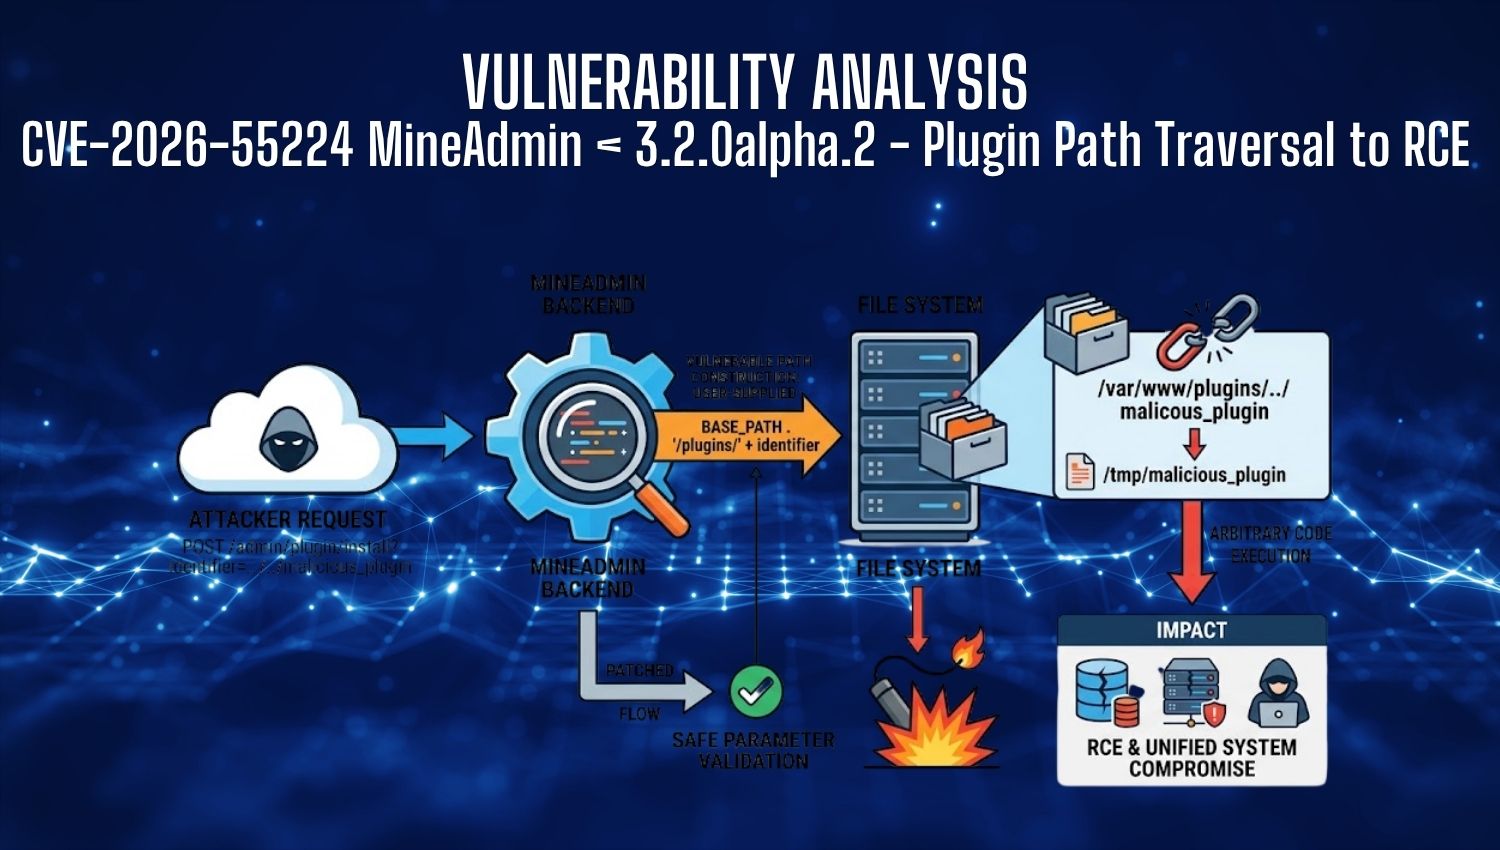
Vulnerability Analysis CVE-2026-55224 MineAdmin < 3.2.0-alpha.2 – Plugin Path Traversal to RCE

CVE-2026-55224 MineAdmin Plugin Path Traversal to RCE

Introduction MineAdmin is a popular open-source administrative framework built on the high-performance Hyperf PHP framework and Vue 3, widely adopted by enterprise developers for managing scalable microservices, backend control panels, and RESTful APIs. Despite its robust architectural design, versions prior to 3.2.0-alpha.2 suffer from a critical security flaw located within its App-Store plugin management service. By manipulating an unsanitized identifier parameter, authenticated attackers can bypass directory

Top 10 Add-ons for Burp Suite in Web Security

Top 10 Add ons for Burp SuIte In Web SecurIty

Introduction Web application security testing demands absolute precision, high operational speed, and granular visibility into non-standard protocols, modern API structures, and complex application logic. While Burp Suite (developed by PortSwigger) provides an industry-standard core engine for proxying traffic, its true power lies in its extensible architecture. By leveraging community-developed and commercial extensions, security researchers and penetration testers can seamlessly transform Burp Suite into a fully

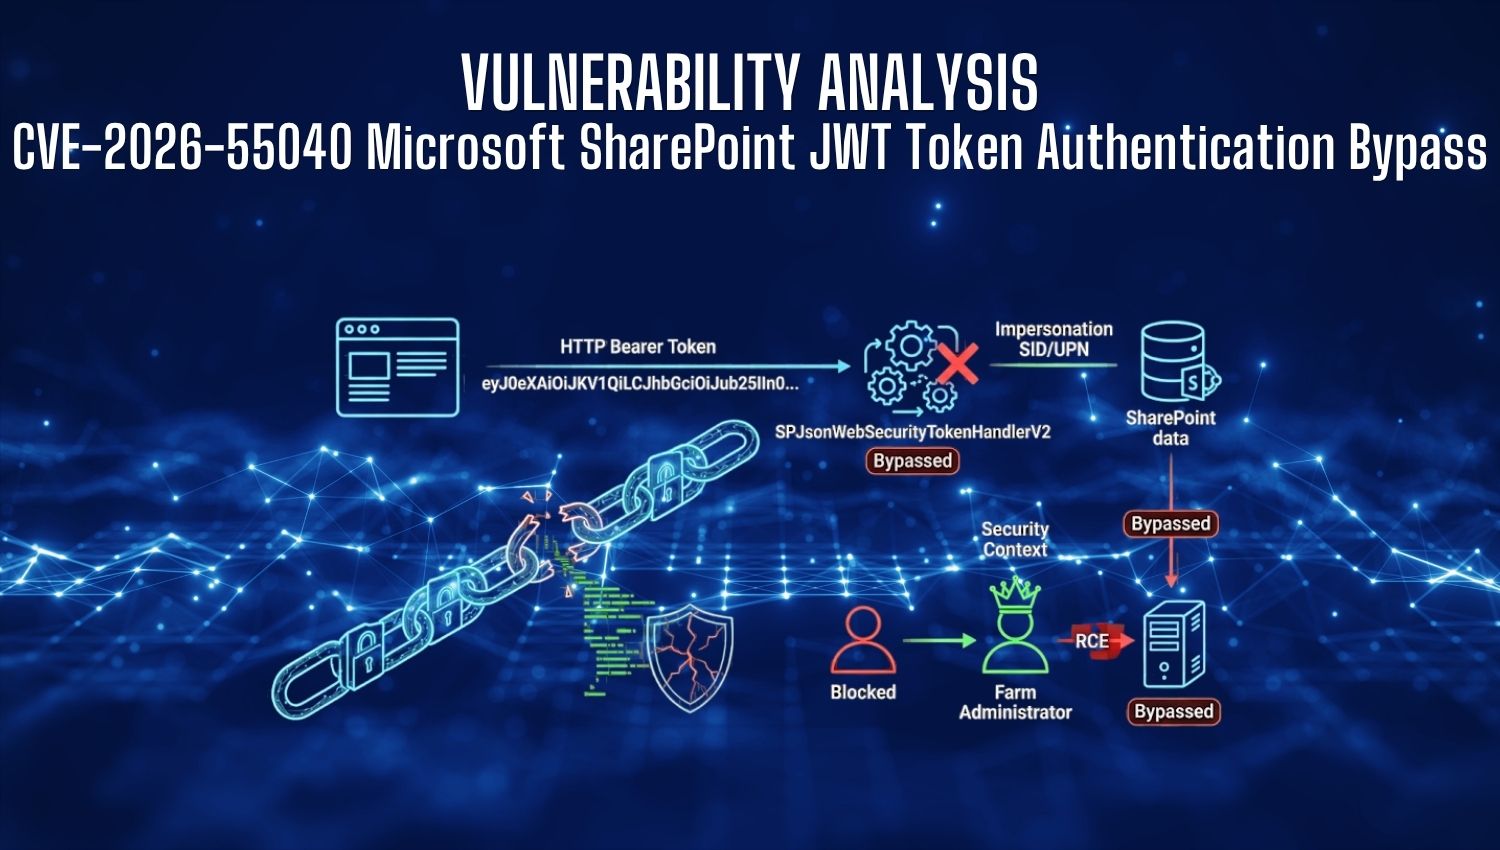
Vulnerability Analysis CVE-2026-55040 Microsoft SharePoint JWT Token Authentication Bypass

CVE-2026-55040 Microsoft SharePoint JWT Token Authentication Bypass

Introduction In recent enterprise security developments, a severe authentication bypass vulnerability designated as CVE-2026-55040 was disclosed in Microsoft SharePoint Server. Rated with a CVSS v3.1 base score of 9.1 (Critical), this flaw exposes on-premises SharePoint deployments to unauthenticated remote exploitation. Originally discovered by security researcher Stephen Fewer at Rapid7 Labs, the vulnerability lies deep within SharePoint’s identity handling and JSON Web

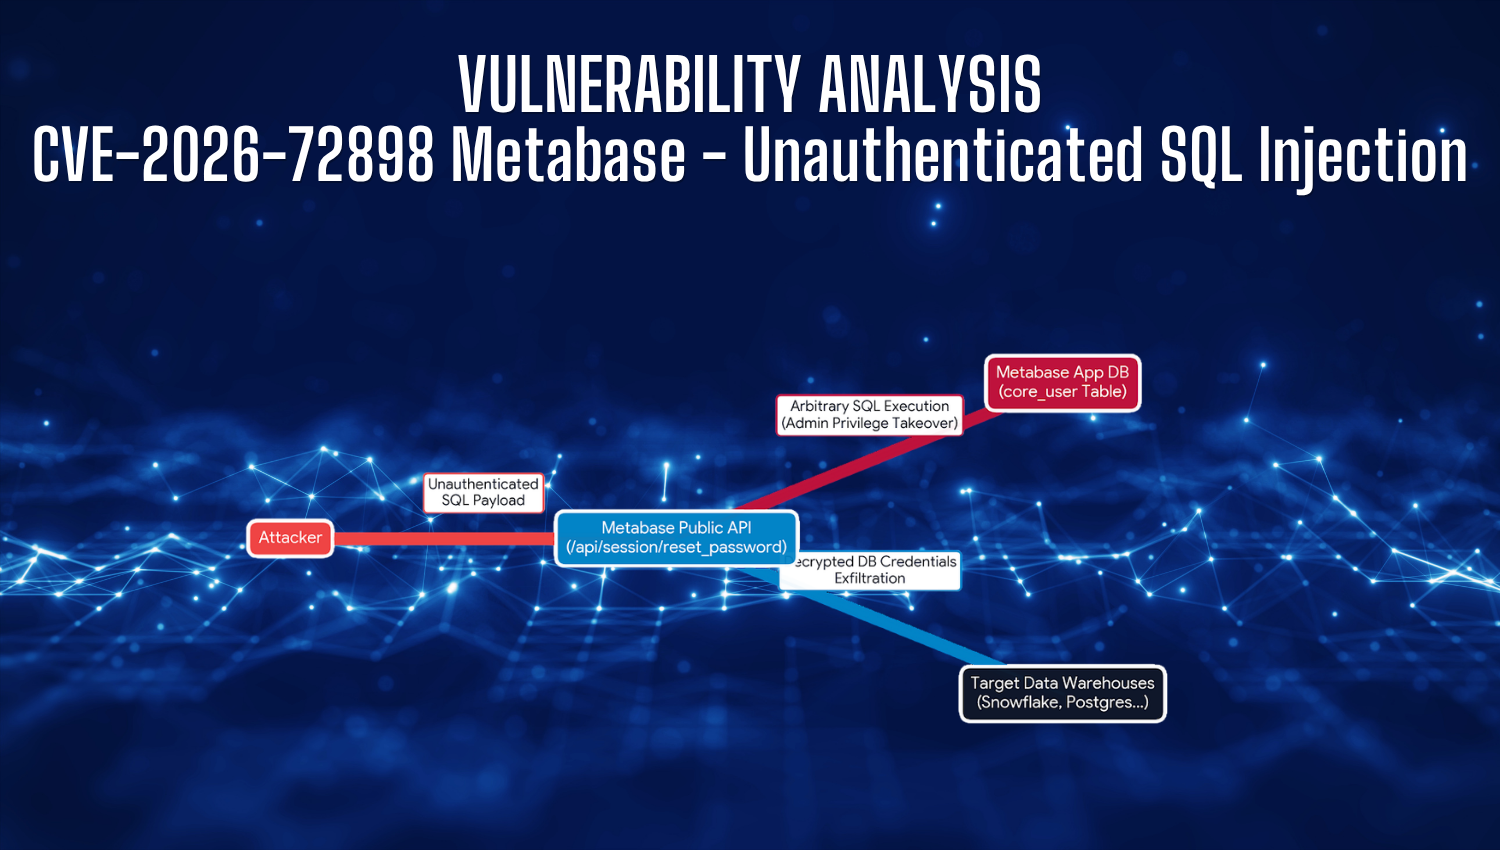
Vulnerability Analysis: CVE-2026-72898 Metabase – Unauthenticated SQL Injection

CVE-2026-72898 Metabase - Unauthenticated SQL Injection

Introduction In modern enterprise architectures, business intelligence (BI) platforms such as Metabase serve as central data gateways, aggregating access to production databases, data warehouses, and identity management systems. Consequently, vulnerabilities within BI platforms pose severe systemic risks to an organization’s entire digital infrastructure. In early August 2026, a critical security flaw identified as CVE-2026-72898 (GitHub Advisory ID: GHSA-vwf4-m7j8-wcjf) was publicly disclosed and documented as an active zero-day threat being

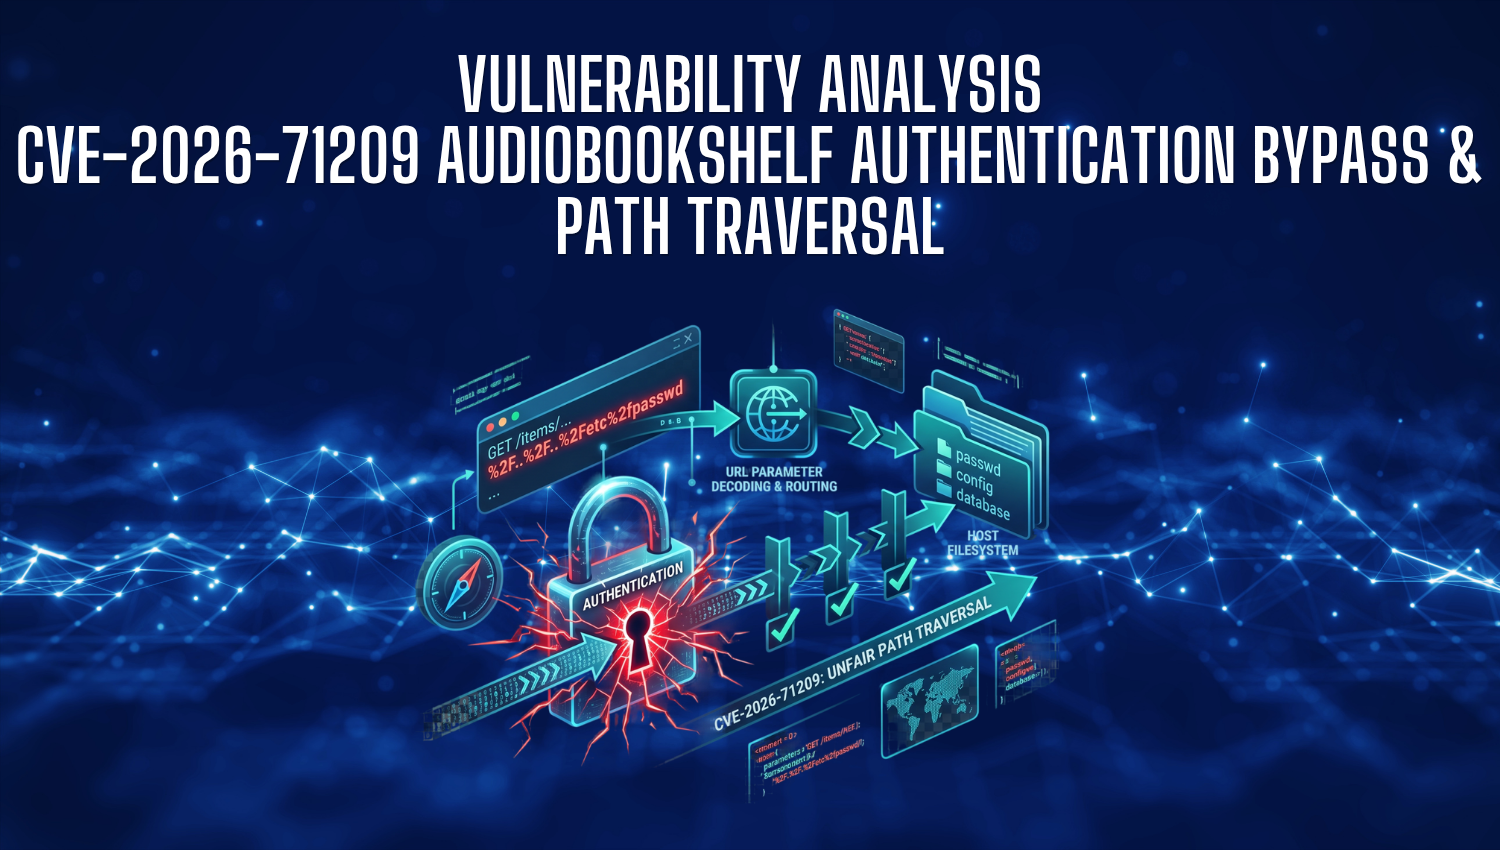
Vulnerability Analysis: CVE-2026-71209 Audiobookshelf Authentication Bypass & Path Traversal

CVE-2026-71209 AudIobookshelf AuthentIcatIon Bypass and Path Traversal

Introduction Audiobookshelf is a widely popular, open-source self-hosted media server designed for managing and streaming audiobooks and podcasts. Due to its active open-source community, rich feature set, and frequent updates, it has become a central component in many home labs and self-hosted server environments worldwide. However, security researchers recently uncovered a critical vulnerability—tracked as CVE-2026-71209—which allows remote, unauthenticated attackers to completely bypass authentication checks. By