Vulnerability Analysis: CVE-2026-123710 Critical Security Vulnerability in Red Hat Quay
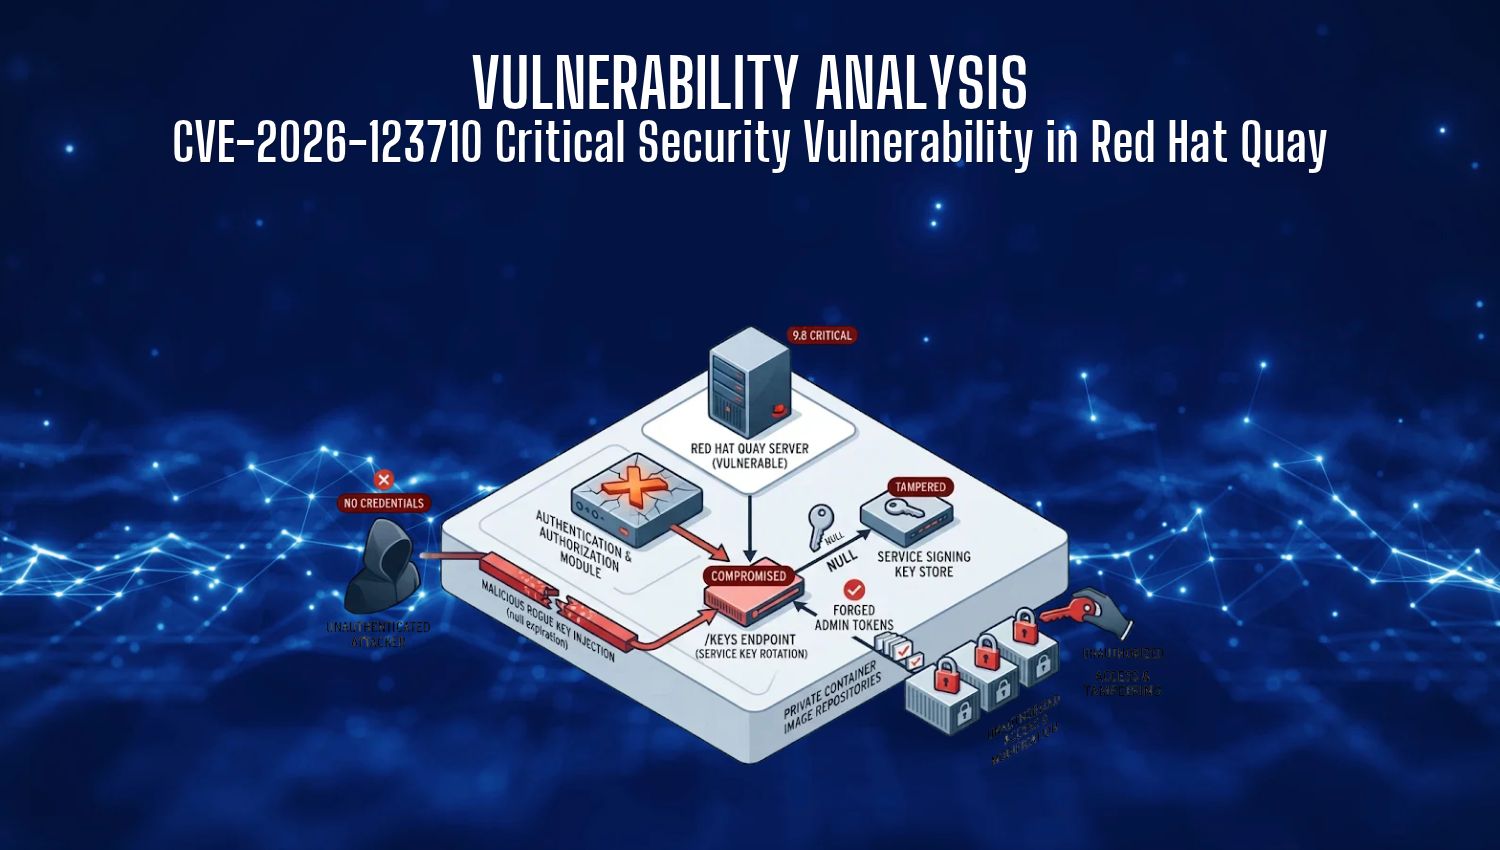
Introduction Containerized applications have become the undisputed backbone of modern enterprise architectures, transforming how software is packaged, shipped, and scaled across complex hybrid-cloud environments. As microservices proliferate, container registries serve as the central repositories for storing, managing, and distributing these vital artifacts, making them high-value targets for malicious threat actors. Red Hat Quay is widely deployed across enterprise ecosystems to ensure seamless, secure image management
Attackers Exploit AhsayCBS Flaws to Deploy Sandbox-Evading Python Backdoor

Introduction In cybersecurity operations, backup management servers represent high-value targets because they hold centralized control over system recovery infrastructure and host sensitive organizational data. In late 2026, security researchers observed threat actors exploiting critical zero-day vulnerabilities in AhsayCBS—a widely deployed cloud backup server solution—to execute unauthenticated remote code execution (RCE). By chaining an authentication bypass vulnerability with a path traversal

Vulnerability Analysis: CVE-2026-123158 “SSHole” – Critical Root Vulnerability in Alpine Linux Systems

Introduction The cybersecurity landscape recently witnessed a highly critical vulnerability dubbed “SSHole” (CVE-2026-123158). This flaw represents a severe authentication bypass issue that primarily impacts lightweight, container-friendly operating systems like Alpine Linux. By exploiting an unintended collision between several independent security mechanisms, unauthenticated remote attackers can bypass SSH authentication entirely. In specific cloud environments, this seamlessly translates to immediate, unauthorized root access, making it one

Vulnerability Analysis: CVE-2026-109518 APT MitM Vulnerability Grants Root Access

CVE-2026-109518 APT MitM Vulnerability Grants Root Access

Introduction Package managers are the backbone of system maintenance and software deployment in Linux environments. A critical security flaw, designated as CVE-2026-109518, has been identified in APT, the default package manager for Debian and Ubuntu distributions. Discovered by security researcher Max Justicz, this vulnerability allows a Man-in-the-Middle (MitM) attacker to intercept package downloads, bypass verification, and execute arbitrary code with root privileges. Because APT is ubiquitous

Vulnerability Analysis: CVE-2026-116366 ClickHouse Server – Brotli v1.2.0 Decoder DoS/OOB-Write

CVE-2026-116366

Introduction ClickHouse is a widely deployed, high-performance columnar database management system designed for online analytical processing (OLAP). To maintain its exceptional read and write speeds, ClickHouse relies heavily on efficient data compression algorithms, including Google’s Brotli library. CVE-2026-116366 represents a critical security flaw in how ClickHouse handles incoming Brotli-compressed payloads. This vulnerability exposes affected servers to unauthenticated Remote Code Execution (RCE) and Denial of

Vulnerability Analysis: CVE-2026-111497 Critical out-of-bounds write in the Node.js Brotli decoder

CVE-2026-111497

Introduction In modern web architectures, data compression plays a pivotal role in reducing network bandwidth consumption, optimizing server response times, and accelerating overall web content delivery across distributed networks. Brotli—a popular lossless data compression algorithm originally developed by Google—has quickly established itself as a ubiquitous open-source standard widely integrated across major web browsers, edge reverse proxies, content delivery networks (CDNs), and backend server

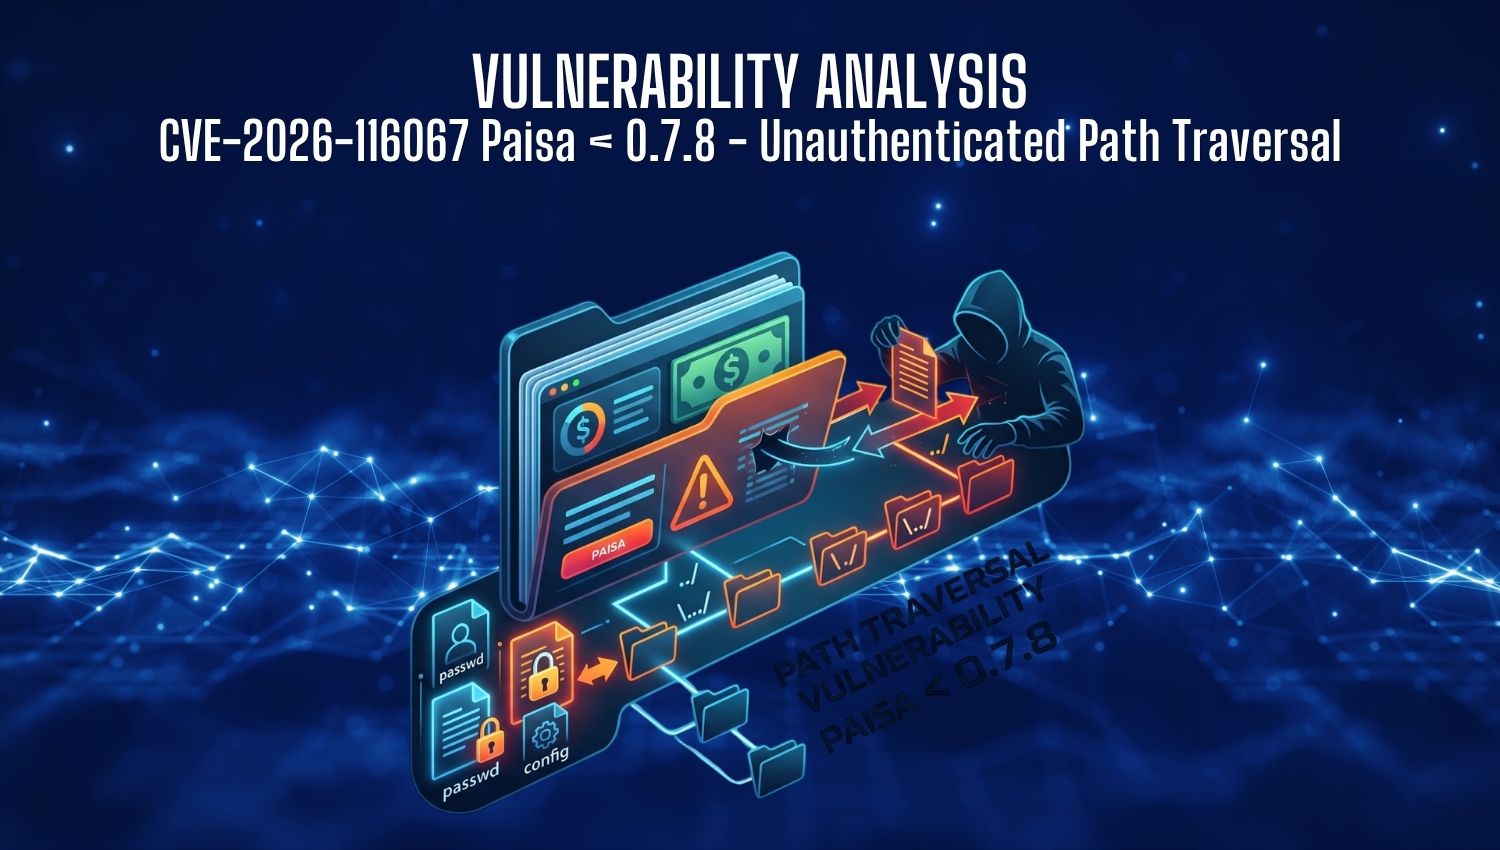
Vulnerability Analysis: CVE-2026-116067 Paisa < 0.7.8 – Unauthenticated Path Traversal

CVE-2026-116067

Introduction In modern web applications, handling file paths securely is a critical requirement. When input fields accept file paths or file names directly without adequate validation, software can become susceptible to Directory Traversal (Path Traversal) flaws. CVE-2026-116067 represents a high-severity Path Traversal vulnerability discovered in Paisa—a popular open-source, self-hosted personal finance tracking application designed to help users manage their ledgers, budgets, and investments. Self-hosted financial

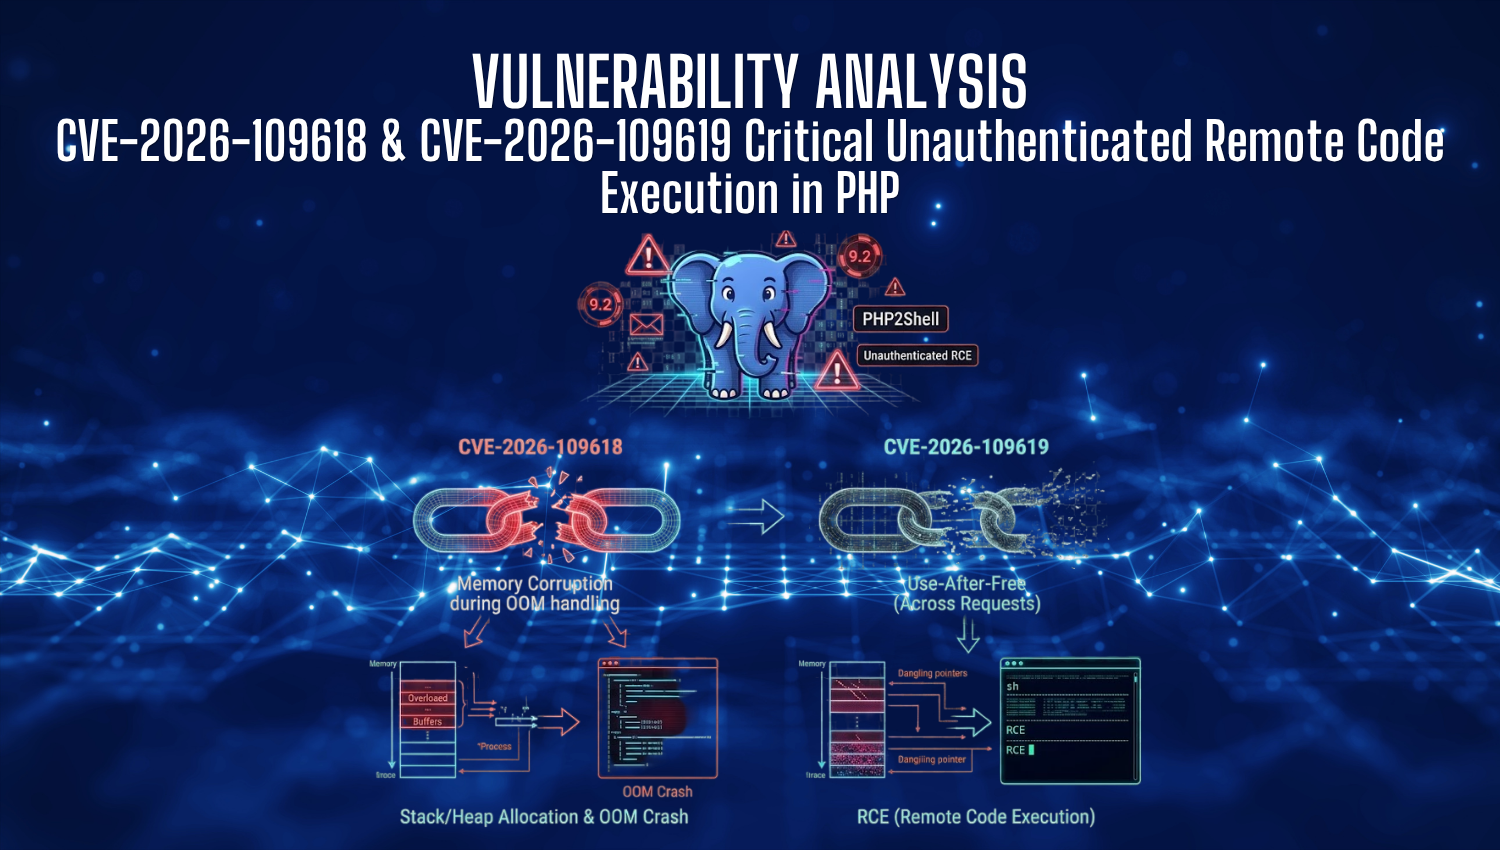
Vulnerability Analysis: CVE-2026-109618 & CVE-2026-109619 Critical Unauthenticated Remote Code Execution in PHP

Introduction CVE-2026-109618 and CVE-2026-109619 represent one of the most critical security emergencies in recent PHP history, threatening millions of active web servers globally. Highlighting the fundamental dangers of memory management flaws within persistent web server worker environments—such as PHP-FPM or Apache mod_php—these vulnerabilities enable unauthenticated remote attackers to execute arbitrary system commands with the privilege level of the

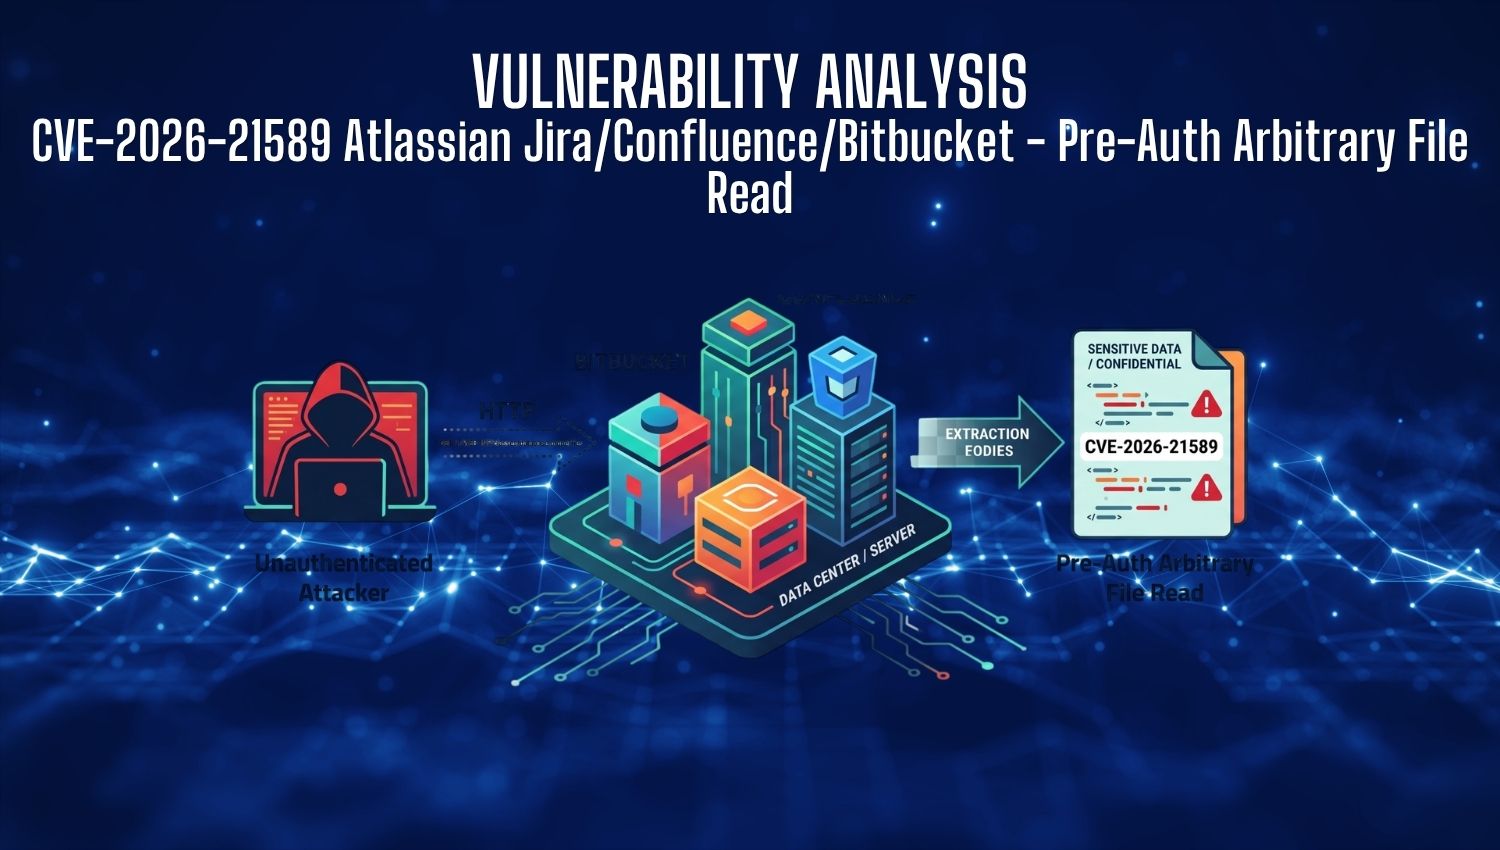
Vulnerability Analysis CVE-2026-21589 Atlassian Jira/Confluence/Bitbucket – Pre-Auth Arbitrary File Read

CVE-2026-21589

Introduction In October 2026, Atlassian issued an emergency security advisory disclosing CVE-2026-21589, a critical unauthenticated arbitrary file access vulnerability affecting its core self-hosted product suite. Assigned a CVSSv4 score of 9.3 (Critical), this security flaw allows unauthenticated remote threat actors to read arbitrary files directly from target system directories. Unauthenticated arbitrary file read vulnerabilities represent a severe risk to enterprise infrastructure because

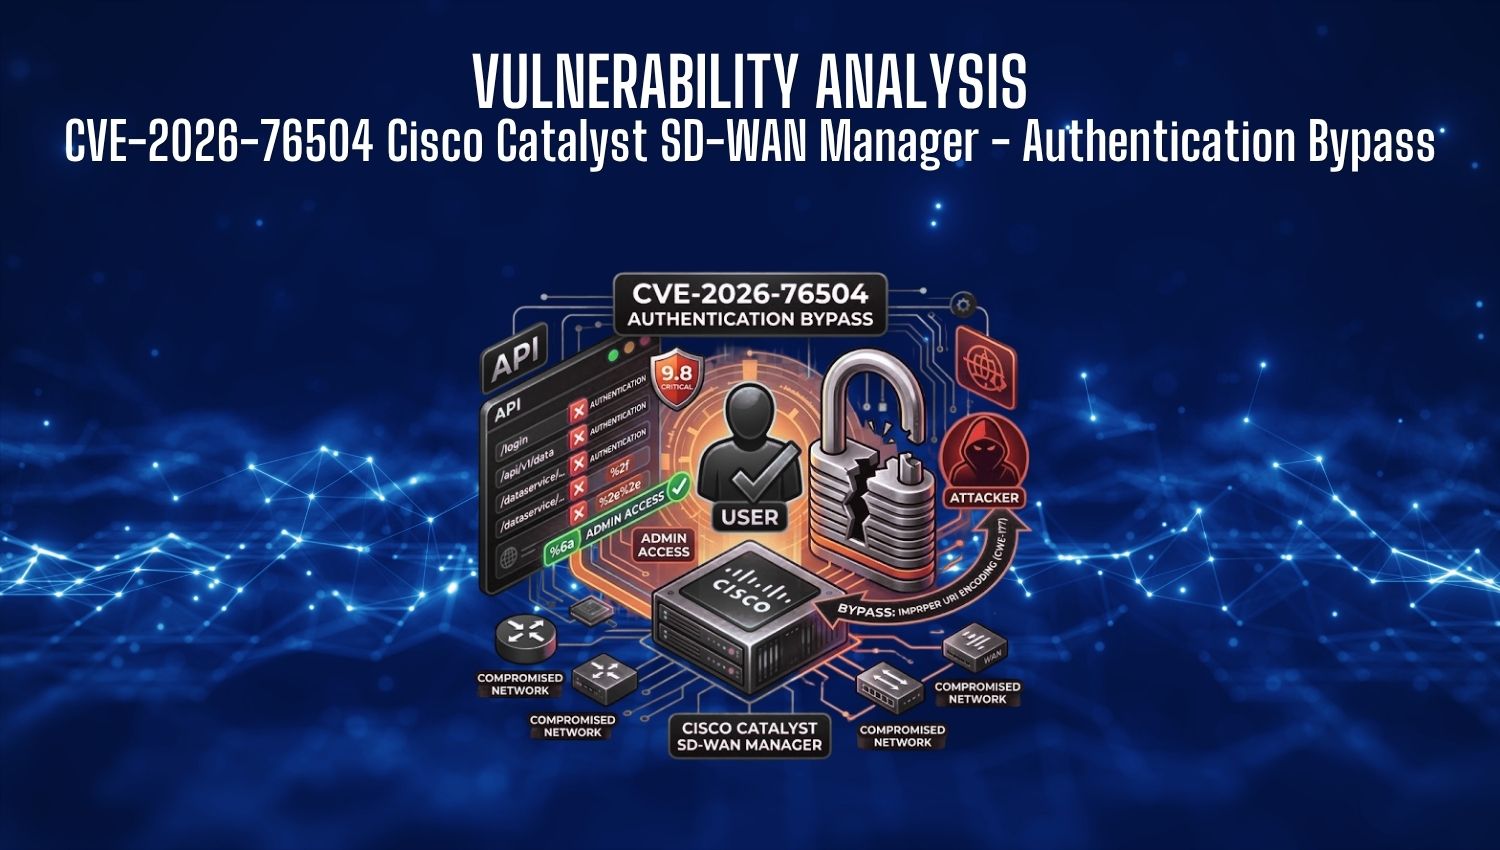
Vulnerability Analysis CVE-2026-76504 Cisco Catalyst SD-WAN Manager – Authentication Bypass

CVE-2026-76504 Cisco Catalyst SD-WAN Manager - Authentication Bypass

Introduction Centralized management platforms serve as the core control plane for modern enterprise network architectures, providing a single pane of glass for multi-cloud and wide-area network management. Cisco Catalyst SD-WAN Manager (formerly known as vManage) enables network administrators to configure, monitor, automate, and orchestrate complex enterprise wide-area networks across global deployments from a unified web interface. Because this platform possesses full administrative authority