The Ultimate 2026 Shodan Cheat Sheet Guide

The Ultimate 2026 Shodan Cheat Sheet Guide
Introduction In the current cybersecurity landscape, understanding an organization’s exposed digital footprint is a core priority. Shodan—often dubbed the world’s first search engine for Internet-connected devices—operates by systematically scanning IP addresses across the globe, grabbing service banners, and indexing raw protocol outputs. Unlike standard web search engines that crawl HTML page content, Shodan indexes everything from SSH servers, web portals, and databases to
Entry-Level Cybersecurity Roles and Real Required Skills

Entry-Level CybersecurIty Roles and Real RequIred SkIlls

Introduction The cybersecurity industry stands as one of the fastest-growing fields in today’s digital world, accompanied by a critical shortage of skilled talent. However, candidates aspiring to step into the sector frequently encounter a perplexing reality: job postings labeled as “Entry-Level” demand 3 to 5 years of experience, dozens of certifications, and nearly impossible lists of comprehensive competencies. This situation complicates the entry of

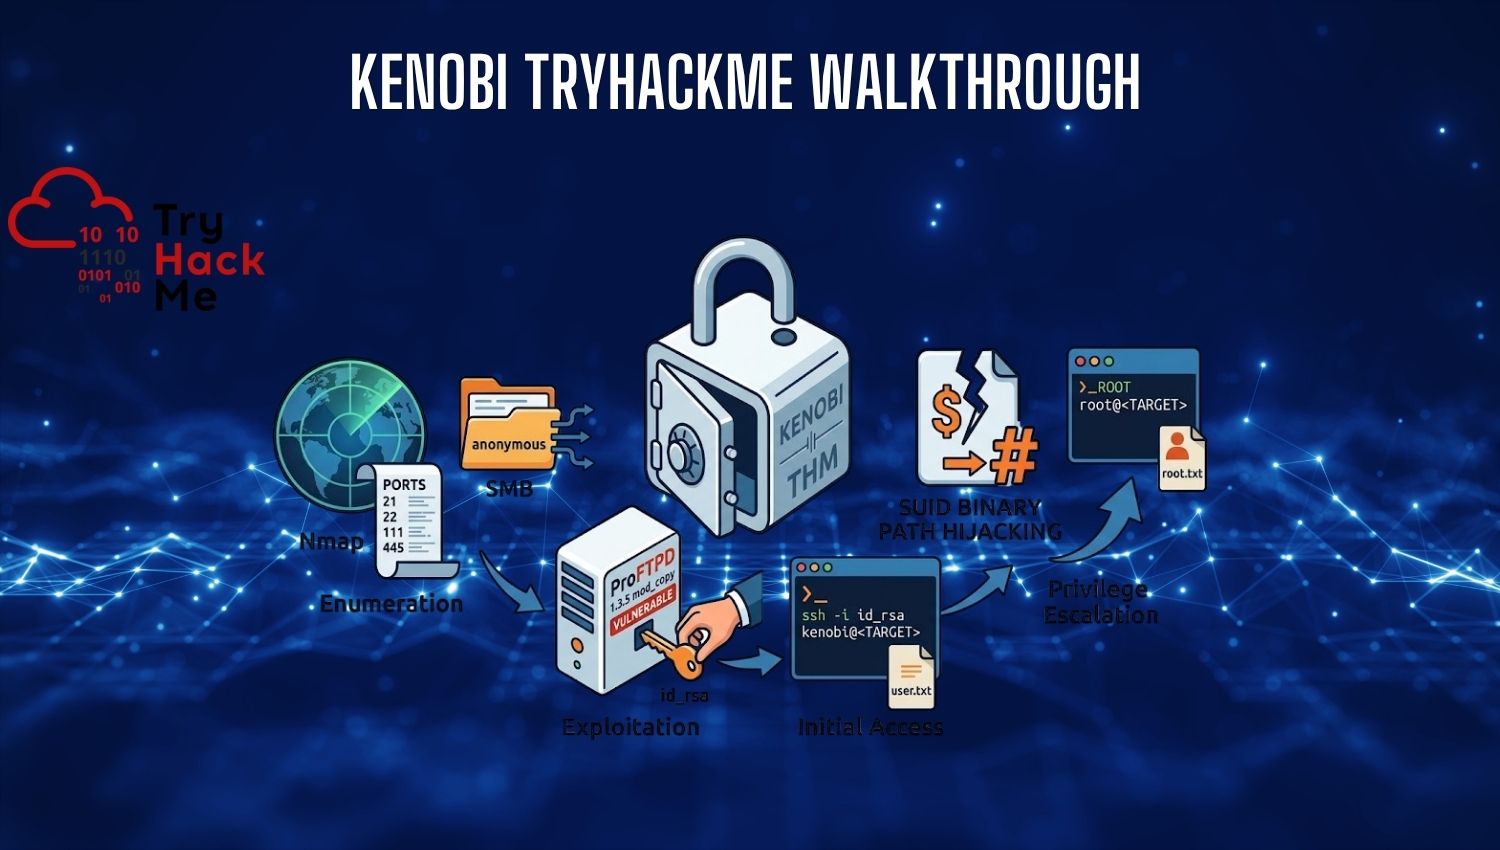
Kenobi TryHackMe Walkthrough

Introduction The Kenobi room on TryHackMe is one of the most fundamental and popular practical labs designed to teach offensive security concepts. Featuring a Linux target machine, this room introduces security researchers and aspiring penetration testers to fundamental network enumeration techniques, service exploitation, and post-exploitation privilege escalation. By walking through a realistic penetration testing scenario, learners gain hands-on experience in identifying misconfigurations and

Top 10 Add-ons for Burp Suite in Web Security

Top 10 Add ons for Burp SuIte In Web SecurIty

Introduction Web application security testing demands absolute precision, high operational speed, and granular visibility into non-standard protocols, modern API structures, and complex application logic. While Burp Suite (developed by PortSwigger) provides an industry-standard core engine for proxying traffic, its true power lies in its extensible architecture. By leveraging community-developed and commercial extensions, security researchers and penetration testers can seamlessly transform Burp Suite into a fully

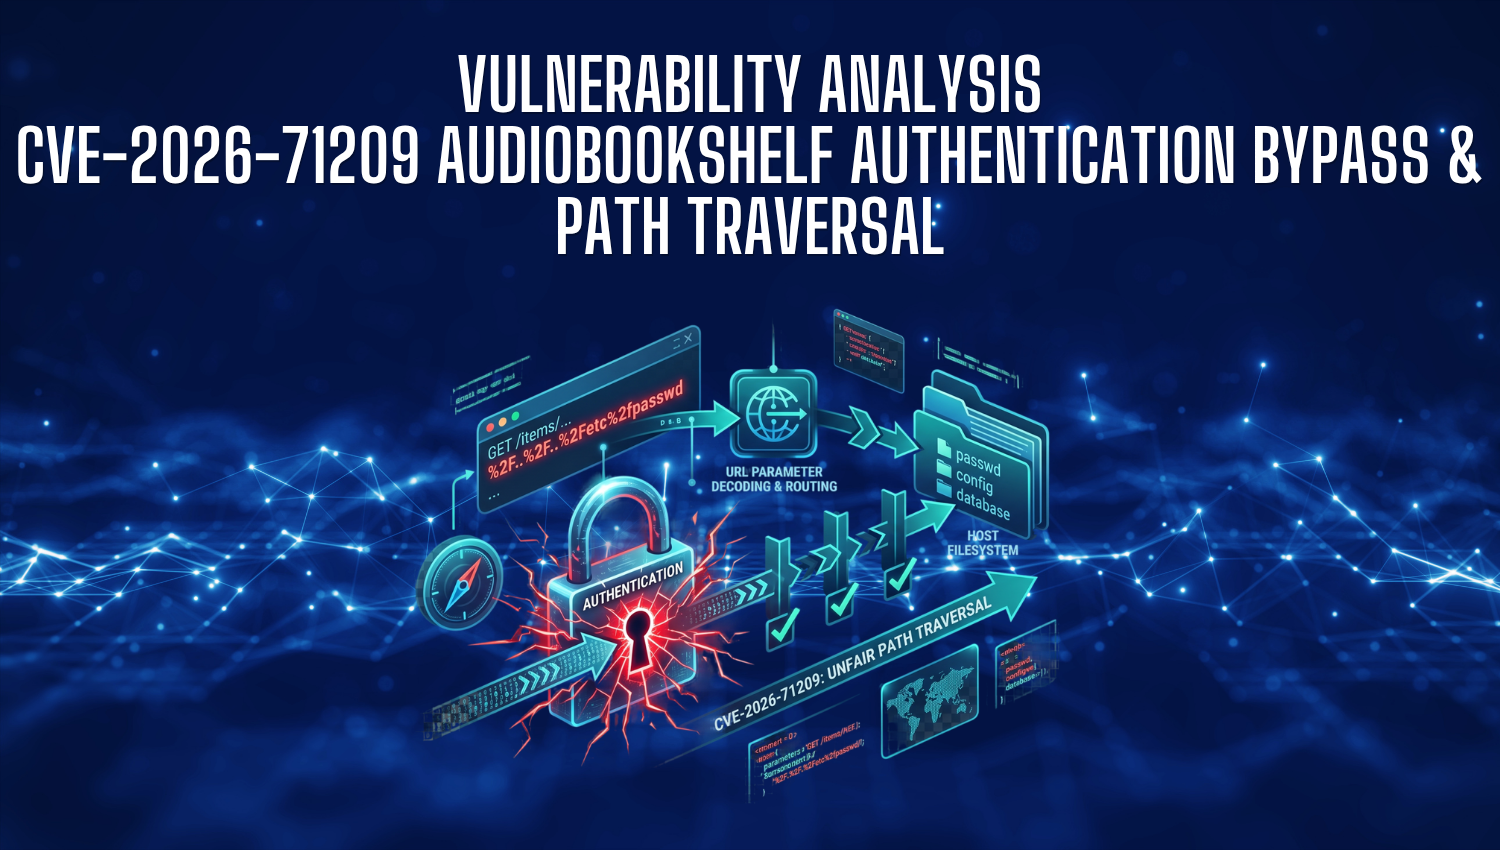
Vulnerability Analysis: CVE-2026-71209 Audiobookshelf Authentication Bypass & Path Traversal

CVE-2026-71209 AudIobookshelf AuthentIcatIon Bypass and Path Traversal

Introduction Audiobookshelf is a widely popular, open-source self-hosted media server designed for managing and streaming audiobooks and podcasts. Due to its active open-source community, rich feature set, and frequent updates, it has become a central component in many home labs and self-hosted server environments worldwide. However, security researchers recently uncovered a critical vulnerability—tracked as CVE-2026-71209—which allows remote, unauthenticated attackers to completely bypass authentication checks. By

The Ultimate Guide to 360 TryHackMe Free Rooms: Master Cybersecurity for Free

Remote Active Directory Pentesting A Comprehensive Overview

Introduction Starting a career in cybersecurity can feel like standing at the foot of an impossibly tall mountain. With endless sub-fields—ranging from web application security and digital forensics to reverse engineering, malware analysis, and cloud security—it is remarkably easy for beginners to feel overwhelmed about where to start, which path to follow, and what skills to prioritize. Fortunately, hands-on platforms like TryHackMe (THM) have