Vulnerability Analysis: CVE-2026-109518 APT MitM Vulnerability Grants Root Access
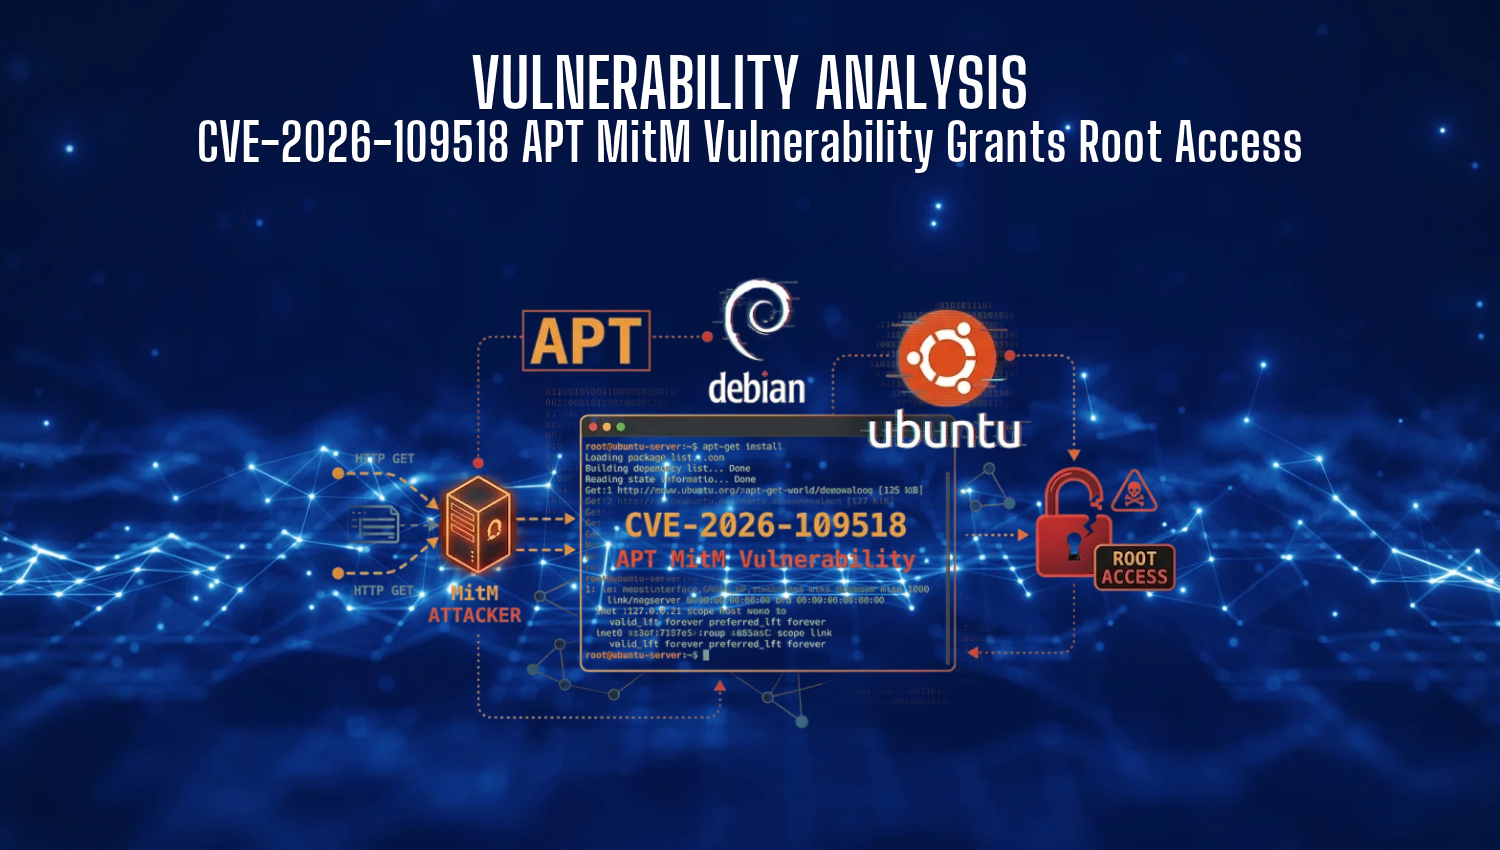
CVE-2026-109518 APT MitM Vulnerability Grants Root Access

Introduction Package managers are the backbone of system maintenance and software deployment in Linux environments. A critical security flaw, designated as CVE-2026-109518, has been identified in APT, the default package manager for Debian and Ubuntu distributions. Discovered by security researcher Max Justicz, this vulnerability allows a Man-in-the-Middle (MitM) attacker to intercept package downloads, bypass verification, and execute arbitrary code with root privileges. Because APT is ubiquitous
Vulnerability Analysis: CVE-2026-116366 ClickHouse Server – Brotli v1.2.0 Decoder DoS/OOB-Write

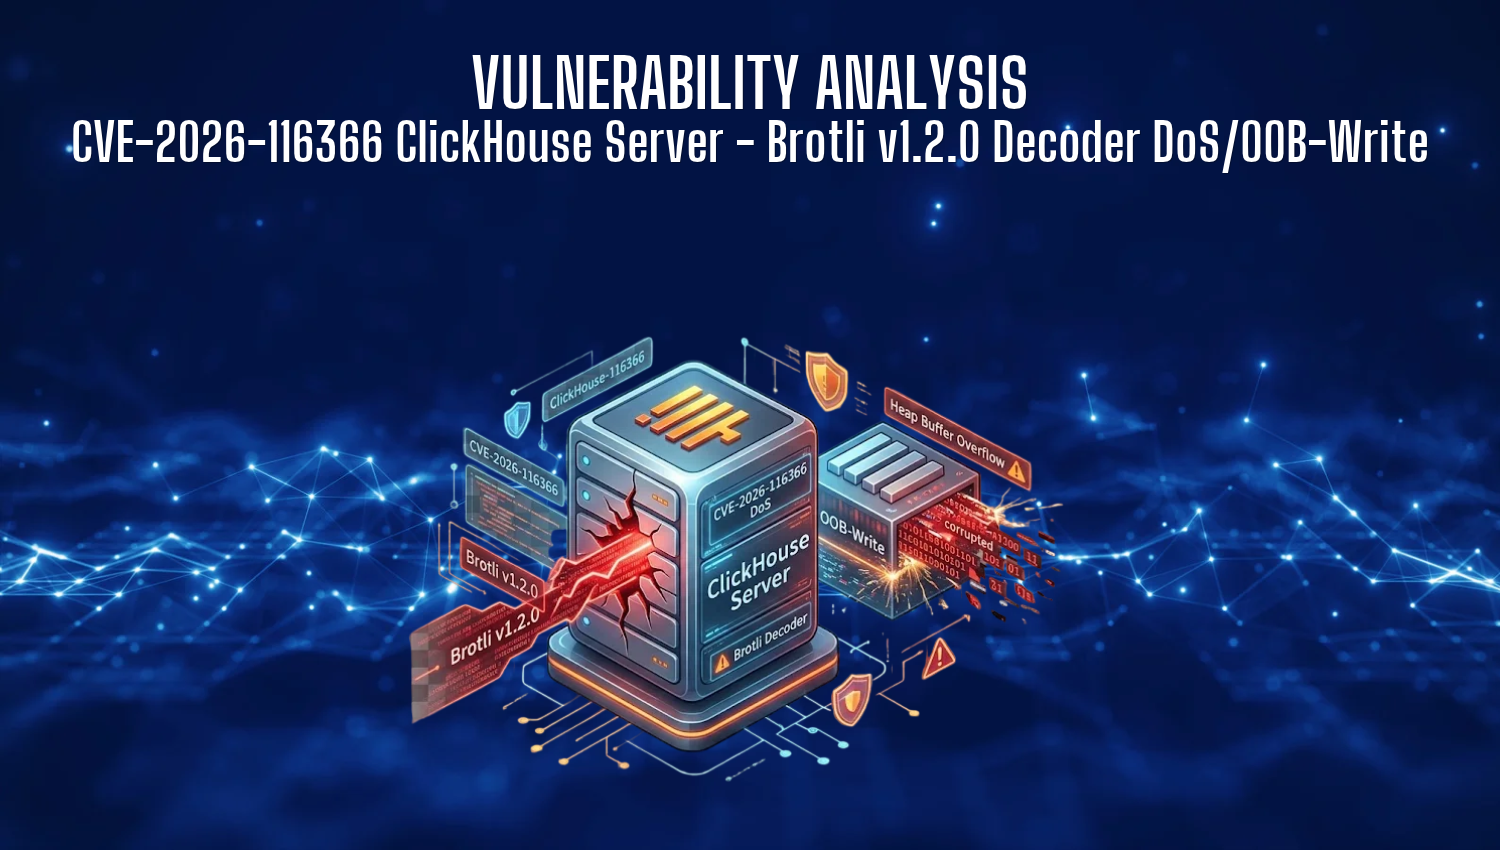
CVE-2026-116366

Introduction ClickHouse is a widely deployed, high-performance columnar database management system designed for online analytical processing (OLAP). To maintain its exceptional read and write speeds, ClickHouse relies heavily on efficient data compression algorithms, including Google’s Brotli library. CVE-2026-116366 represents a critical security flaw in how ClickHouse handles incoming Brotli-compressed payloads. This vulnerability exposes affected servers to unauthenticated Remote Code Execution (RCE) and Denial of

Vulnerability Analysis: CVE-2026-111497 Critical out-of-bounds write in the Node.js Brotli decoder

CVE-2026-111497

Introduction In modern web architectures, data compression plays a pivotal role in reducing network bandwidth consumption, optimizing server response times, and accelerating overall web content delivery across distributed networks. Brotli—a popular lossless data compression algorithm originally developed by Google—has quickly established itself as a ubiquitous open-source standard widely integrated across major web browsers, edge reverse proxies, content delivery networks (CDNs), and backend server

Pyngrok for White Hat Hackers: Rapid Deployment Scenarios in Security Testing

pyngrok for hackers

Introduction Speed, flexibility, and operational efficiency are critical in penetration testing and Red Team operations. Exposing a locally hosted awareness simulation page or testing infrastructure to external target systems typically requires router reconfigurations, port forwarding, or setting up cloud-based virtual private servers (VPS). These administrative obstacles often introduce unnecessary friction and delay execution during time-sensitive engagements. Ngrok eliminates these time-consuming setup steps by

Vulnerability Analysis: CVE-2026-116067 Paisa < 0.7.8 – Unauthenticated Path Traversal

CVE-2026-116067

Introduction In modern web applications, handling file paths securely is a critical requirement. When input fields accept file paths or file names directly without adequate validation, software can become susceptible to Directory Traversal (Path Traversal) flaws. CVE-2026-116067 represents a high-severity Path Traversal vulnerability discovered in Paisa—a popular open-source, self-hosted personal finance tracking application designed to help users manage their ledgers, budgets, and investments. Self-hosted financial

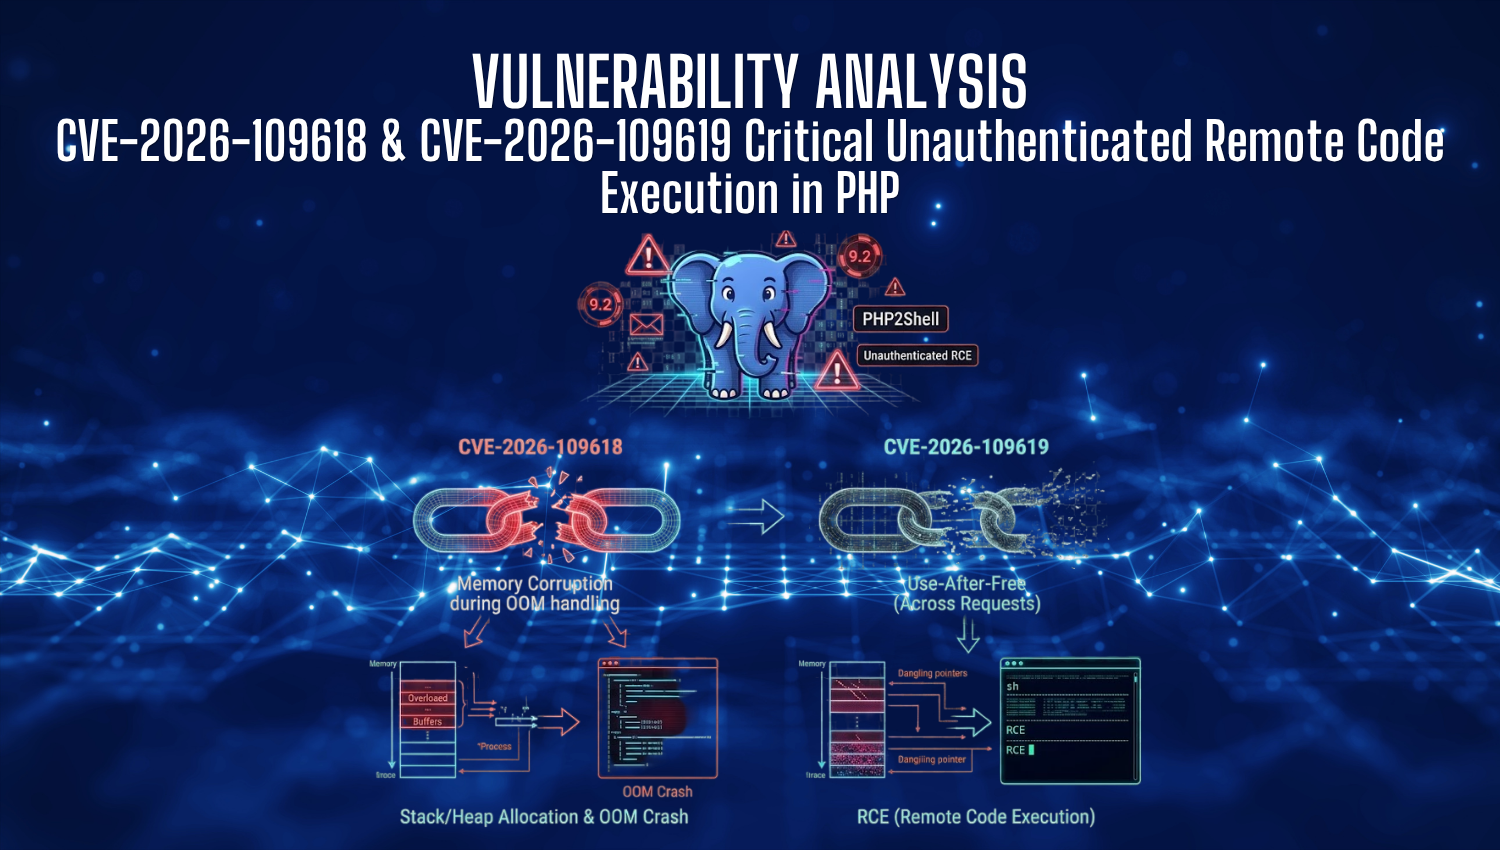
Vulnerability Analysis: CVE-2026-109618 & CVE-2026-109619 Critical Unauthenticated Remote Code Execution in PHP

Introduction CVE-2026-109618 and CVE-2026-109619 represent one of the most critical security emergencies in recent PHP history, threatening millions of active web servers globally. Highlighting the fundamental dangers of memory management flaws within persistent web server worker environments—such as PHP-FPM or Apache mod_php—these vulnerabilities enable unauthenticated remote attackers to execute arbitrary system commands with the privilege level of the

What You Need to Know About Ransomware Protection in 2026

What You Need to Know About Ransomware

Introduction As we navigate through 2026, the cybersecurity landscape has become more complex than ever. Ransomware has evolved from simple encryption scripts into highly sophisticated, AI-driven operations that target organizations of all sizes. Cybercriminals now leverage advanced automation, deepfakes, and triple-extortion tactics to maximize their impact. Staying ahead of these threats requires more than just basic antivirus software; it demands a comprehensive, proactive approach

Learning Cybersecurity with ChatGPT: An AI-Powered Beginner’s Guide

learning cybersecurity with chatgpt

Introduction Cybersecurity is a challenging and complex field to learn due to constantly evolving threats and advancing technologies. In the past, stepping into this industry required reading hundreds of pages of technical documentation and attending expensive training sessions. Today, thanks to Artificial Intelligence (AI), access to information has fundamentally changed. ChatGPT can transform into a 24/7 accessible personal tutor that simplifies complex

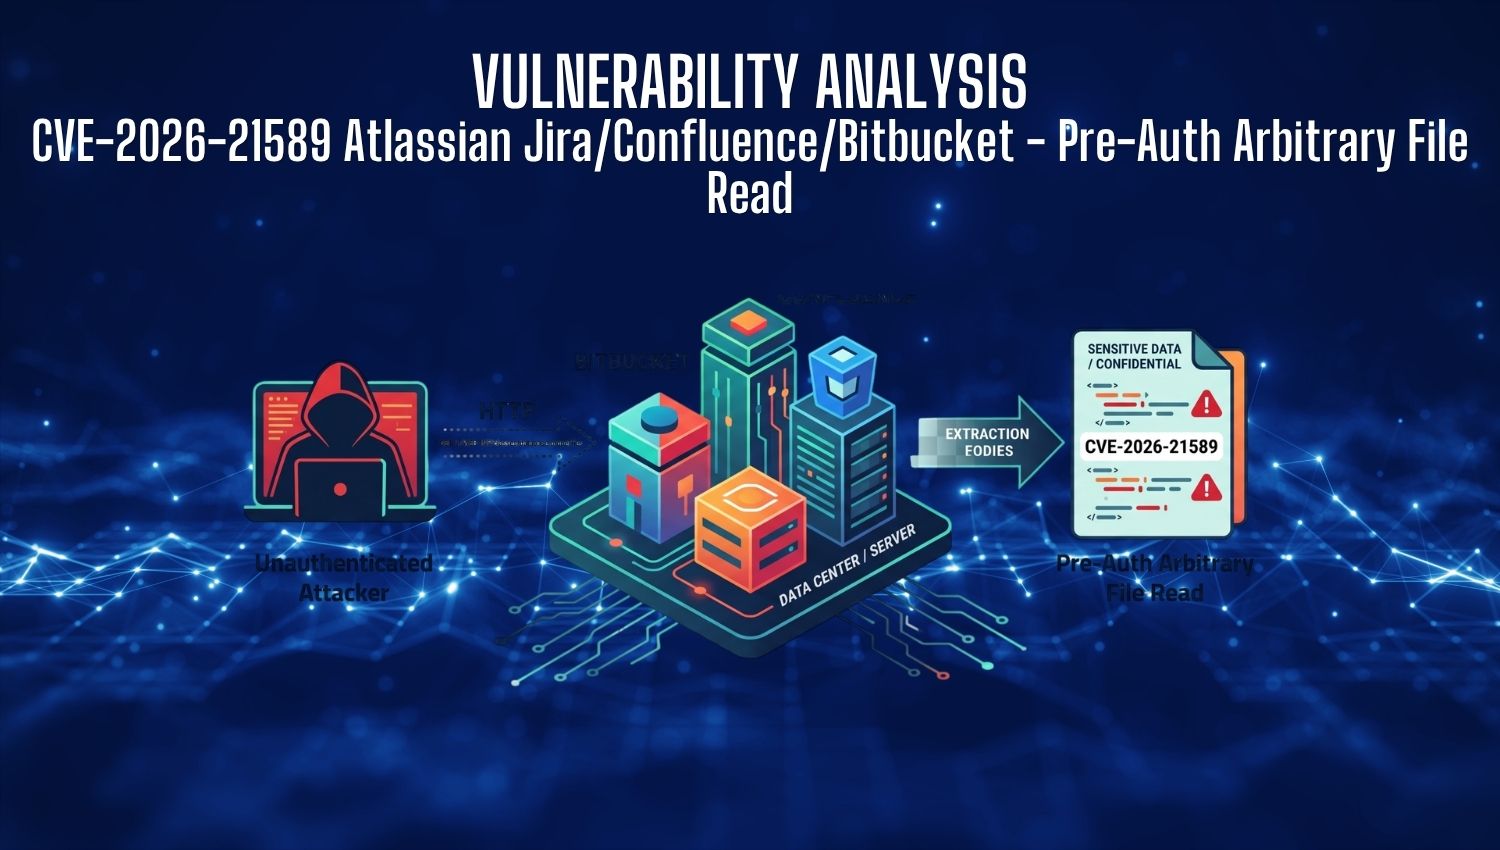
Vulnerability Analysis CVE-2026-21589 Atlassian Jira/Confluence/Bitbucket – Pre-Auth Arbitrary File Read

CVE-2026-21589

Introduction In October 2026, Atlassian issued an emergency security advisory disclosing CVE-2026-21589, a critical unauthenticated arbitrary file access vulnerability affecting its core self-hosted product suite. Assigned a CVSSv4 score of 9.3 (Critical), this security flaw allows unauthenticated remote threat actors to read arbitrary files directly from target system directories. Unauthenticated arbitrary file read vulnerabilities represent a severe risk to enterprise infrastructure because

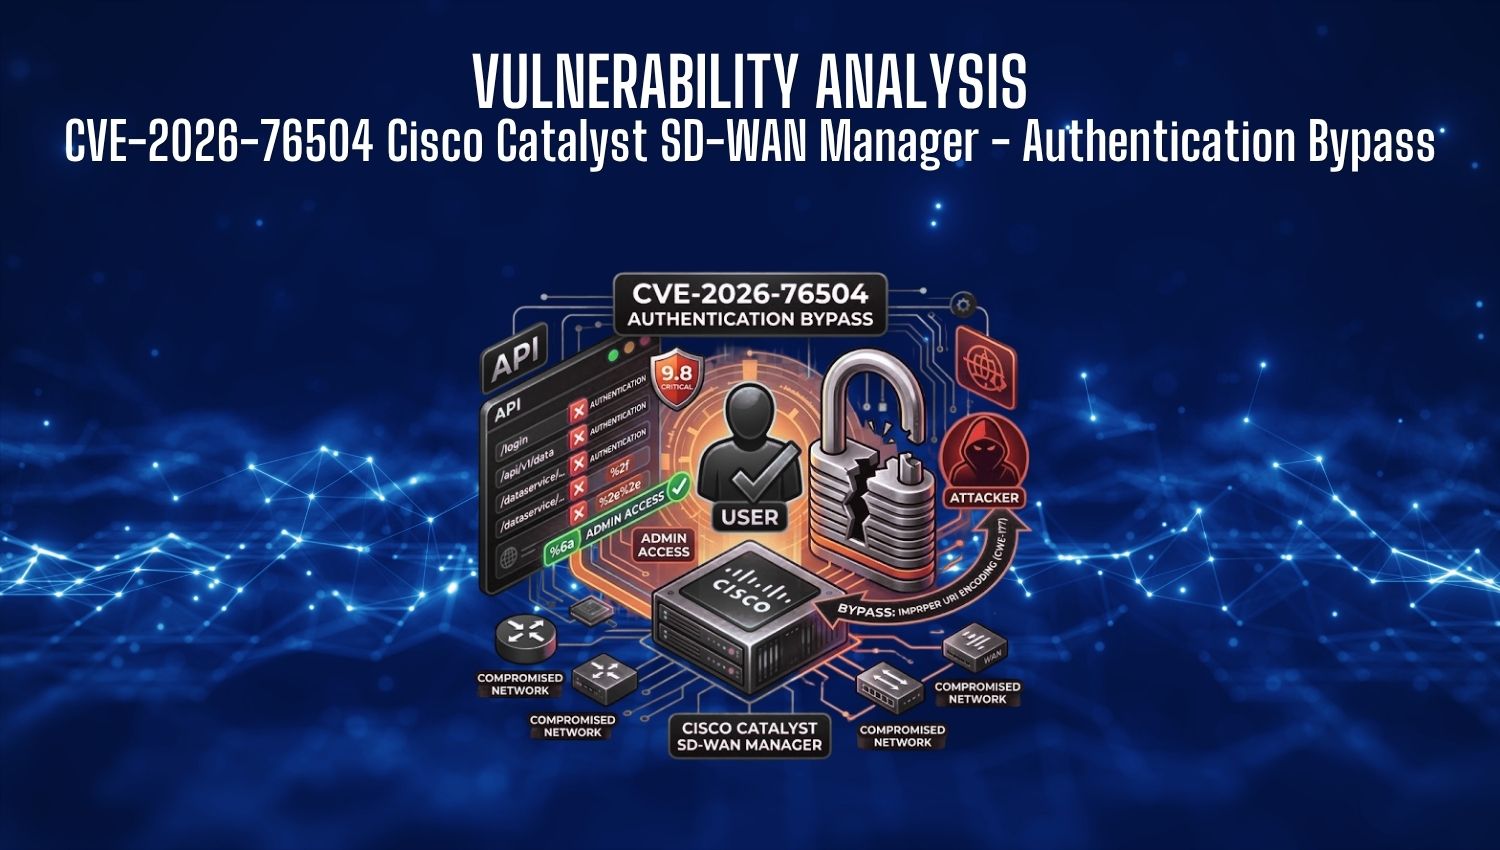
Vulnerability Analysis CVE-2026-76504 Cisco Catalyst SD-WAN Manager – Authentication Bypass

CVE-2026-76504 Cisco Catalyst SD-WAN Manager - Authentication Bypass

Introduction Centralized management platforms serve as the core control plane for modern enterprise network architectures, providing a single pane of glass for multi-cloud and wide-area network management. Cisco Catalyst SD-WAN Manager (formerly known as vManage) enables network administrators to configure, monitor, automate, and orchestrate complex enterprise wide-area networks across global deployments from a unified web interface. Because this platform possesses full administrative authority