Vulnerability Analysis CVE-2026-87902 WordPress Core – PHP Template Path Traversal
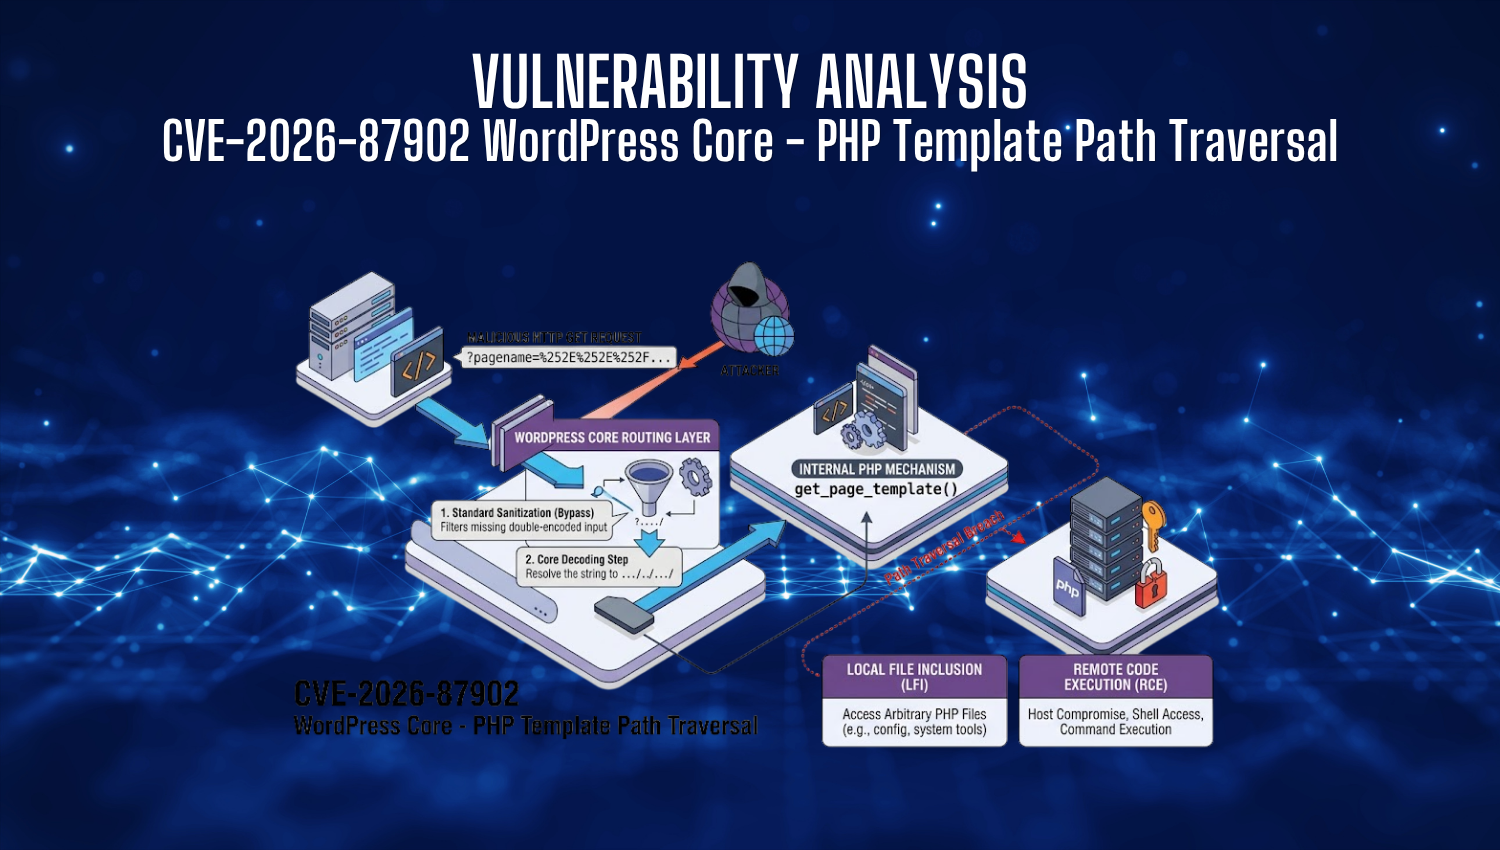
CVE-2026-87902 WordPress Core - PHP Template Path Traversal

Introduction The global cybersecurity community witnessed a significant shift in threat metrics when a severe, unauthenticated security flaw within WordPress Core was disclosed. Designated as CVE-2026-87902, this critical flaw impacts tens of millions of active web applications dependent on the open-source Content Management System (CMS). Assigning it a CVSS v4.0 rating of 9.2 (Critical), security threat intelligence teams flagged the vulnerability for its
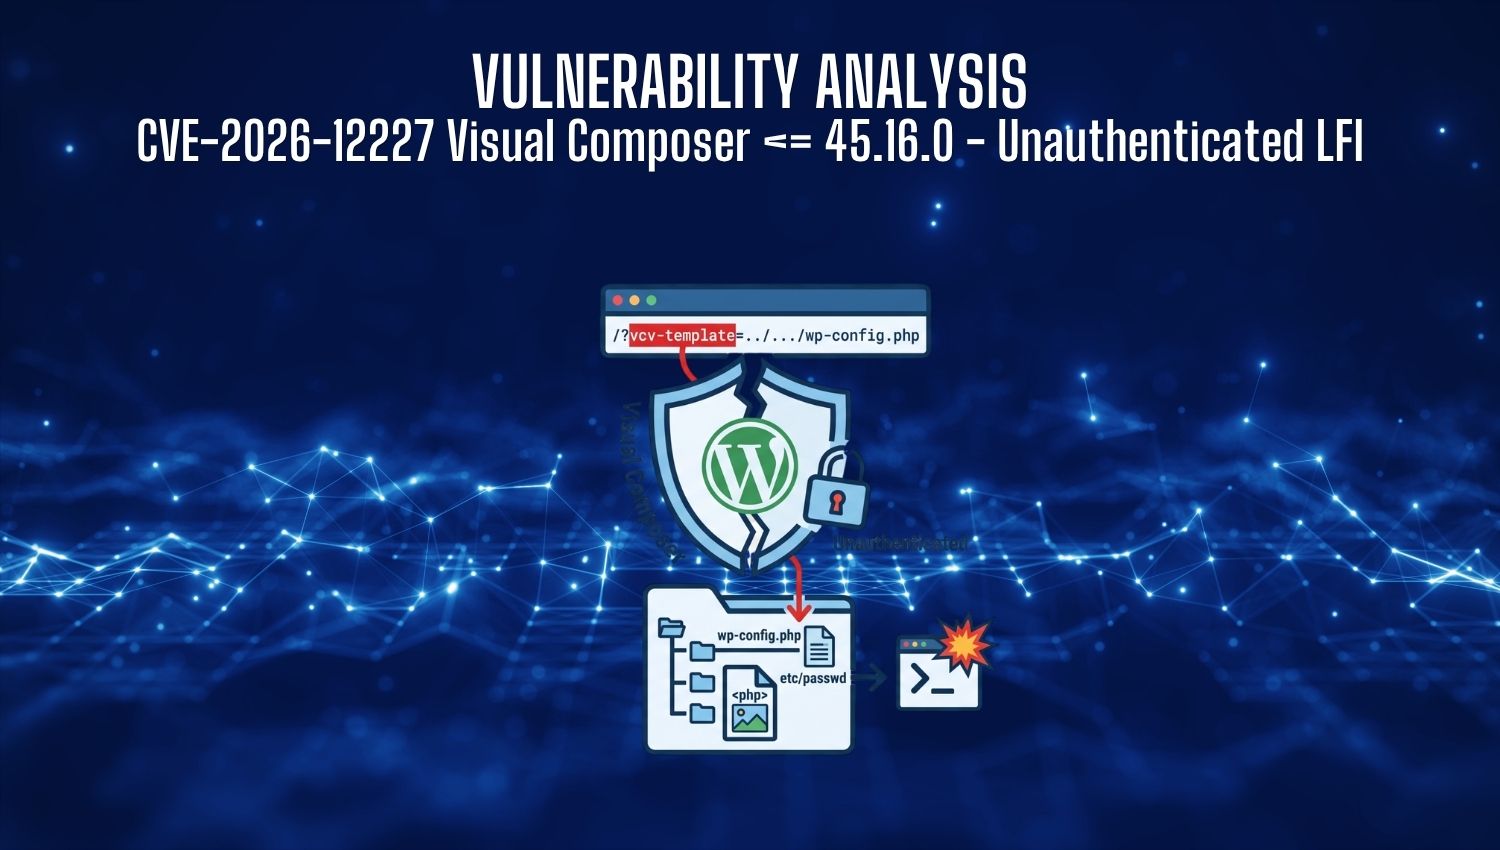
Vulnerability Analysis: CVE-2026-12227 Visual Composer <= 45.16.0 – Unauthenticated LFI

CVE-2026-12227

Introduction In the landscape of web application security, WordPress plugins are frequently targeted due to their widespread deployment. The Visual Composer Website Builder, a highly popular page builder plugin for WordPress, was found to contain a critical security flaw designated as CVE-2026-12227. This vulnerability, affecting versions up to and including 45.16.0, allows unauthenticated attackers to exploit a Local File Inclusion (LFI) vulnerability. Due to its

The Hidden Gateway to Enterprise Networks: Unbound DNS Flaw and the Threat to Global Resolvers

Unbound DNS Flaw and the Threat to Global Resolvers

Introduction The Domain Name System functions as the foundational directory of global internet infrastructure, silently resolving human-readable hostnames into network addresses. However, severe memory management flaws and improper packet parsing within DNSSEC (Domain Name System Security Extensions) validation modules can instantly transform these trusted recursive resolvers into high-impact entry points for adversary breach campaigns. Officially tracked as CVE-2026-81642 and publicly disclosed by NLnet

Vulnerability Analysis: CVE-2026-76461 – Critical Cisco Secure Email Gateway Vulnerability Exploited

CVE-2026-76461 Critical Cisco Secure Email Gateway Vulnerability Exploited

Introduction Email remains one of the primary vectors for enterprise cyberattacks, making secure email gateways critical perimeter defenses. Recently, a severe security flaw identified as CVE-2026-76461 was discovered in Cisco Secure Email Gateway (formerly Cisco Email Security Appliance / ESA). Rated with a maximum-severity CVSS score of 9.8 (Critical), this vulnerability allows unauthenticated, remote attackers to execute arbitrary commands at the highest system privileges. Both Cisco and the

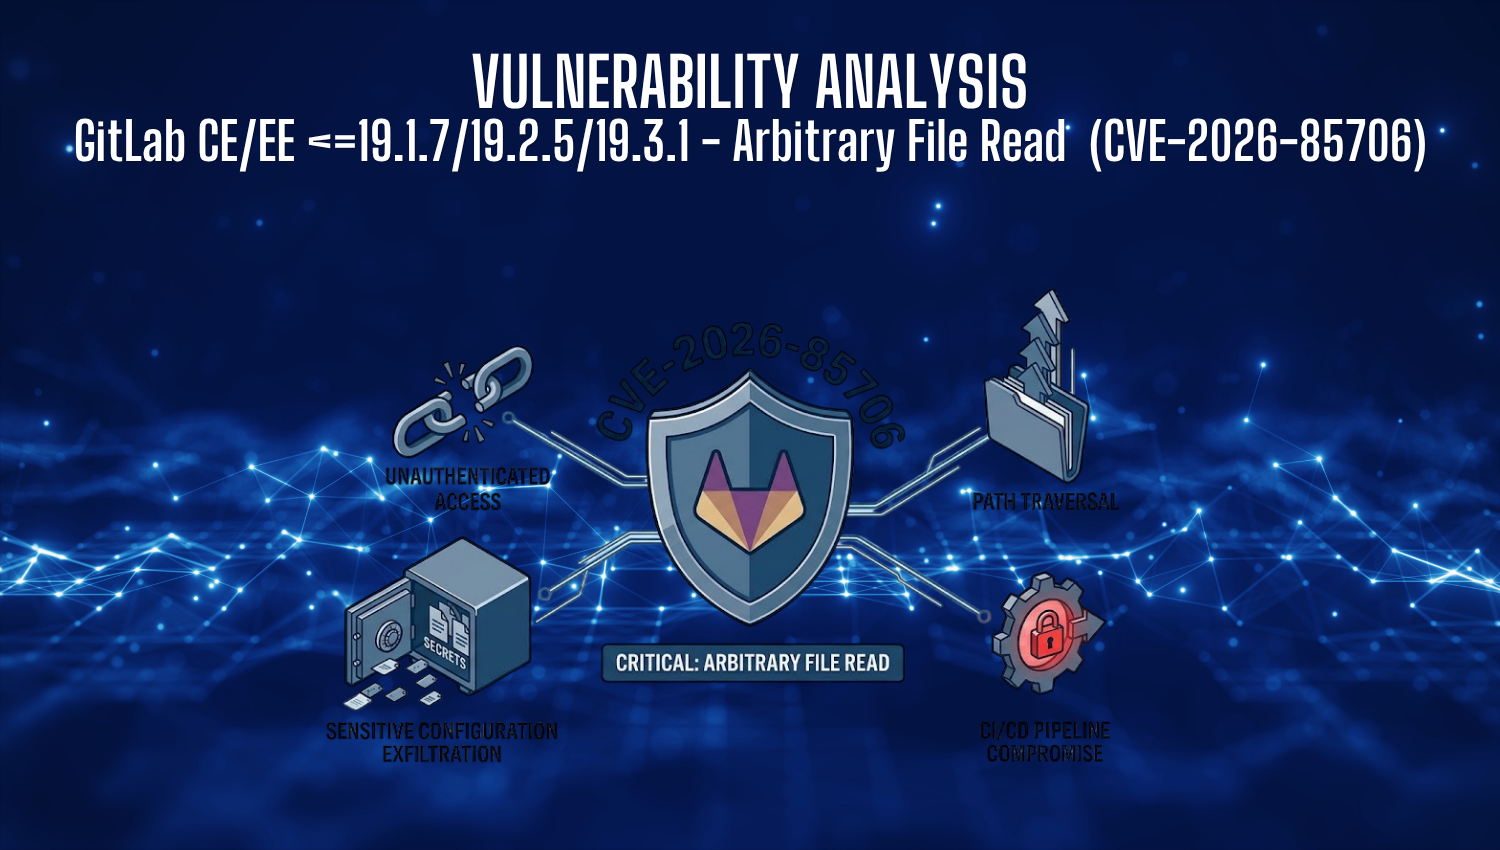
Vulnerability Analysis CVE-2026-85706 GitLab – Arbitrary File Read

CVE-2026-85706 GitLab

Introduction Security flaws in critical software development and deployment infrastructure pose a significant, far-reaching risk to modern organizational supply chains. GitLab, an open-source DevOps platform used worldwide for source code management and continuous integration/continuous deployment (CI/CD) pipelines, released emergency security updates addressing CVE-2026-85706. This maximum-severity vulnerability—rated at CVSS 10.0—allows unauthenticated remote attackers to read arbitrary files directly from the host file system

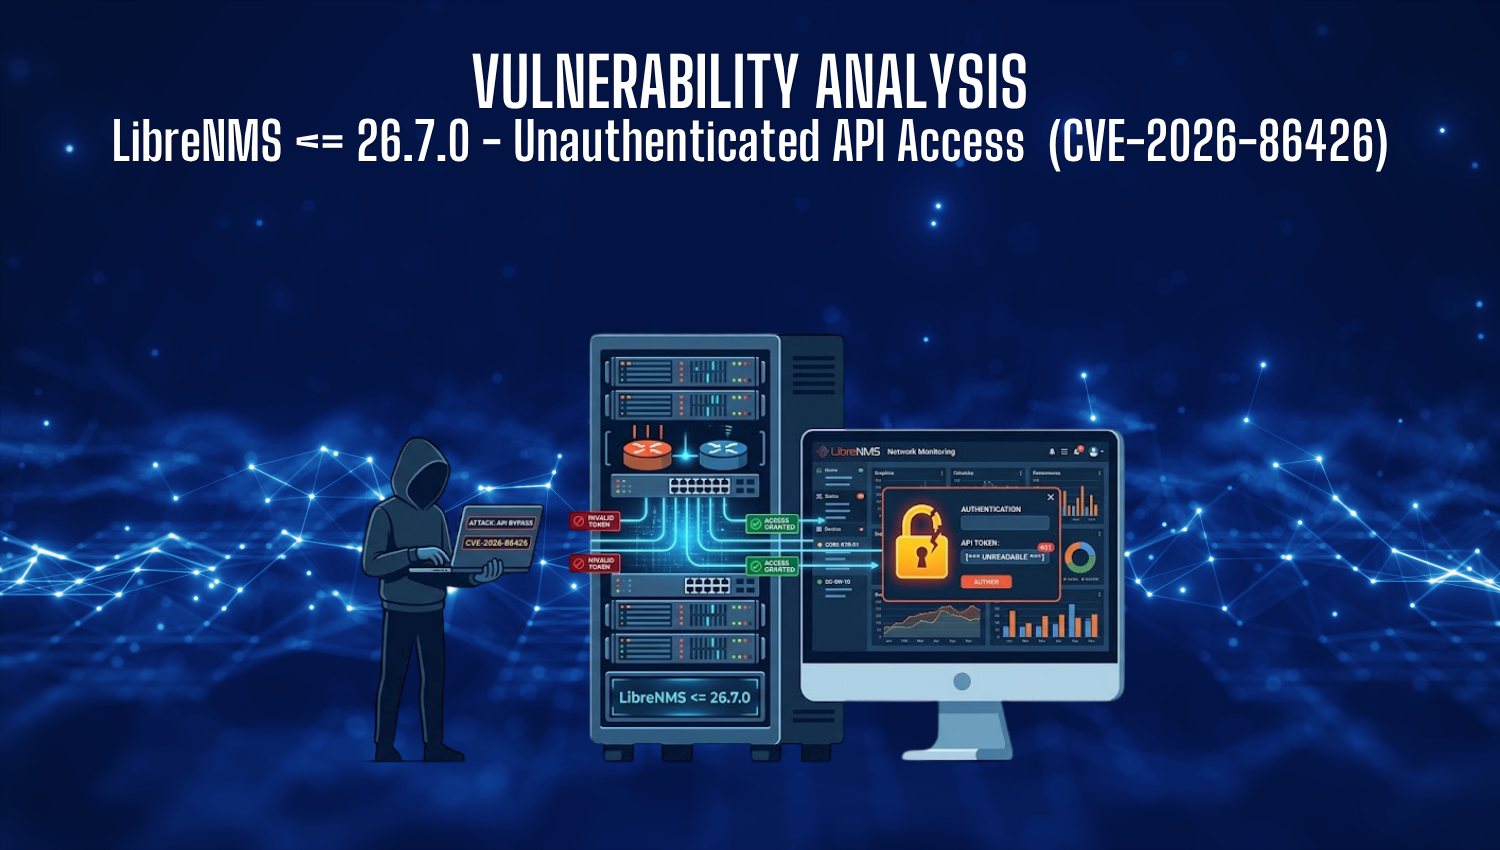
Vulnerability Analysis: CVE-2026-86426 LibreNMS <= 26.7.0 – Unauthenticated API Access

CVE-2026-86426 LibreNMS

Introduction CVE-2026-86426 represents a critical authentication bypass vulnerability affecting LibreNMS network monitoring installations running version 26.7.0 or earlier. Publicly disclosed and addressed in late 2026, the vulnerability received a severe CVSS v4.0 rating of 9.2 (Critical) due to its low attack complexity and high impact. The underlying flaw resides within the API authentication middleware, which fails to strictly enforce parameter types during input

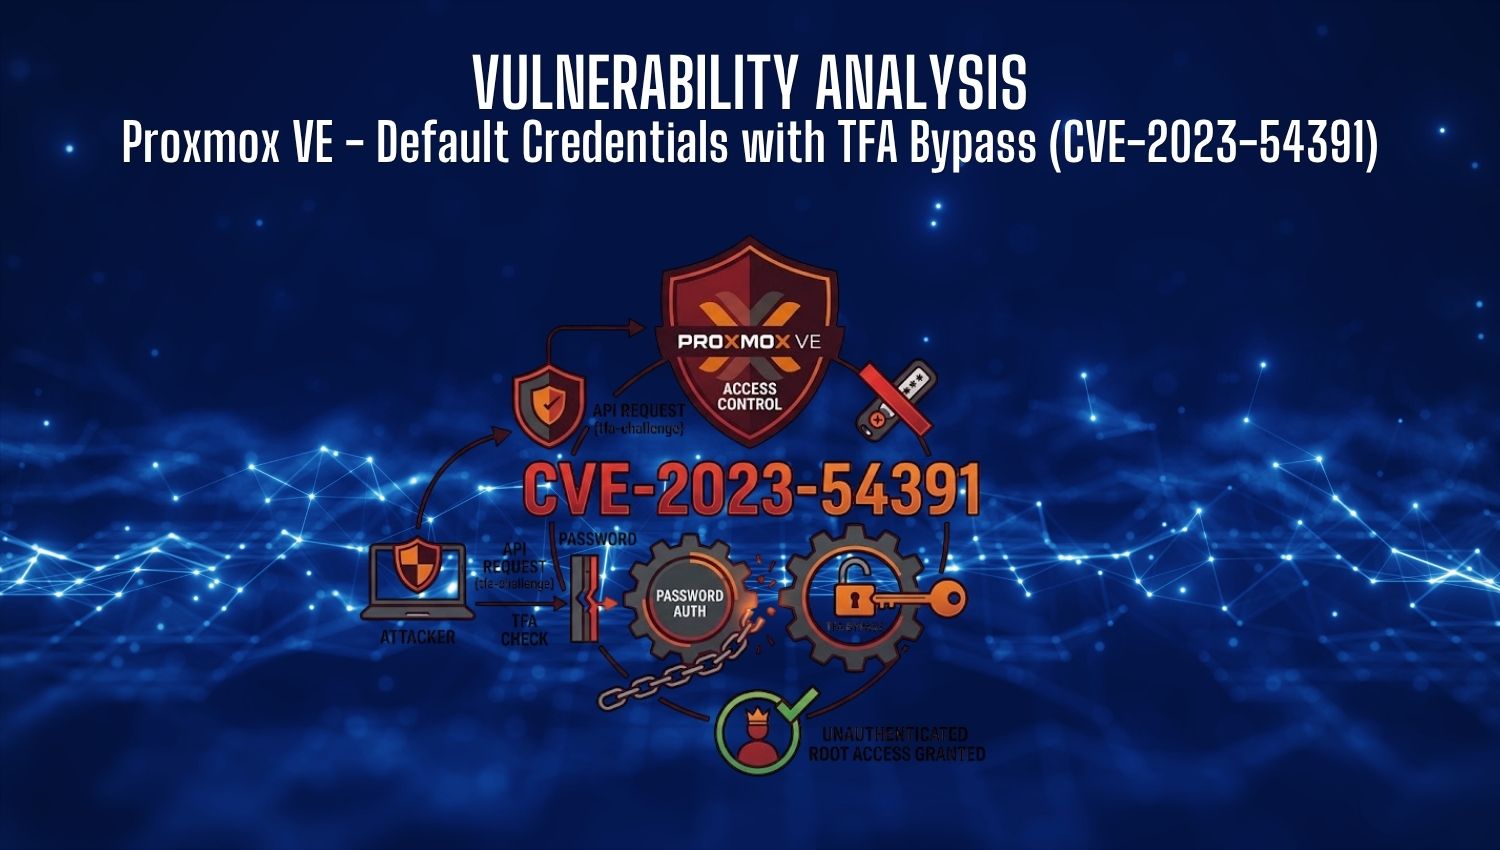
Vulnerability Analysis: Proxmox VE – Default Credentials with TFA Bypass (CVE-2023-54391)

Proxmox VE - Default Credentials with TFA Bypass (CVE-2023-54391)

Introduction CVE-2023-54391 represents a critical pre-authentication authentication bypass vulnerability in Proxmox Virtual Environment (PVE). Operating at a CVSS 3.1 score of 9.8 (Critical), this security flaw allows unauthenticated remote attackers to completely bypass standard password authentication mechanisms. By manipulating parameters in the login API endpoint, an attacker can gain full superuser (root@pam) access to the underlying hypervisor management plane without knowing the victim

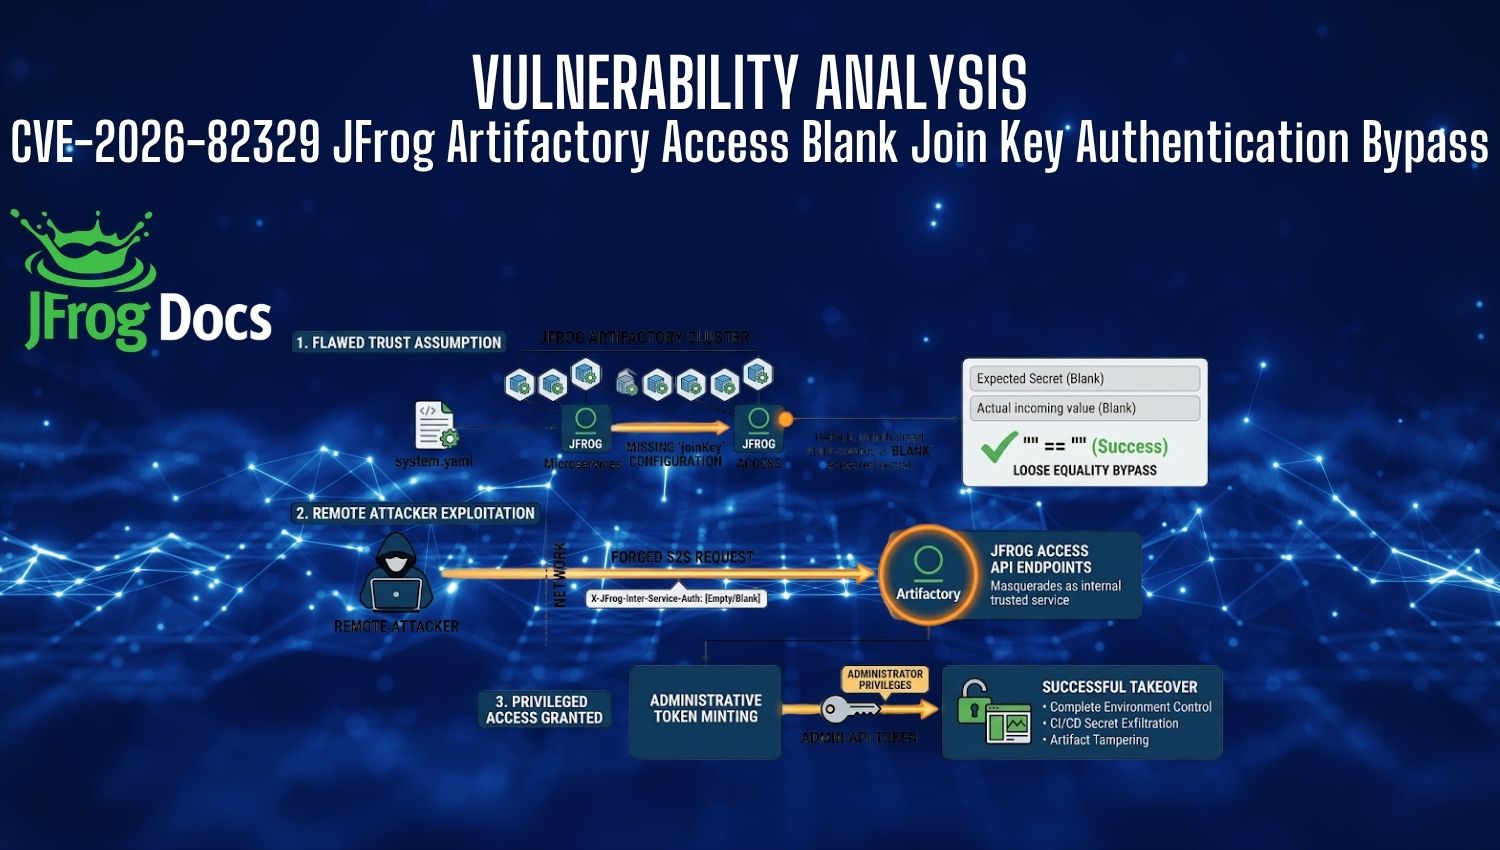
Vulnerability Analysis: CVE-2026-82329 JFrog Artifactory Access Authentication Bypass

CVE-2026-82329 JFrog Artifactory Access Blank Join Key Authentication Bypass

Introduction JFrog Artifactory serves as a central pillar in modern software engineering, providing universal artifact management across continuous integration and continuous delivery (CI/CD) pipelines. Given its privileged position—storing sensitive binaries, container images, AI models, and proprietary source code dependencies—a breach within Artifactory poses significant supply chain risks to global digital infrastructure. Disclosed in late August 2026, CVE-2026-82329 represents a critical security flaw rated 9.8 (Critical) under CVSS

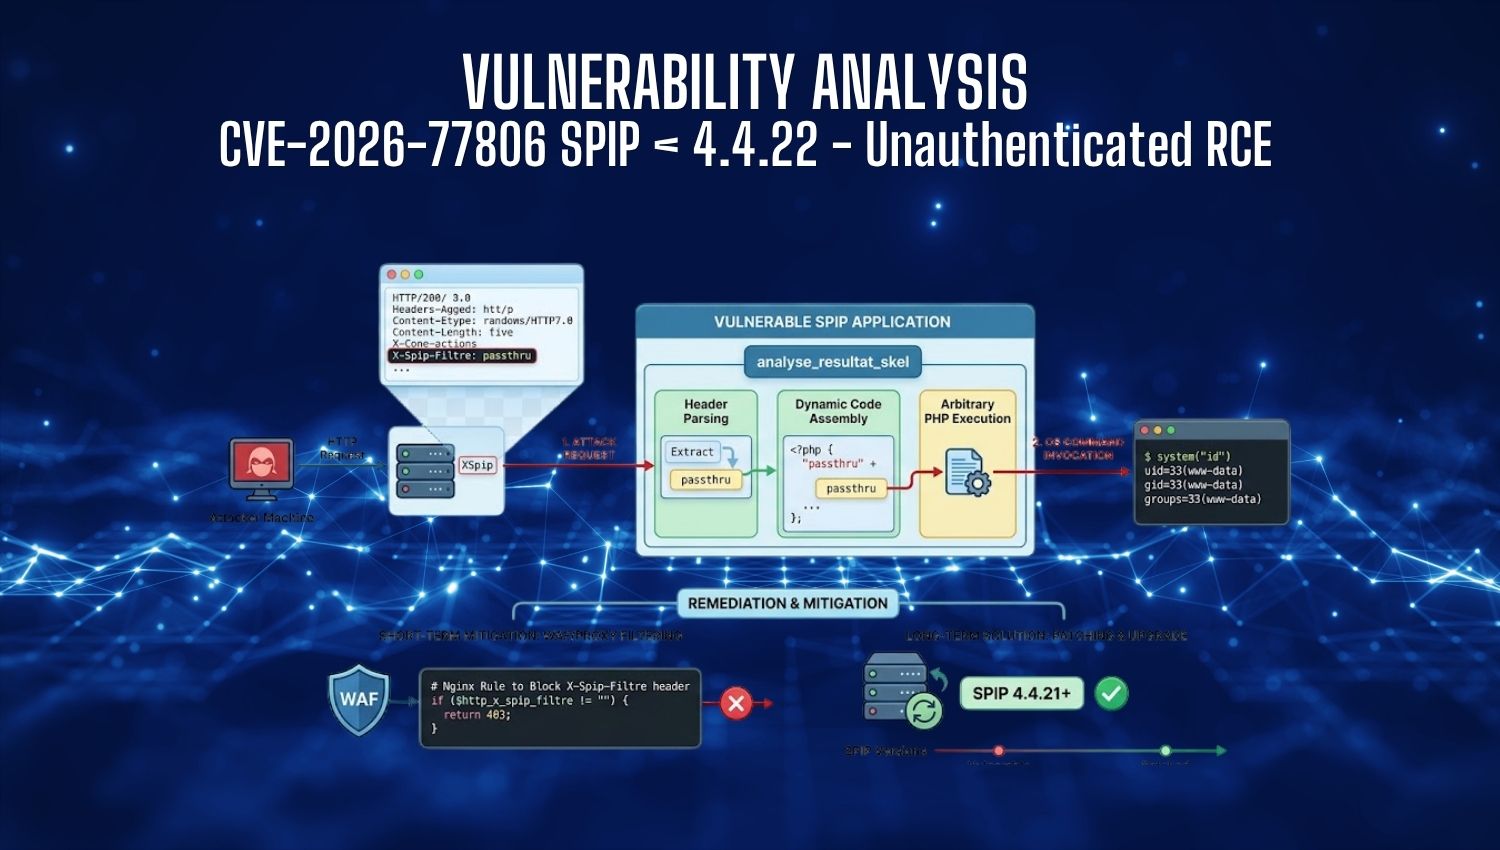
Vulnerability Analysis: SPIP < 4.4.22 – Unauthenticated RCE (CVE-2026-77806)

CVE-2026-77806 SPIP RCE

Introduction Content Management Systems (CMS) form the backbone of millions of web applications worldwide. When a critical vulnerability surfaces within a core CMS framework, the potential blast radius is immense. CVE-2026-77806 represents one such severe threat—a critical, unauthenticated Remote Code Execution (RCE) flaw affecting the SPIP publishing framework in versions prior to 4.4.21. Achieving a CVSS score of 9.8 (Critical), this vulnerability allows unauthenticated remote attackers to

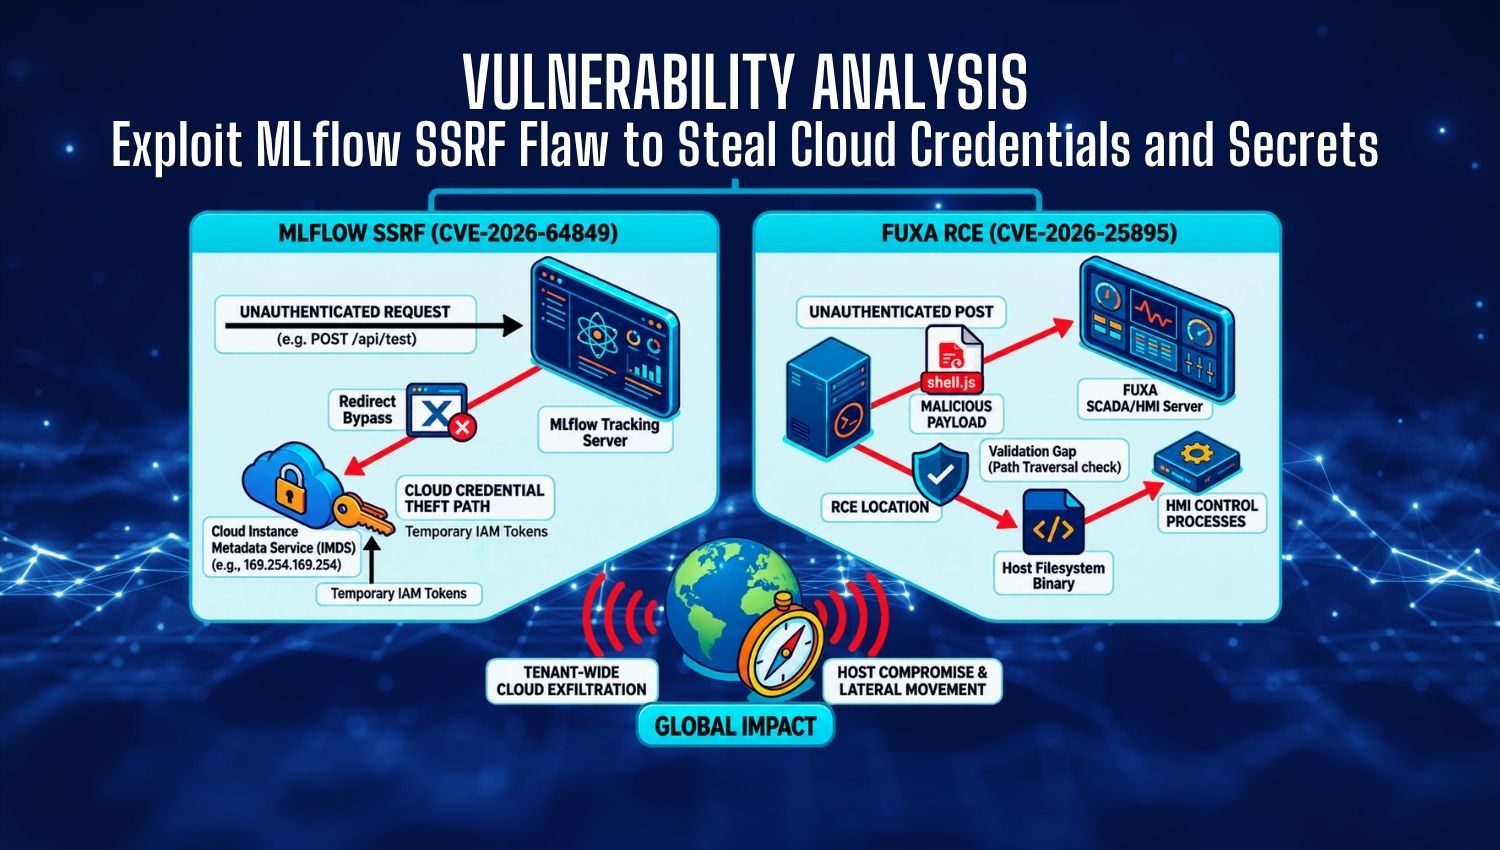
Unauthenticated Infrastructure Exploitation: From MLflow SSRF to SCADA Remote Code Execution

Exploit MLflow SSRF Flaw to Steal Cloud Credentials and Secrets

Introduction Recent security intelligence highlights a wave of sophisticated attacks targeting exposed enterprise infrastructure across modern cloud environments and industrial networks. Threat actors are actively hunting for internet-facing assets to establish initial footholds, systematically weaponizing unauthenticated vulnerabilities in popular AI lifecycle platforms and critical industrial automation systems. By abusing missing access controls and flawed input validation mechanisms, remote attackers