Vulnerability Analysis: CVE-2026-63077 Unauthenticated Remote Code Execution in JetBrains TeamCity
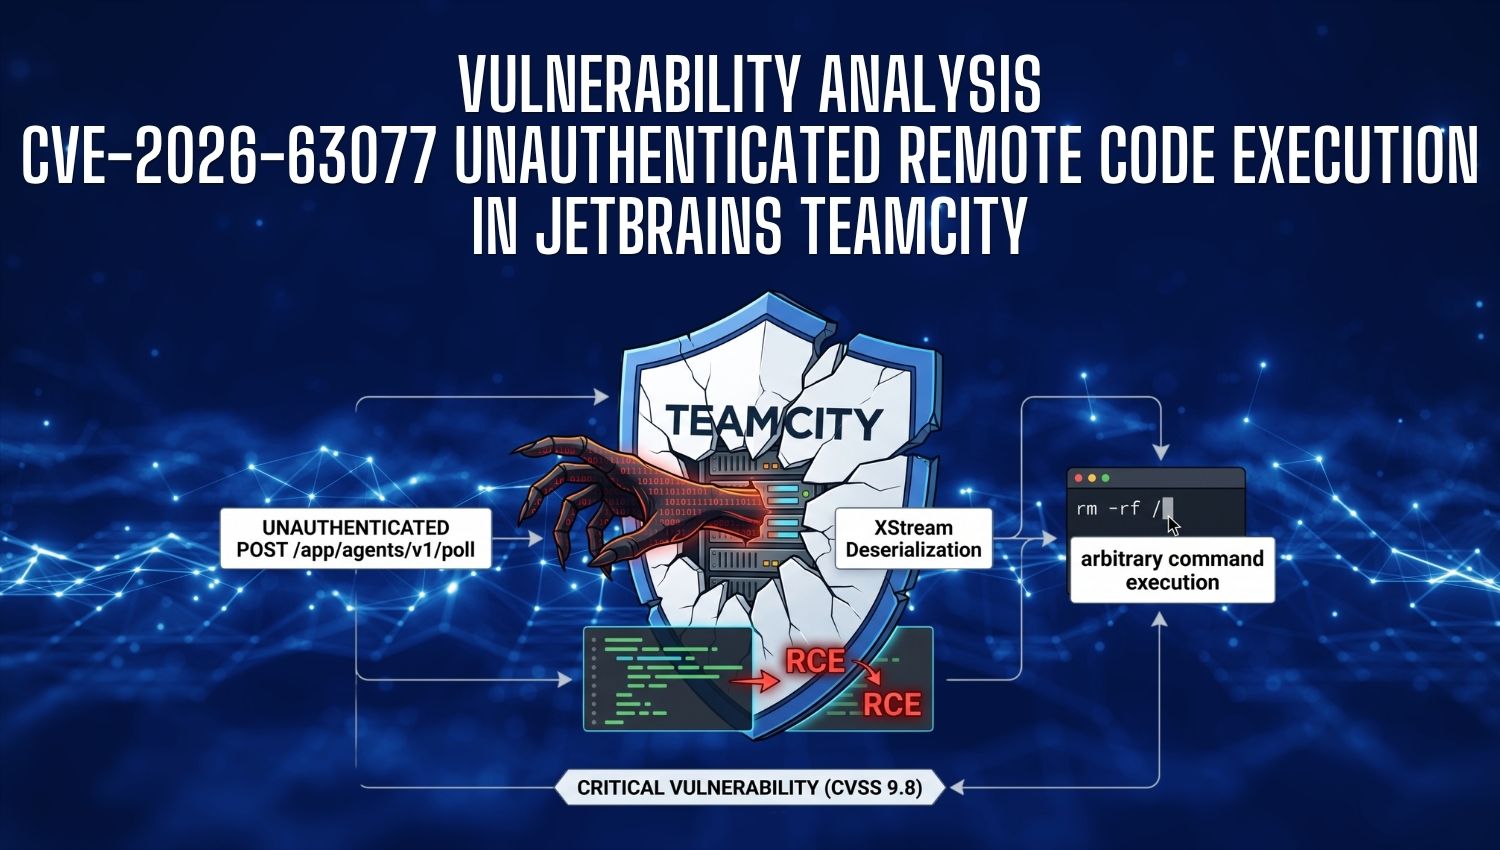
CVE-2026-63077 UnauthentIcated Remote Code ExecutIon In JetBraIns TeamCIty

Introduction On August 5, 2026, cybersecurity researchers disclosed a critical security vulnerability designated as CVE-2026-63077 (CVSS v3.1 Score: 9.8 – Critical) affecting JetBrains TeamCity On-Premises installations. TeamCity is one of the world’s most widely adopted Continuous Integration and Continuous Deployment (CI/CD) server solutions, serving as the core infrastructure for source code compilation, secret storage, and automated deployment pipelines across enterprise environments. CVE-2026-63077 represents an unauthenticated Remote Code Execution (RCE) vulnerability that allows
The Ultimate Guide to 360 TryHackMe Free Rooms: Master Cybersecurity for Free

Remote Active Directory Pentesting A Comprehensive Overview

Introduction Starting a career in cybersecurity can feel like standing at the foot of an impossibly tall mountain. With endless sub-fields—ranging from web application security and digital forensics to reverse engineering, malware analysis, and cloud security—it is remarkably easy for beginners to feel overwhelmed about where to start, which path to follow, and what skills to prioritize. Fortunately, hands-on platforms like TryHackMe (THM) have

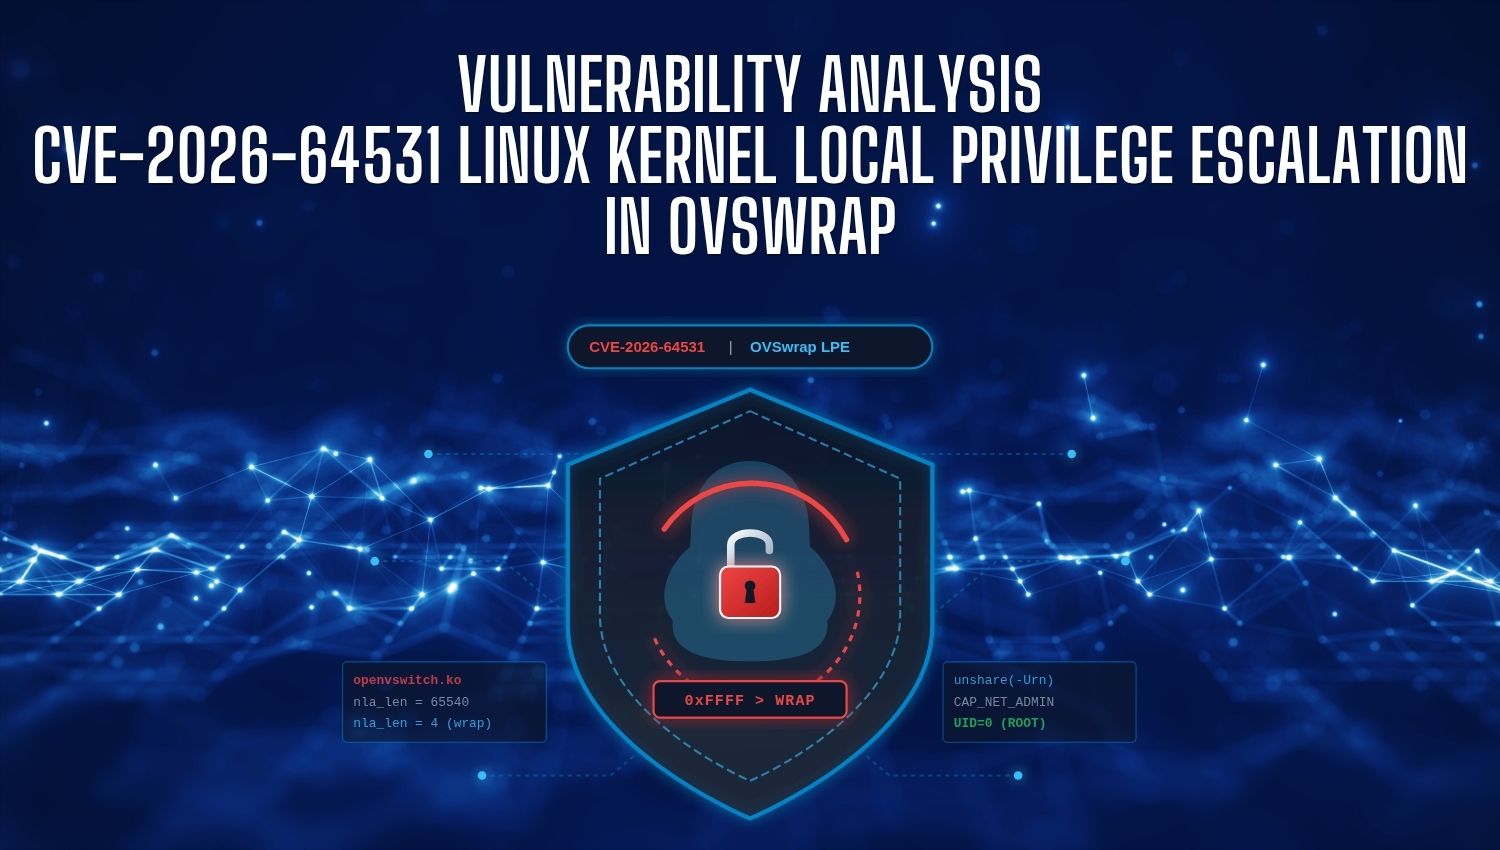
Vulnerability Analysis: CVE-2026-64531 Linux Kernel Local Privilege Escalation in OVSwrap

CVE-2026-64531 LInux Kernel Local PrIvIlege EscalatIon In OVSwrap

Introduction In modern enterprise cloud environments, multi-tenant container orchestration platforms, and heavily virtualized infrastructure, security isolation relies fundamentally on rigid Linux kernel boundaries and software-defined networking components. A newly disclosed vulnerability designated as CVE-2026-64531 (dubbed OVSwrap) poses a critical threat to system integrity and data confidentiality across enterprise Linux deployments. Discovered by security researcher Asim Manizada, OVSwrap allows unprivileged local users, low-privilege service accounts, or

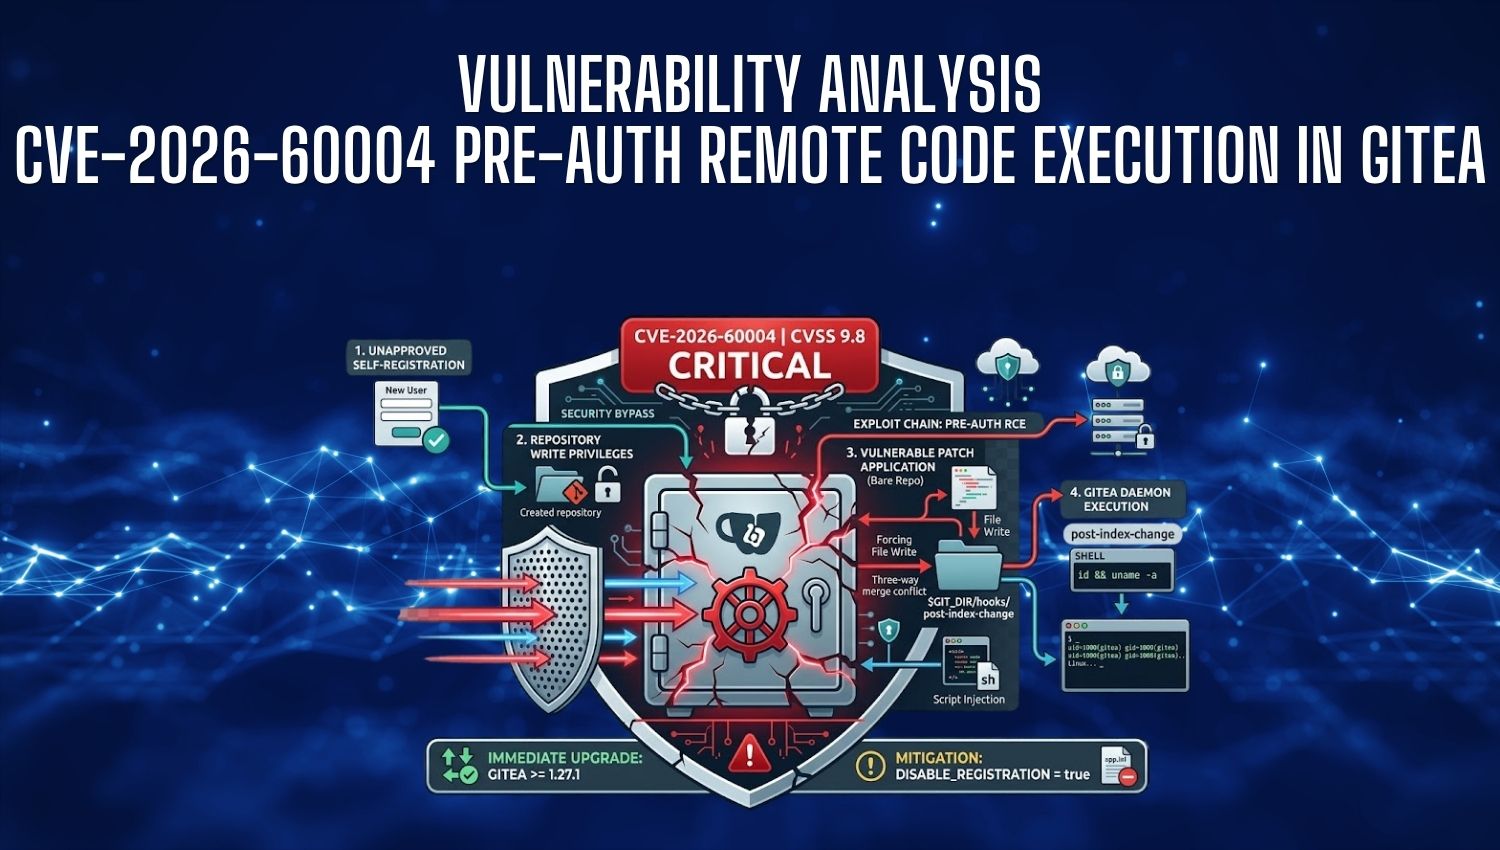
Vulnerability Analysis: CVE-2026-60004 Pre-Auth Remote Code Execution in Gitea

CVE-2026-60004 Pre-Auth Remote Code Execution in Gitea

Introduction Securing self-hosted version control platforms is critical for maintaining the integrity of modern software development pipelines, source code repositories, and automated CI/CD workflows. Gitea, a lightweight and widely adopted self-hosted Git service, recently addressed a critical security vulnerability identified as CVE-2026-60004. Carrying a maximum CVSS v3 score of 9.8 (Critical), this flaw enables unauthenticated remote attackers under default system configurations to achieve arbitrary

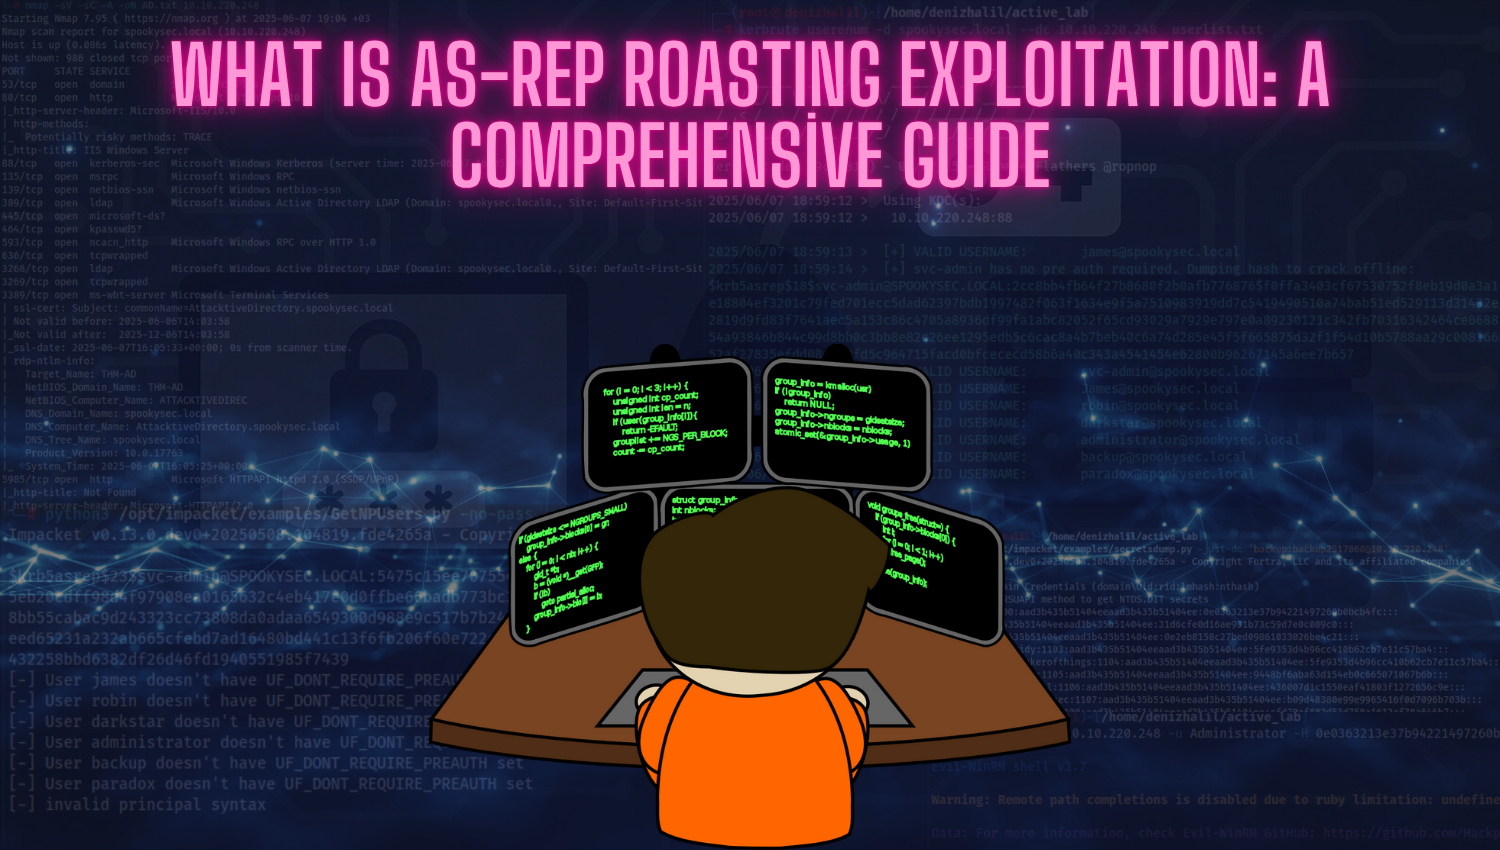
What is AS-REP Roasting Exploitation: A Comprehensive Guide

Introduction AS-REP Roasting is a critical attack technique that exploits a fundamental misconfiguration in Kerberos authentication, particularly within Active Directory environments. This sophisticated attack specifically targets user accounts where Kerberos pre-authentication has been disabled, allowing attackers to extract and crack user password hashes offline without triggering account lockouts or generating significant security alerts. In modern enterprise networks, Active Directory serves

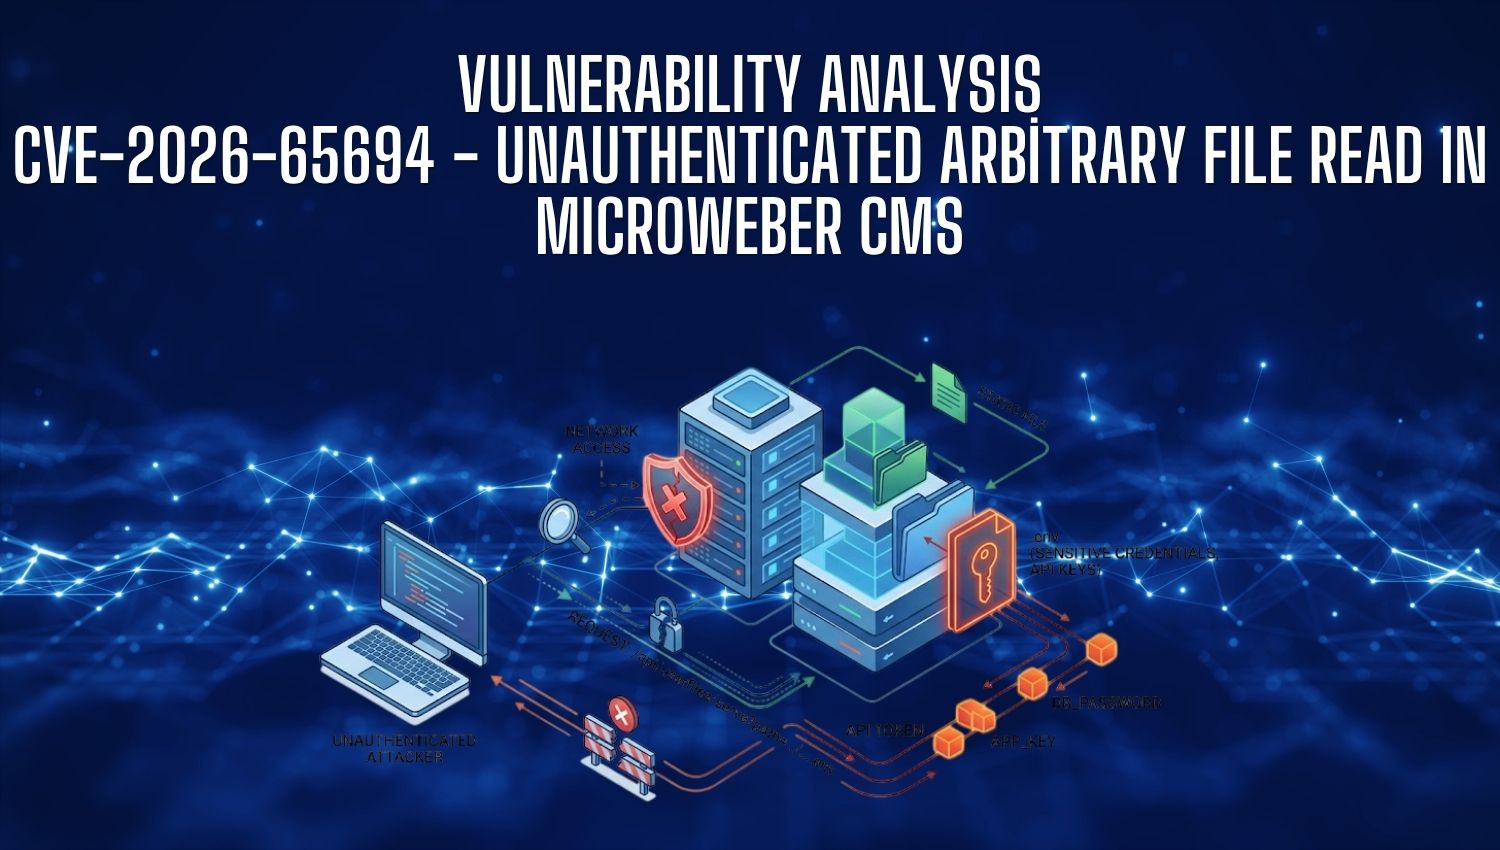
Vulnerability Analysis: CVE-2026-65694 – Unauthenticated Arbitrary File Read in Microweber CMS

Vulnerability Analysis CVE-2026-65694

Introduction Content Management Systems (CMS) form the backbone of modern web applications, handling everything from content publishing and dynamic page creation to user administration and media file management. However, this centralized functionality also presents an attractive attack surface for malicious actors when input sanitization mechanisms fail. When input validation fails within core controllers that serve assets or files, the security impact on

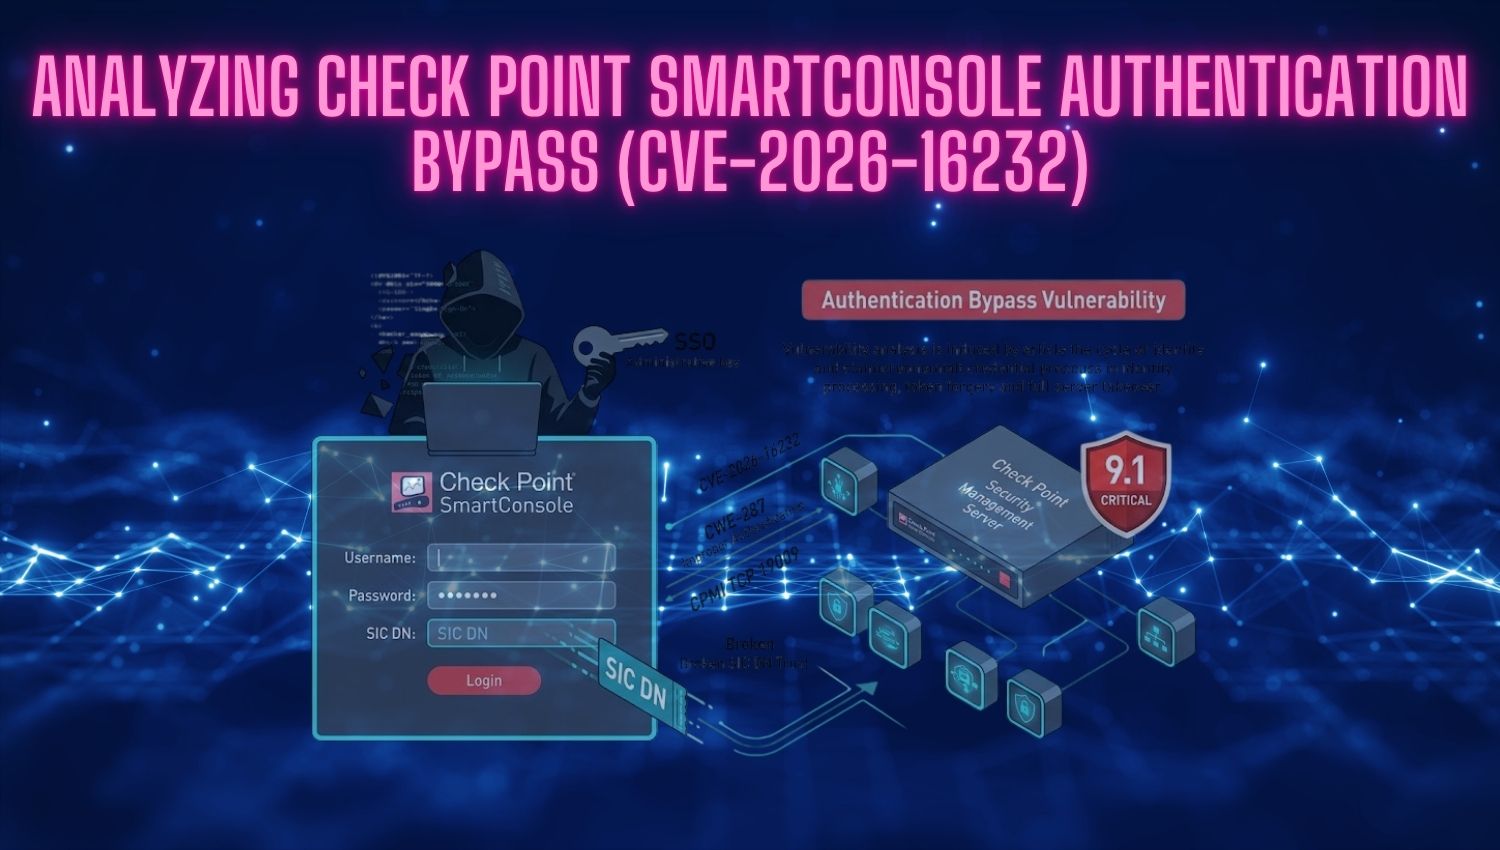
Analyzing Check Point SmartConsole Authentication Bypass (CVE-2026-16232)

AnalyzIng Check PoInt SmartConsole AuthentIcatIon Bypass (CVE-2026-16232)

Introduction Check Point Security Management Servers and Multi-Domain Security Management (MDS) platforms serve as the central control plane for enterprise network security. They manage security policies, threat prevention rules, user directories, and gateway configurations across global corporate environments. A critical vulnerability designated as CVE-2026-16232 was discovered within these systems, drastically elevating organizational risk. This flaw allows unauthenticated remote attackers to completely bypass SmartConsole authentication mechanisms, forge administrative

Certighost (CVE-2026-54121): How Low-Privilege Users Impersonate Domain Controllers

Certighost (CVE-2026-54121) How Low-Privilege Users Impersonate Domain Controllers

Introduction Active Directory Certificate Services (AD CS) serves as a foundational component in modern enterprise identity environments, facilitating public key infrastructure (PKI), machine authentication, VPN access, and smart card logins. However, misconfigurations and deep-seated flaws in how Enterprise Certificate Authorities (CAs) process incoming certificate requests or resolve directory objects can create severe privilege escalation vectors. The Certighost vulnerability (CVE-2026-54121) exposes a critical breakdown in this identity trust boundary, allowing an

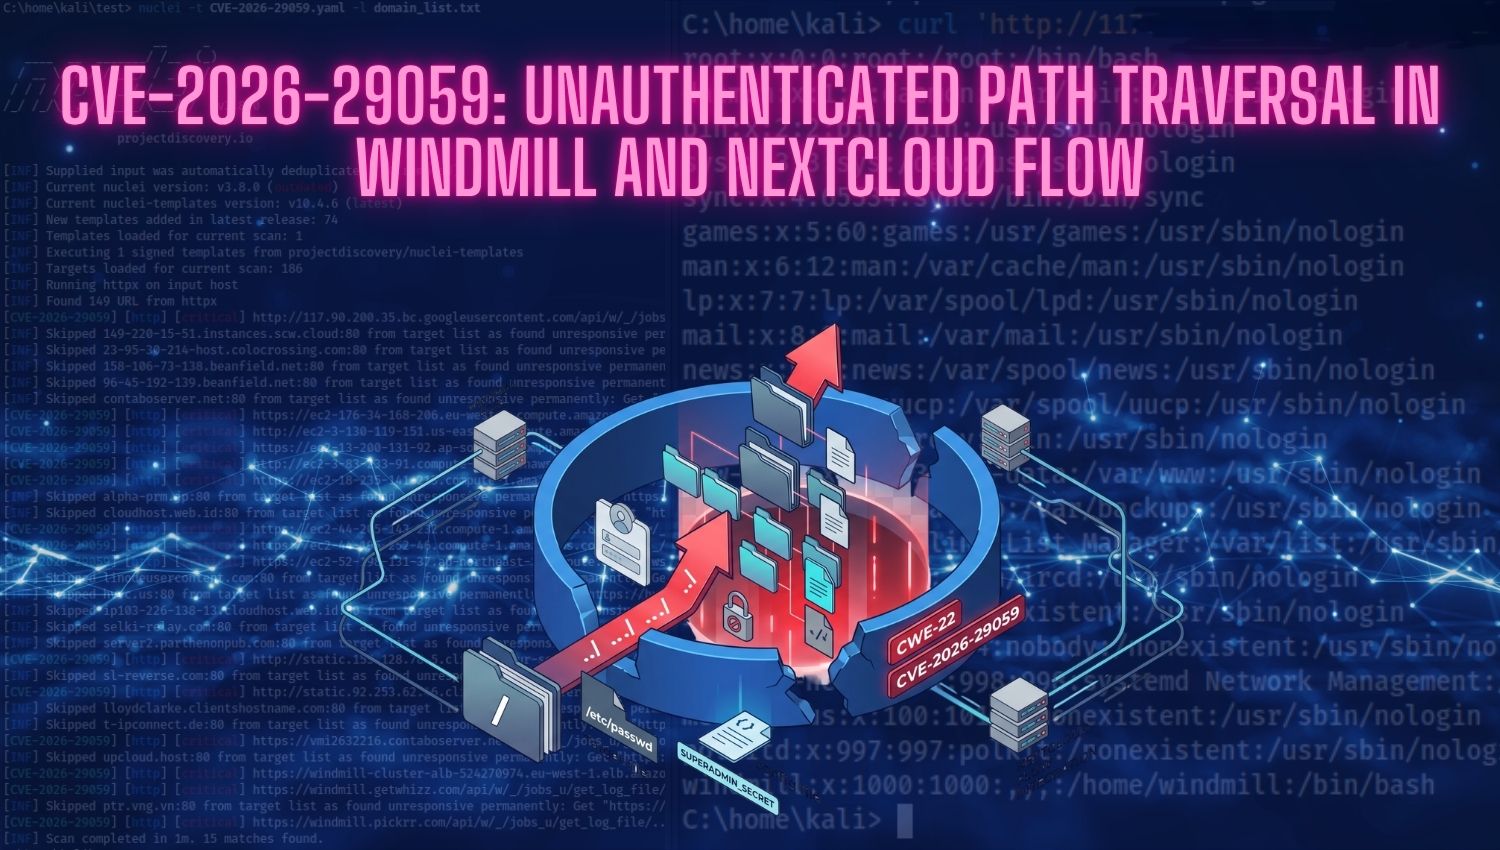
CVE-2026-29059: Unauthenticated Path Traversal in Windmill and Nextcloud Flow

CVE-2026-29059 UnauthentIcated Path Traversal In WIndmIll and Nextcloud Flow

Introduction Modern enterprise automation relies heavily on unified workflow engines to connect disparate infrastructure components, manage background tasks, and streamline internal processes. Platforms such as Windmill and its integrations—including Nextcloud Flow—provide robust execution environments for scripts and automated jobs. However, because these systems process sensitive data and hold elevated permissions across networks, any inherent flaw severely expands an organization’s attack surface. When central infrastructure automation

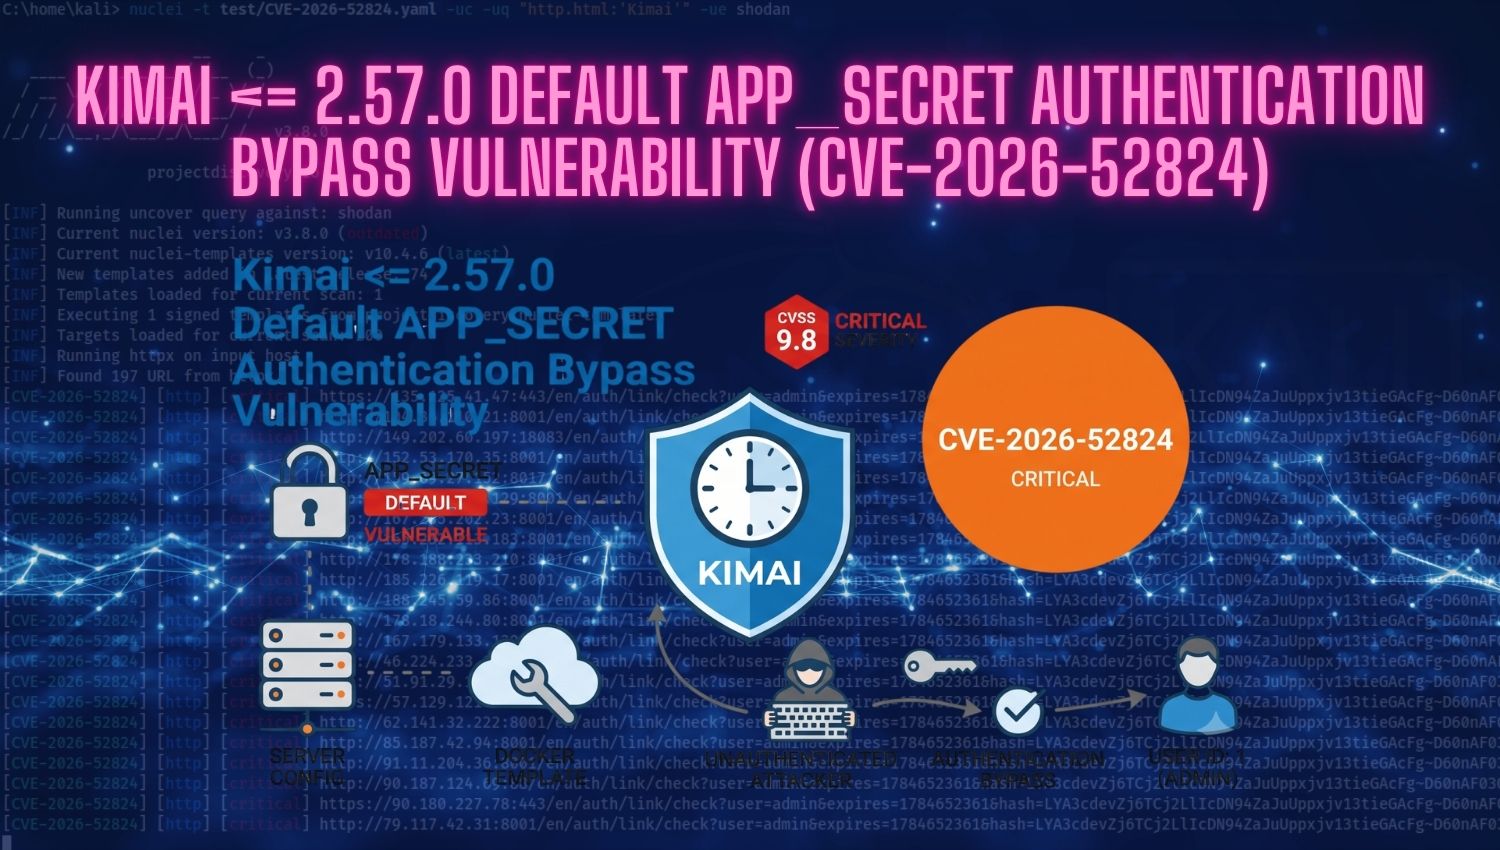
Kimai <= 2.57.0 Default APP_SECRET Authentication Bypass Vulnerability (CVE-2026-52824)

Kimai 2.57.0 Default APP_SECRET Authentication Bypass Vulnerability (CVE-2026-52824)

Introduction Kimai, an open-source time tracking and project management platform, is widely used by organizations and freelancers worldwide to manage sensitive operational, financial, and client data. However, a critical security flaw identified as CVE-2026-52824, affecting version 2.57.0 and earlier, highlights the severe consequences of insecure default configurations in production environments. When cryptographic secrets remain unchanged