
Exploitation of DbGate Remote Code Execution via Dynamic Import Bypass (CVE-2026-47670)
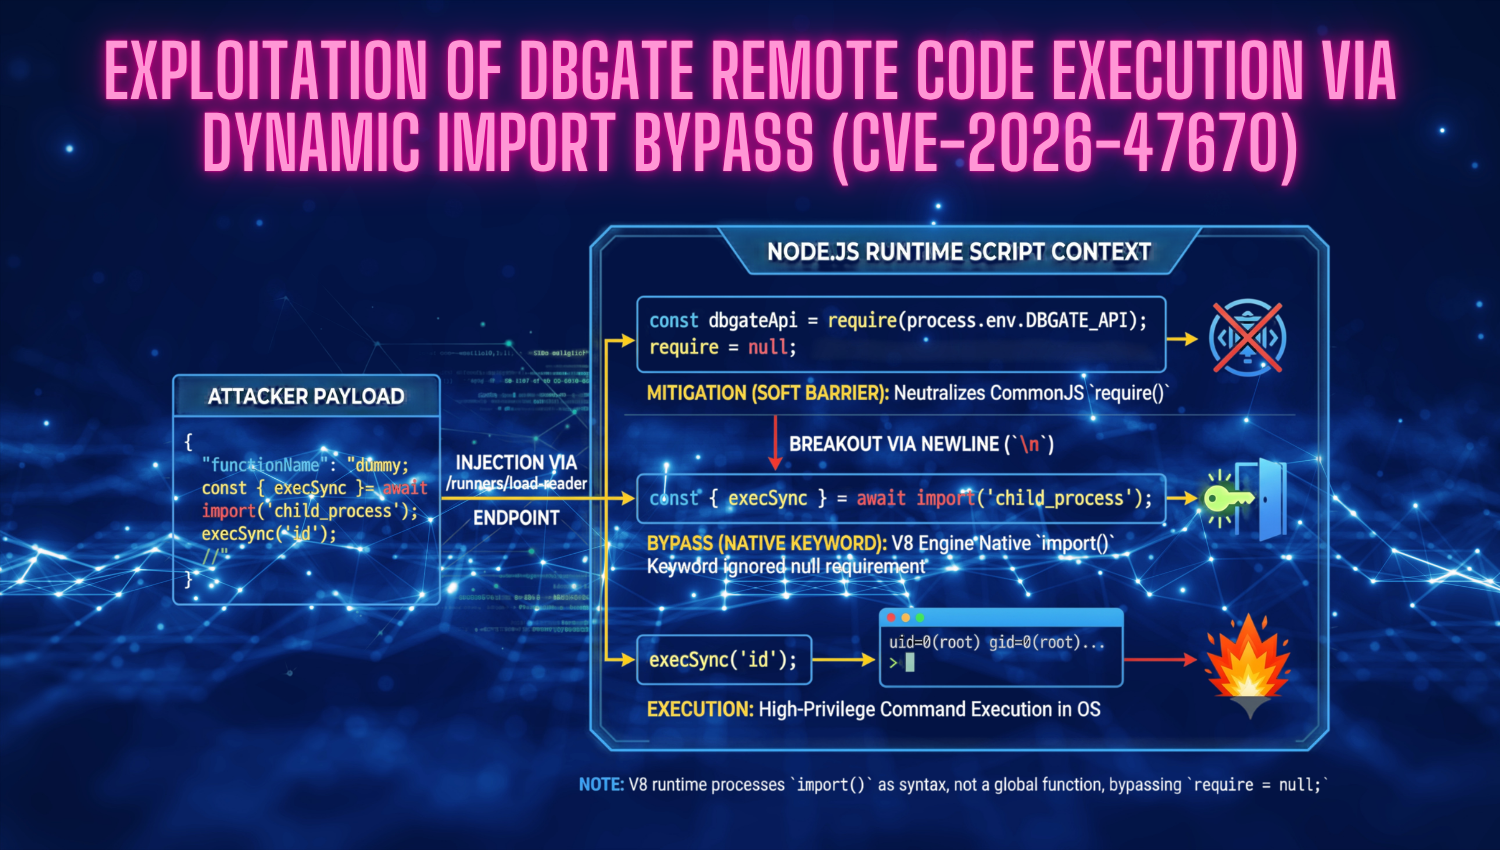
Introduction In modern web architectures, open-source cross-platform database administration tools like DbGate are widely adopted by DevOps teams and database administrators to streamline data visualization, schema editing, and multi-database query management. However, when these powerful administrative tools implement dynamic server-side script execution mechanisms without enforcing rigorous input sanitization, strict type validation, and robust context isolation, severe security vulnerabilities can easily emerge. This article explores CVE-2026-47670, a critical authenticated