Vulnerability Analysis: CVE-2026-76461 – Critical Cisco Secure Email Gateway Vulnerability Exploited
CVE-2026-76461 Critical Cisco Secure Email Gateway Vulnerability Exploited

Introduction Email remains one of the primary vectors for enterprise cyberattacks, making secure email gateways critical perimeter defenses. Recently, a severe security flaw identified as CVE-2026-76461 was discovered in Cisco Secure Email Gateway (formerly Cisco Email Security Appliance / ESA). Rated with a maximum-severity CVSS score of 9.8 (Critical), this vulnerability allows unauthenticated, remote attackers to execute arbitrary commands at the highest system privileges. Both Cisco and the
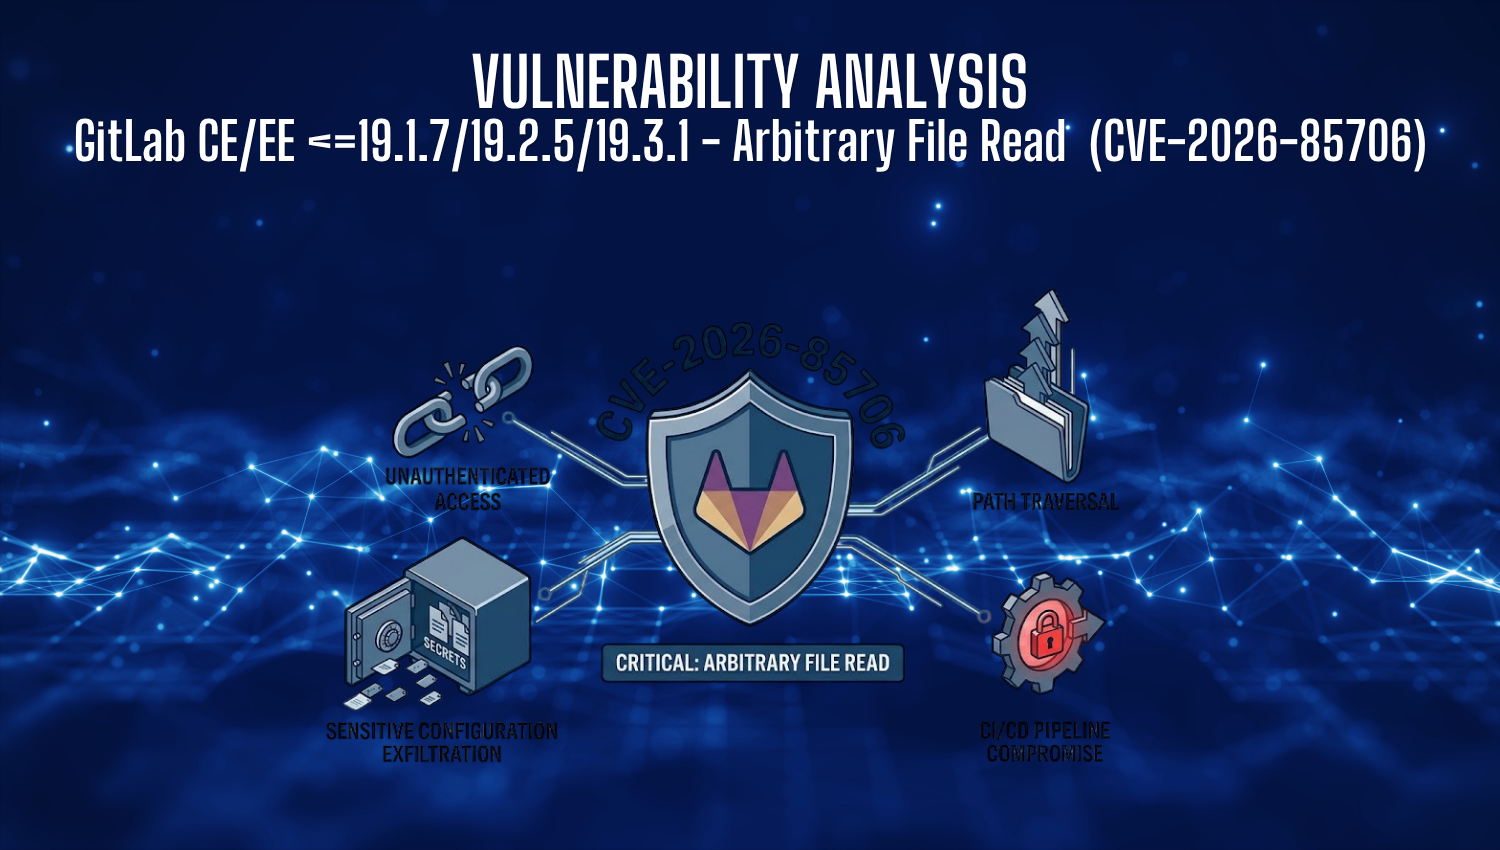
Vulnerability Analysis CVE-2026-85706 GitLab – Arbitrary File Read

CVE-2026-85706 GitLab

Introduction Security flaws in critical software development and deployment infrastructure pose a significant, far-reaching risk to modern organizational supply chains. GitLab, an open-source DevOps platform used worldwide for source code management and continuous integration/continuous deployment (CI/CD) pipelines, released emergency security updates addressing CVE-2026-85706. This maximum-severity vulnerability—rated at CVSS 10.0—allows unauthenticated remote attackers to read arbitrary files directly from the host file system

Critical Threats in Critical Infrastructures: June 2026 Cybersecurity Analysis

Critical Threats in Critical Infrastructures June 2026 Cybersecurity Analysis

Introduction Modern computing ecosystems are becoming increasingly complex due to the convergence of cloud-based architectures, intricate network protocols, and widespread web integrations. While this complexity yields an expansive attack surface for threat actors, it mandates proactive patch management for defensive teams. This rapid digital transformation has outpaced traditional perimeter security, leaving legacy frameworks highly susceptible to sophisticated, automated multi-stage attacks. June 2026 marked