Vulnerability Analysis: CVE-2026-123158 “SSHole” – Critical Root Vulnerability in Alpine Linux Systems
Introduction The cybersecurity landscape recently witnessed a highly critical vulnerability dubbed “SSHole” (CVE-2026-123158). This flaw represents a severe authentication bypass issue that primarily impacts lightweight, container-friendly operating systems like Alpine Linux. By exploiting an unintended collision between several independent security mechanisms, unauthenticated remote attackers can bypass SSH authentication entirely. In specific cloud environments, this seamlessly translates to immediate, unauthorized root access, making it one
Vulnerability Analysis: CVE-2026-116366 ClickHouse Server – Brotli v1.2.0 Decoder DoS/OOB-Write

CVE-2026-116366

Introduction ClickHouse is a widely deployed, high-performance columnar database management system designed for online analytical processing (OLAP). To maintain its exceptional read and write speeds, ClickHouse relies heavily on efficient data compression algorithms, including Google’s Brotli library. CVE-2026-116366 represents a critical security flaw in how ClickHouse handles incoming Brotli-compressed payloads. This vulnerability exposes affected servers to unauthenticated Remote Code Execution (RCE) and Denial of

Vulnerability Analysis: CVE-2026-111497 Critical out-of-bounds write in the Node.js Brotli decoder

CVE-2026-111497

Introduction In modern web architectures, data compression plays a pivotal role in reducing network bandwidth consumption, optimizing server response times, and accelerating overall web content delivery across distributed networks. Brotli—a popular lossless data compression algorithm originally developed by Google—has quickly established itself as a ubiquitous open-source standard widely integrated across major web browsers, edge reverse proxies, content delivery networks (CDNs), and backend server

Vulnerability Analysis: CVE-2026-116067 Paisa < 0.7.8 – Unauthenticated Path Traversal

CVE-2026-116067

Introduction In modern web applications, handling file paths securely is a critical requirement. When input fields accept file paths or file names directly without adequate validation, software can become susceptible to Directory Traversal (Path Traversal) flaws. CVE-2026-116067 represents a high-severity Path Traversal vulnerability discovered in Paisa—a popular open-source, self-hosted personal finance tracking application designed to help users manage their ledgers, budgets, and investments. Self-hosted financial

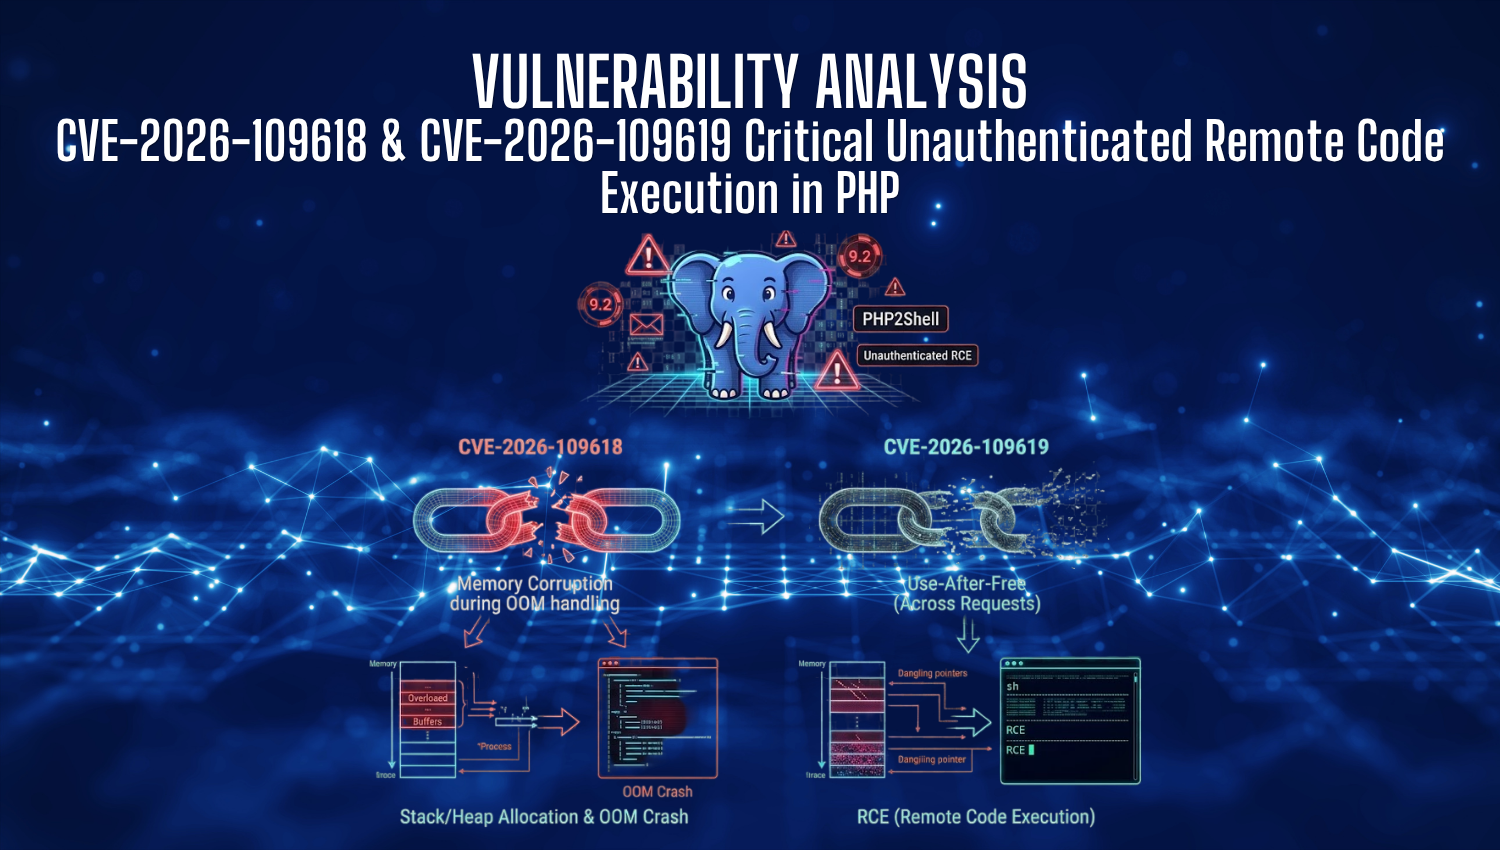
Vulnerability Analysis: CVE-2026-109618 & CVE-2026-109619 Critical Unauthenticated Remote Code Execution in PHP

Introduction CVE-2026-109618 and CVE-2026-109619 represent one of the most critical security emergencies in recent PHP history, threatening millions of active web servers globally. Highlighting the fundamental dangers of memory management flaws within persistent web server worker environments—such as PHP-FPM or Apache mod_php—these vulnerabilities enable unauthenticated remote attackers to execute arbitrary system commands with the privilege level of the

Learning Cybersecurity with ChatGPT: An AI-Powered Beginner’s Guide

learning cybersecurity with chatgpt

Introduction Cybersecurity is a challenging and complex field to learn due to constantly evolving threats and advancing technologies. In the past, stepping into this industry required reading hundreds of pages of technical documentation and attending expensive training sessions. Today, thanks to Artificial Intelligence (AI), access to information has fundamentally changed. ChatGPT can transform into a 24/7 accessible personal tutor that simplifies complex

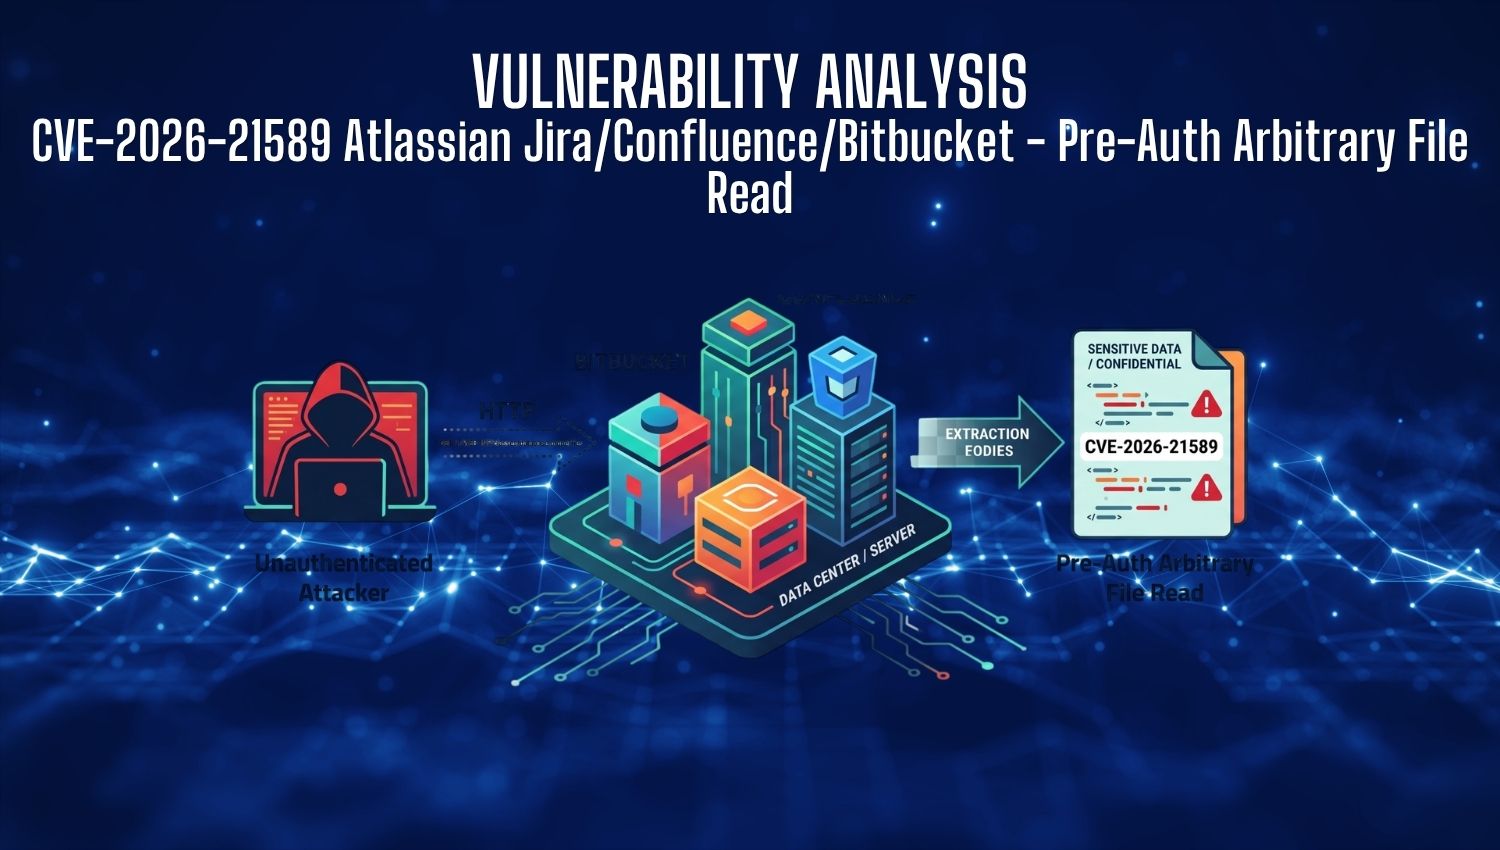
Vulnerability Analysis CVE-2026-21589 Atlassian Jira/Confluence/Bitbucket – Pre-Auth Arbitrary File Read

CVE-2026-21589

Introduction In October 2026, Atlassian issued an emergency security advisory disclosing CVE-2026-21589, a critical unauthenticated arbitrary file access vulnerability affecting its core self-hosted product suite. Assigned a CVSSv4 score of 9.3 (Critical), this security flaw allows unauthenticated remote threat actors to read arbitrary files directly from target system directories. Unauthenticated arbitrary file read vulnerabilities represent a severe risk to enterprise infrastructure because

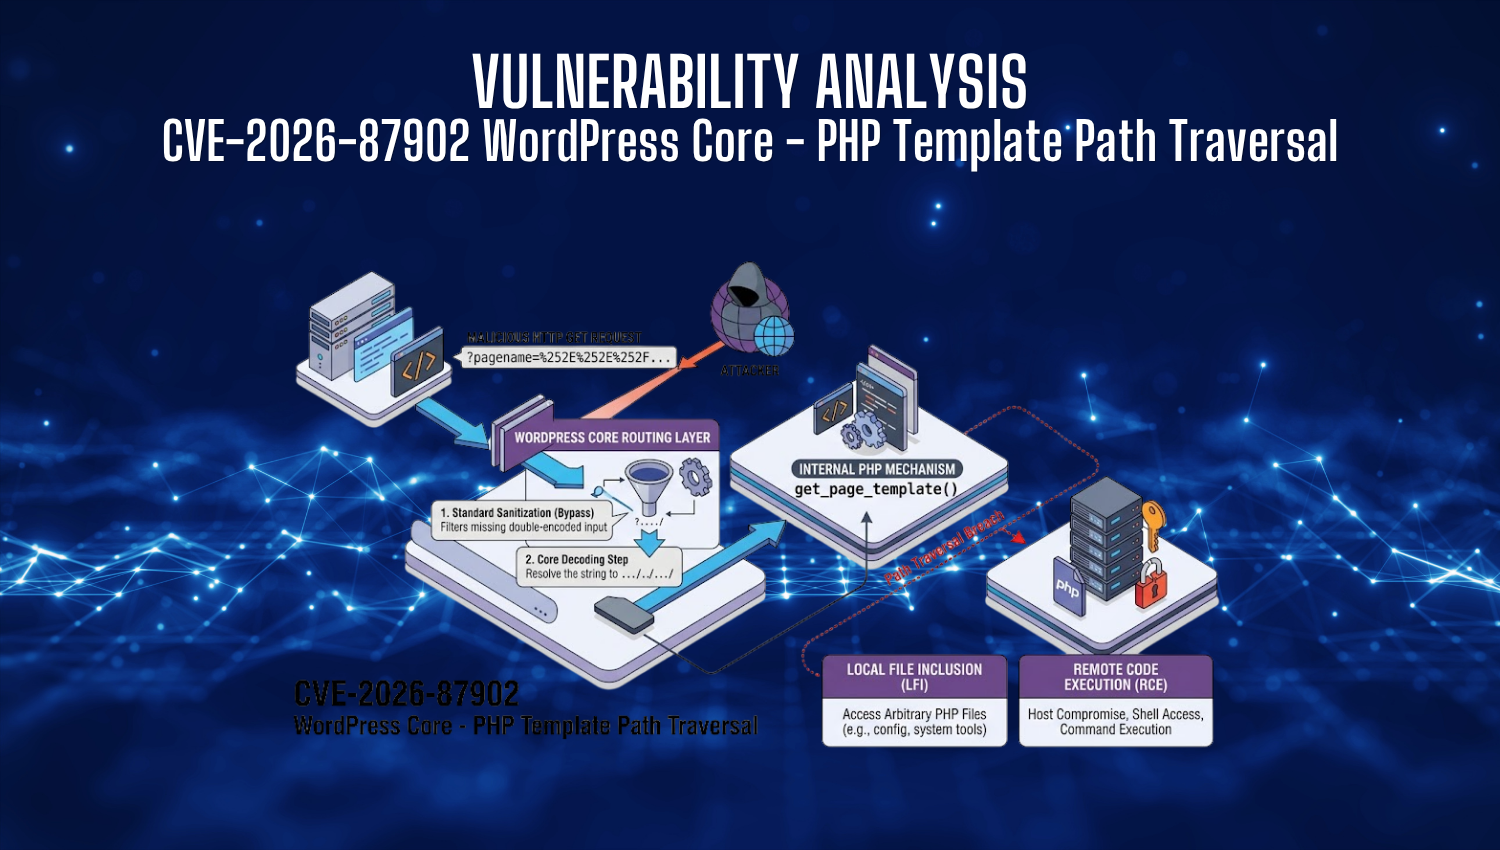
Vulnerability Analysis CVE-2026-87902 WordPress Core – PHP Template Path Traversal

CVE-2026-87902 WordPress Core - PHP Template Path Traversal

Introduction The global cybersecurity community witnessed a significant shift in threat metrics when a severe, unauthenticated security flaw within WordPress Core was disclosed. Designated as CVE-2026-87902, this critical flaw impacts tens of millions of active web applications dependent on the open-source Content Management System (CMS). Assigning it a CVSS v4.0 rating of 9.2 (Critical), security threat intelligence teams flagged the vulnerability for its

The Hidden Gateway to Enterprise Networks: Unbound DNS Flaw and the Threat to Global Resolvers

Unbound DNS Flaw and the Threat to Global Resolvers

Introduction The Domain Name System functions as the foundational directory of global internet infrastructure, silently resolving human-readable hostnames into network addresses. However, severe memory management flaws and improper packet parsing within DNSSEC (Domain Name System Security Extensions) validation modules can instantly transform these trusted recursive resolvers into high-impact entry points for adversary breach campaigns. Officially tracked as CVE-2026-81642 and publicly disclosed by NLnet

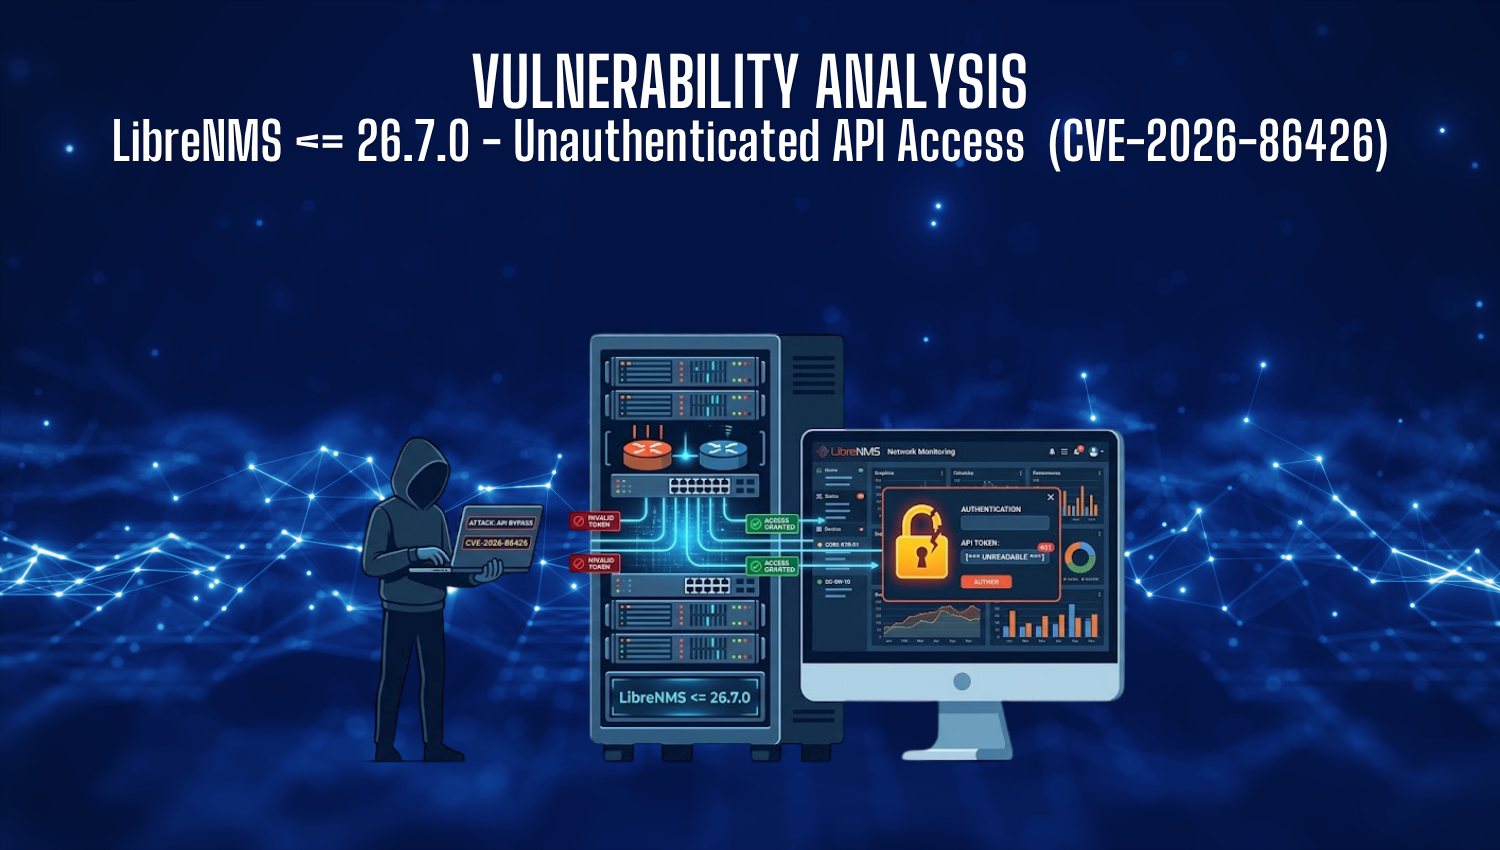
Vulnerability Analysis: CVE-2026-86426 LibreNMS <= 26.7.0 – Unauthenticated API Access

CVE-2026-86426 LibreNMS

Introduction CVE-2026-86426 represents a critical authentication bypass vulnerability affecting LibreNMS network monitoring installations running version 26.7.0 or earlier. Publicly disclosed and addressed in late 2026, the vulnerability received a severe CVSS v4.0 rating of 9.2 (Critical) due to its low attack complexity and high impact. The underlying flaw resides within the API authentication middleware, which fails to strictly enforce parameter types during input