Vulnerability Analysis CVE-2026-87902 WordPress Core – PHP Template Path Traversal
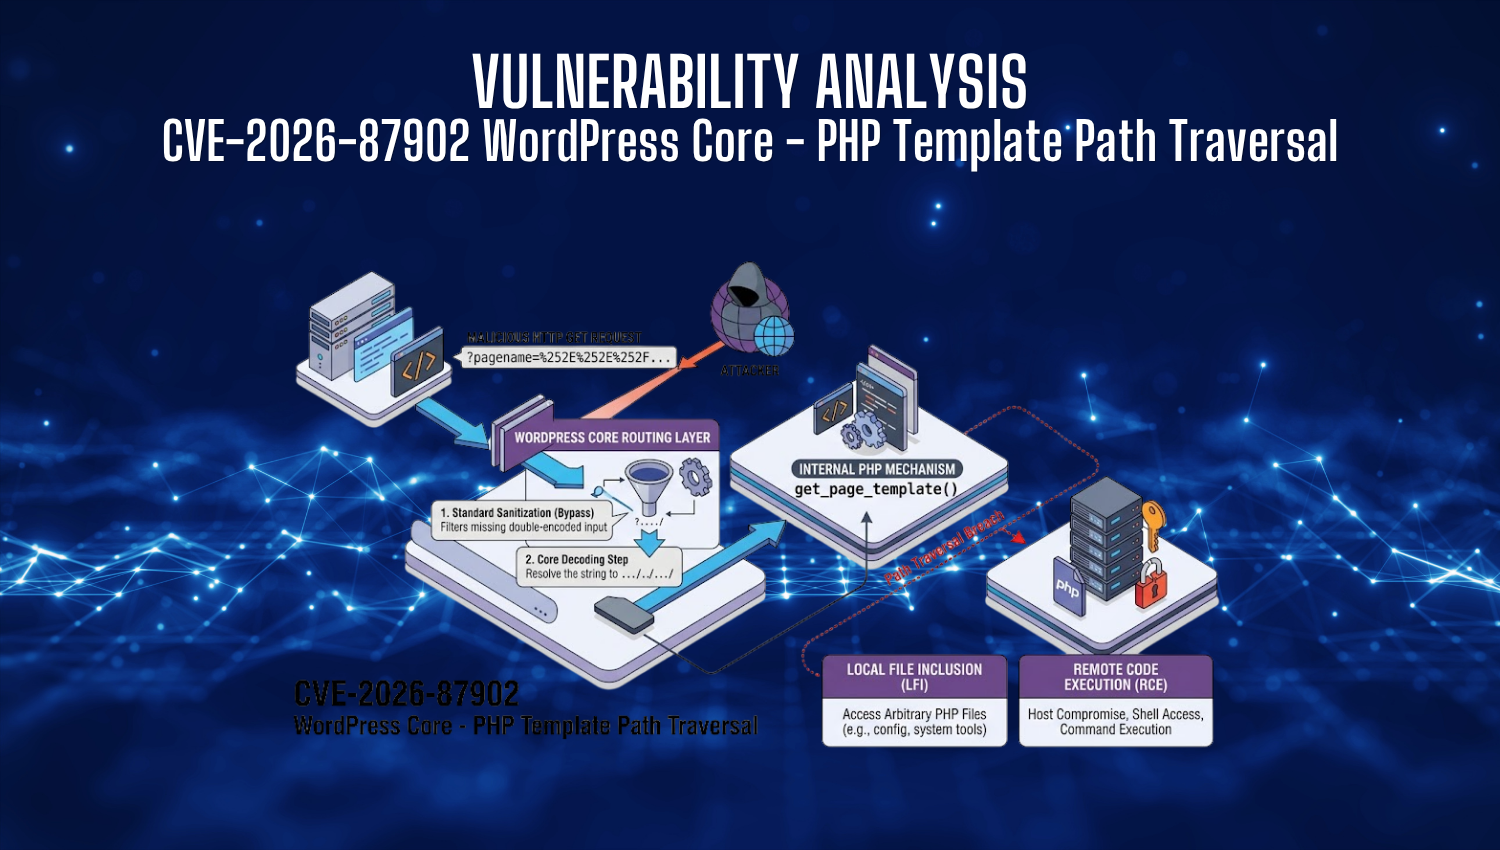
CVE-2026-87902 WordPress Core - PHP Template Path Traversal

Introduction The global cybersecurity community witnessed a significant shift in threat metrics when a severe, unauthenticated security flaw within WordPress Core was disclosed. Designated as CVE-2026-87902, this critical flaw impacts tens of millions of active web applications dependent on the open-source Content Management System (CMS). Assigning it a CVSS v4.0 rating of 9.2 (Critical), security threat intelligence teams flagged the vulnerability for its
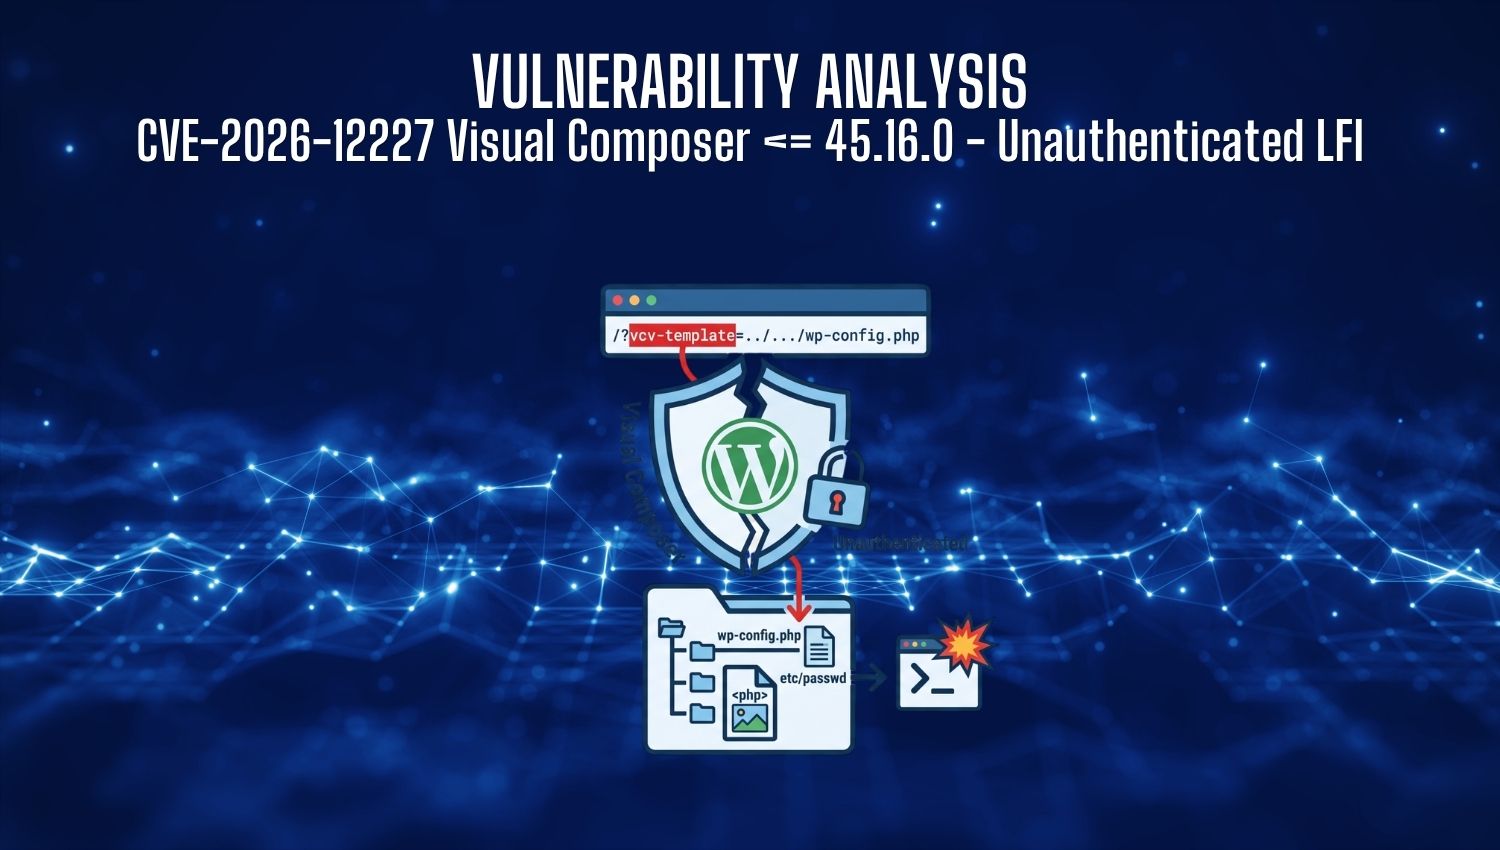
Vulnerability Analysis: CVE-2026-12227 Visual Composer <= 45.16.0 – Unauthenticated LFI

CVE-2026-12227

Introduction In the landscape of web application security, WordPress plugins are frequently targeted due to their widespread deployment. The Visual Composer Website Builder, a highly popular page builder plugin for WordPress, was found to contain a critical security flaw designated as CVE-2026-12227. This vulnerability, affecting versions up to and including 45.16.0, allows unauthenticated attackers to exploit a Local File Inclusion (LFI) vulnerability. Due to its