Vulnerability Analysis CVE-2026-85706 GitLab – Arbitrary File Read
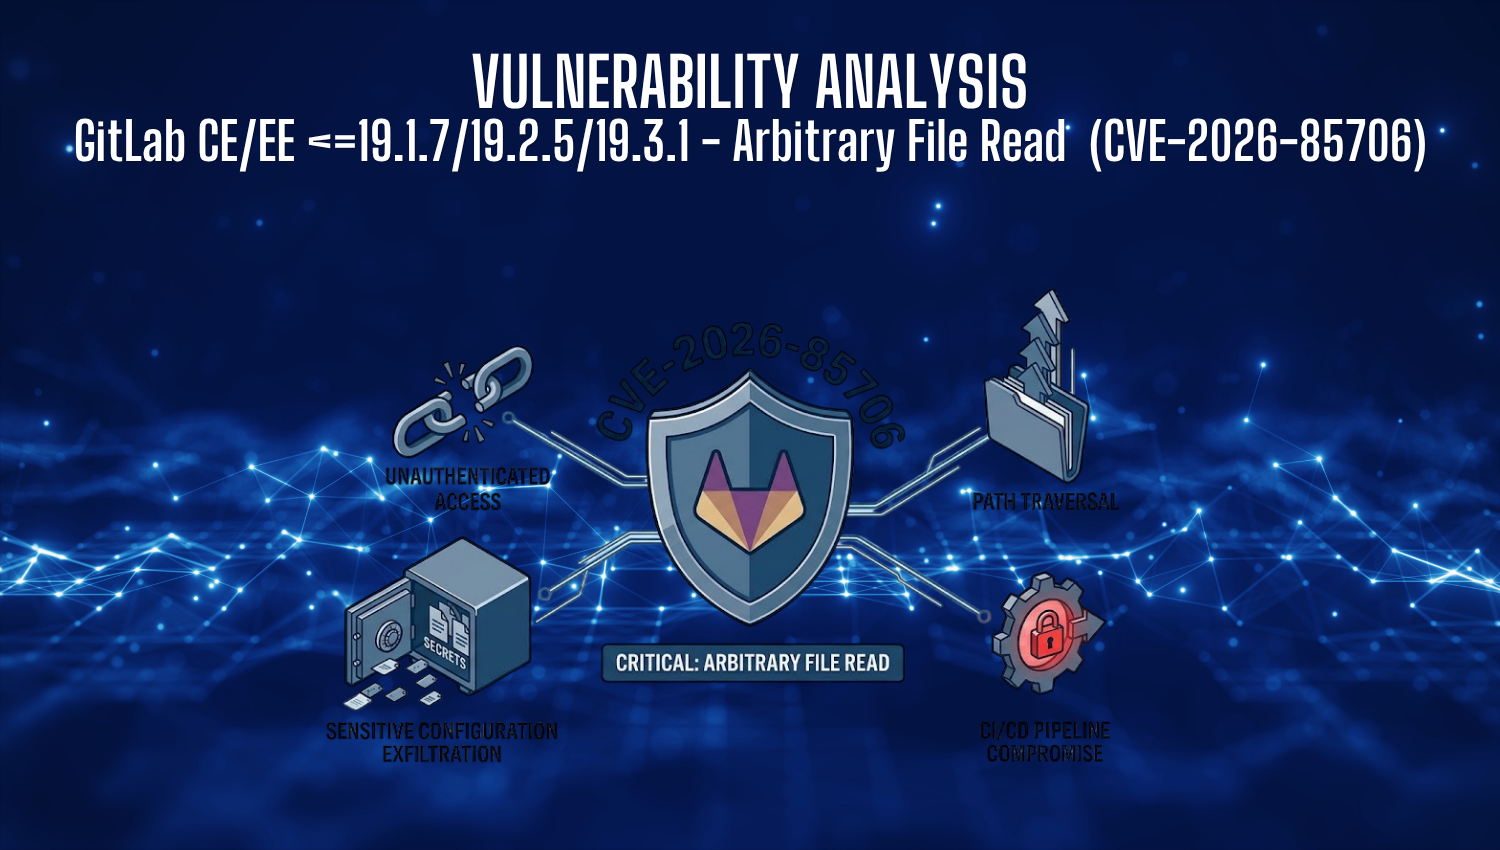
Introduction Security flaws in critical software development and deployment infrastructure pose a significant, far-reaching risk to modern organizational supply chains. GitLab, an open-source DevOps platform used worldwide for source code management and continuous integration/continuous deployment (CI/CD) pipelines, released emergency security updates addressing CVE-2026-85706. This maximum-severity vulnerability—rated at CVSS 10.0—allows unauthenticated remote attackers to read arbitrary files directly from the host file system