What You Need to Know About Ransomware Protection in 2026
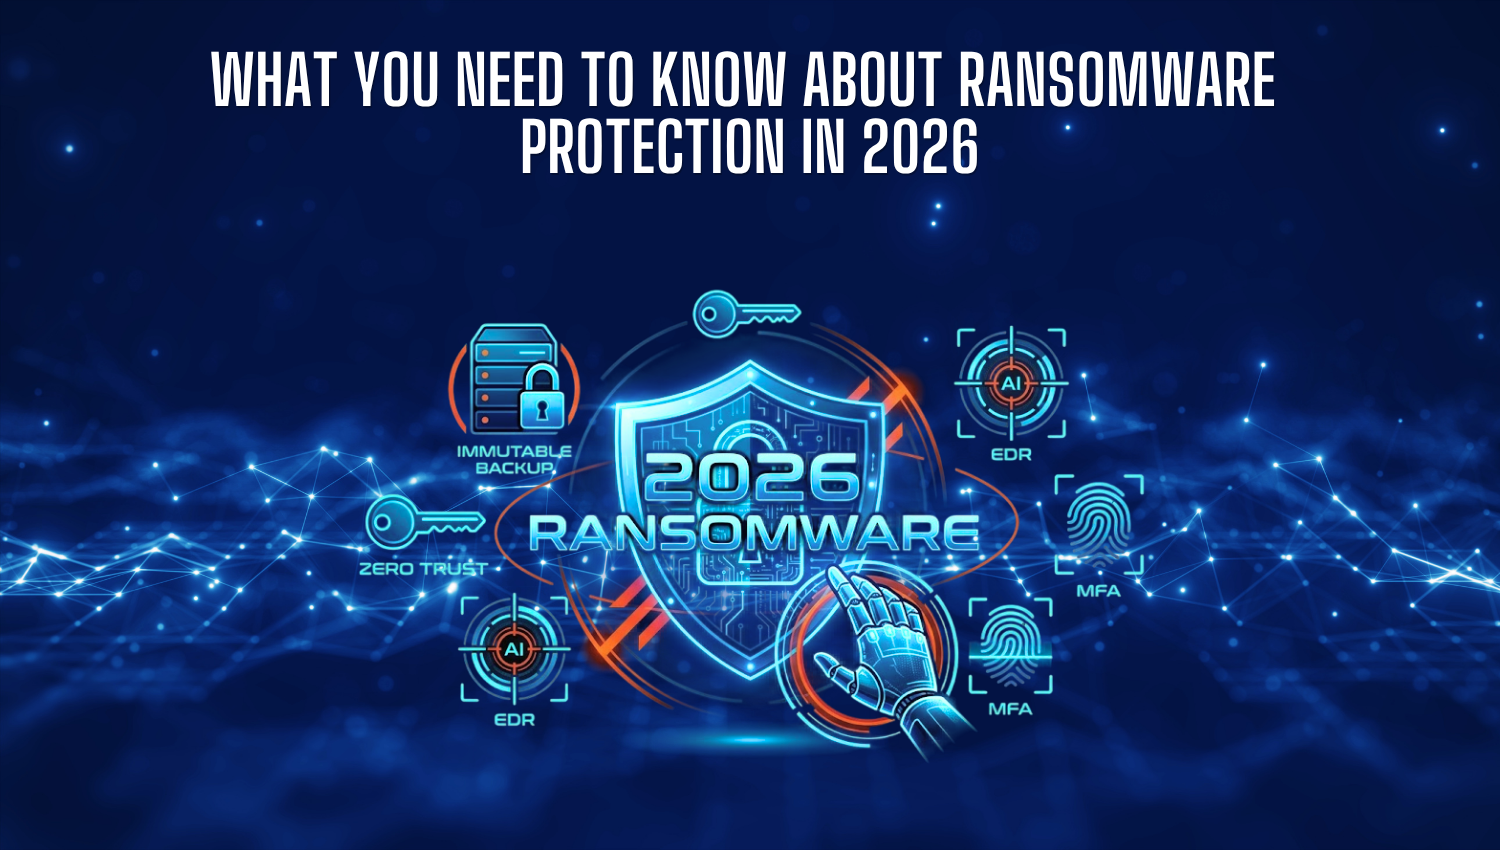
What You Need to Know About Ransomware

Introduction As we navigate through 2026, the cybersecurity landscape has become more complex than ever. Ransomware has evolved from simple encryption scripts into highly sophisticated, AI-driven operations that target organizations of all sizes. Cybercriminals now leverage advanced automation, deepfakes, and triple-extortion tactics to maximize their impact. Staying ahead of these threats requires more than just basic antivirus software; it demands a comprehensive, proactive approach
Learning Cybersecurity with ChatGPT: An AI-Powered Beginner’s Guide

learning cybersecurity with chatgpt

Introduction Cybersecurity is a challenging and complex field to learn due to constantly evolving threats and advancing technologies. In the past, stepping into this industry required reading hundreds of pages of technical documentation and attending expensive training sessions. Today, thanks to Artificial Intelligence (AI), access to information has fundamentally changed. ChatGPT can transform into a 24/7 accessible personal tutor that simplifies complex

The Ultimate 2026 Shodan Cheat Sheet Guide

The Ultimate 2026 Shodan Cheat Sheet Guide

Introduction In the current cybersecurity landscape, understanding an organization’s exposed digital footprint is a core priority. Shodan—often dubbed the world’s first search engine for Internet-connected devices—operates by systematically scanning IP addresses across the globe, grabbing service banners, and indexing raw protocol outputs. Unlike standard web search engines that crawl HTML page content, Shodan indexes everything from SSH servers, web portals, and databases to

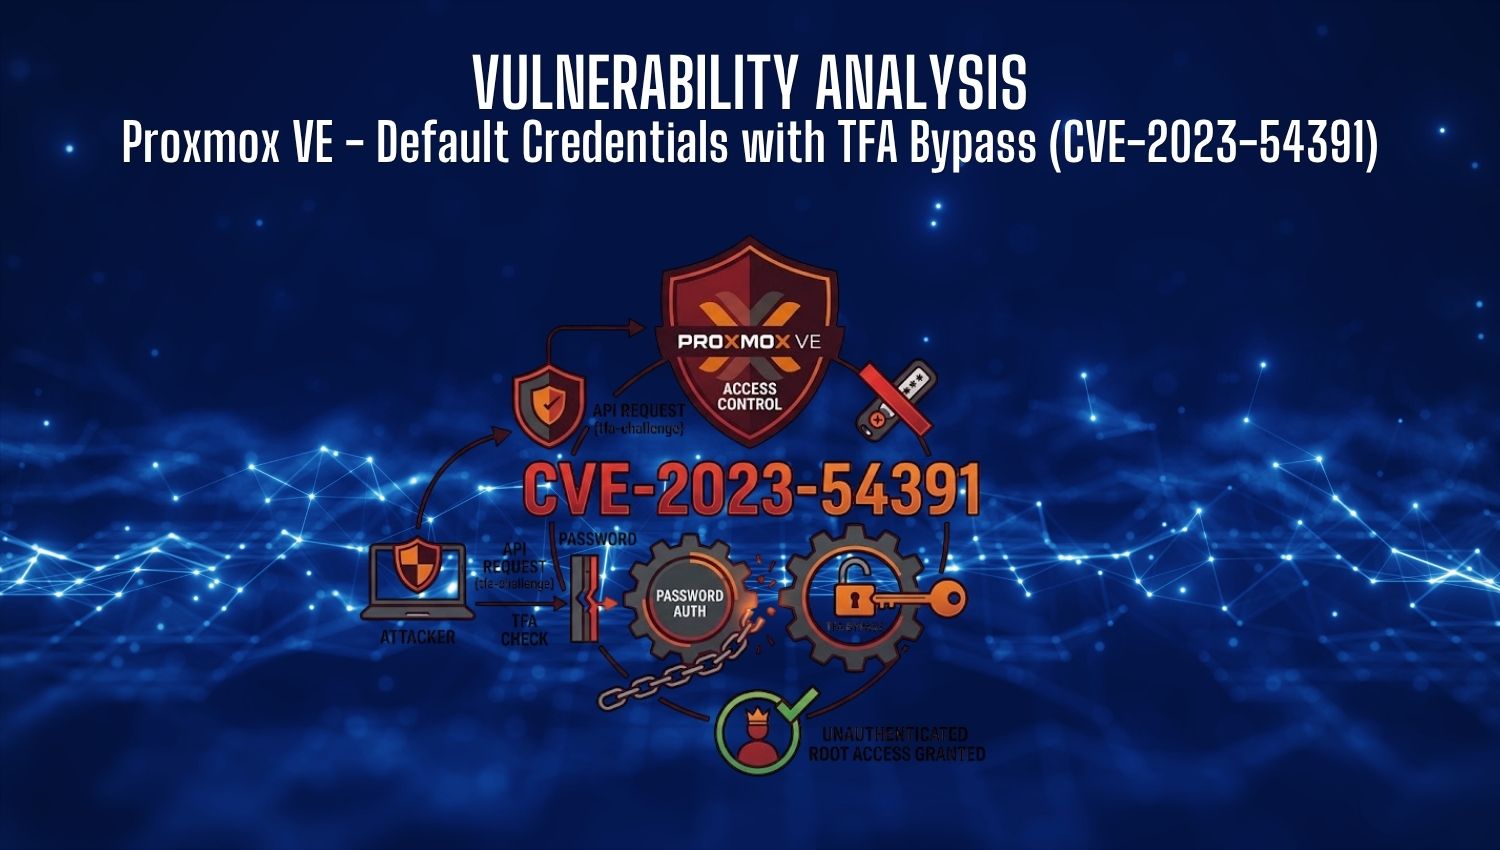
Vulnerability Analysis: Proxmox VE – Default Credentials with TFA Bypass (CVE-2023-54391)

Proxmox VE - Default Credentials with TFA Bypass (CVE-2023-54391)

Introduction CVE-2023-54391 represents a critical pre-authentication authentication bypass vulnerability in Proxmox Virtual Environment (PVE). Operating at a CVSS 3.1 score of 9.8 (Critical), this security flaw allows unauthenticated remote attackers to completely bypass standard password authentication mechanisms. By manipulating parameters in the login API endpoint, an attacker can gain full superuser (root@pam) access to the underlying hypervisor management plane without knowing the victim

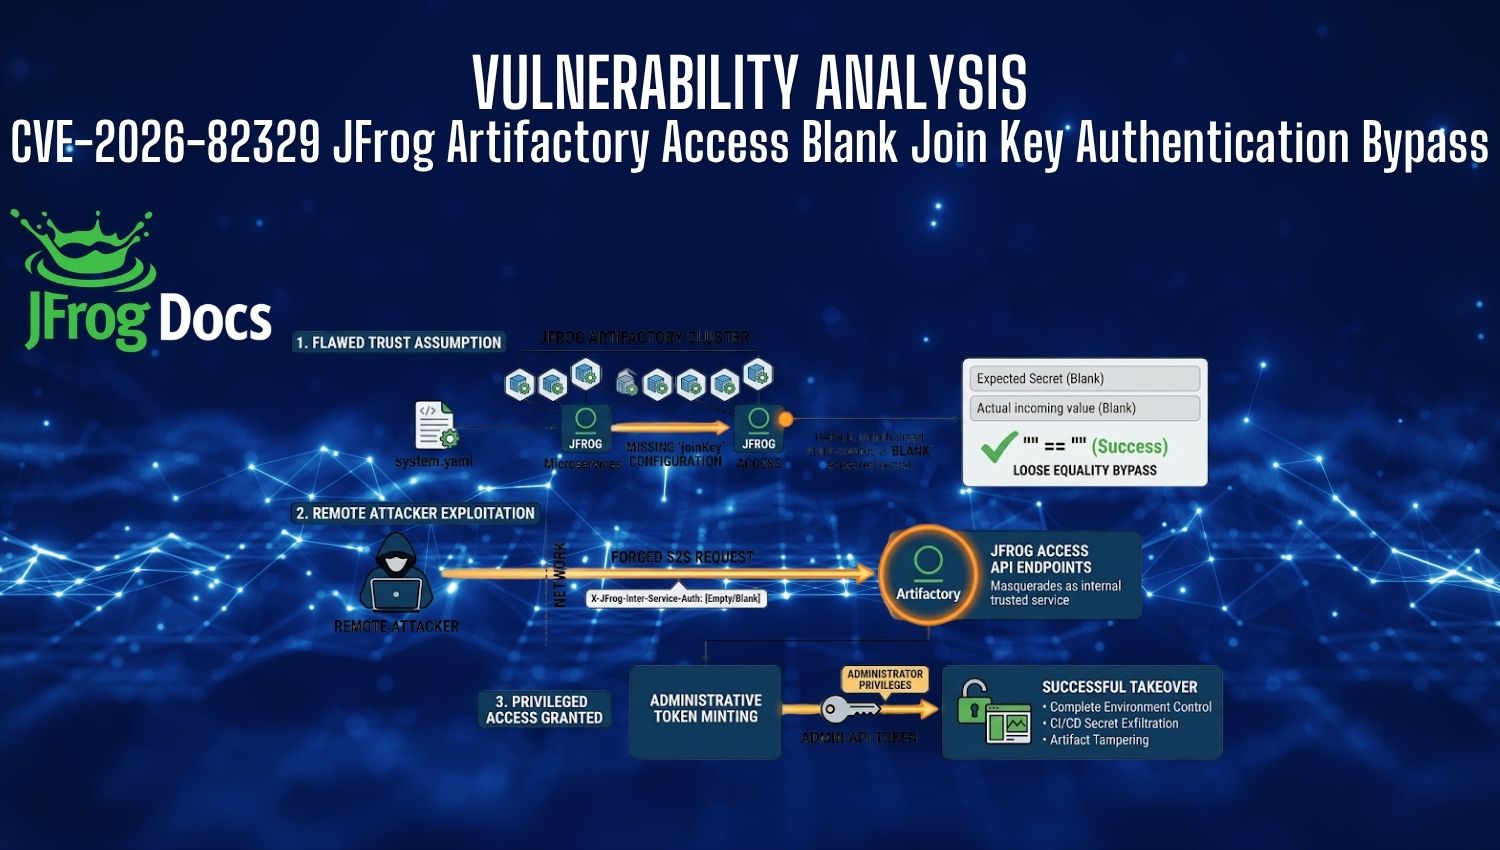
Vulnerability Analysis: CVE-2026-82329 JFrog Artifactory Access Authentication Bypass

CVE-2026-82329 JFrog Artifactory Access Blank Join Key Authentication Bypass

Introduction JFrog Artifactory serves as a central pillar in modern software engineering, providing universal artifact management across continuous integration and continuous delivery (CI/CD) pipelines. Given its privileged position—storing sensitive binaries, container images, AI models, and proprietary source code dependencies—a breach within Artifactory poses significant supply chain risks to global digital infrastructure. Disclosed in late August 2026, CVE-2026-82329 represents a critical security flaw rated 9.8 (Critical) under CVSS

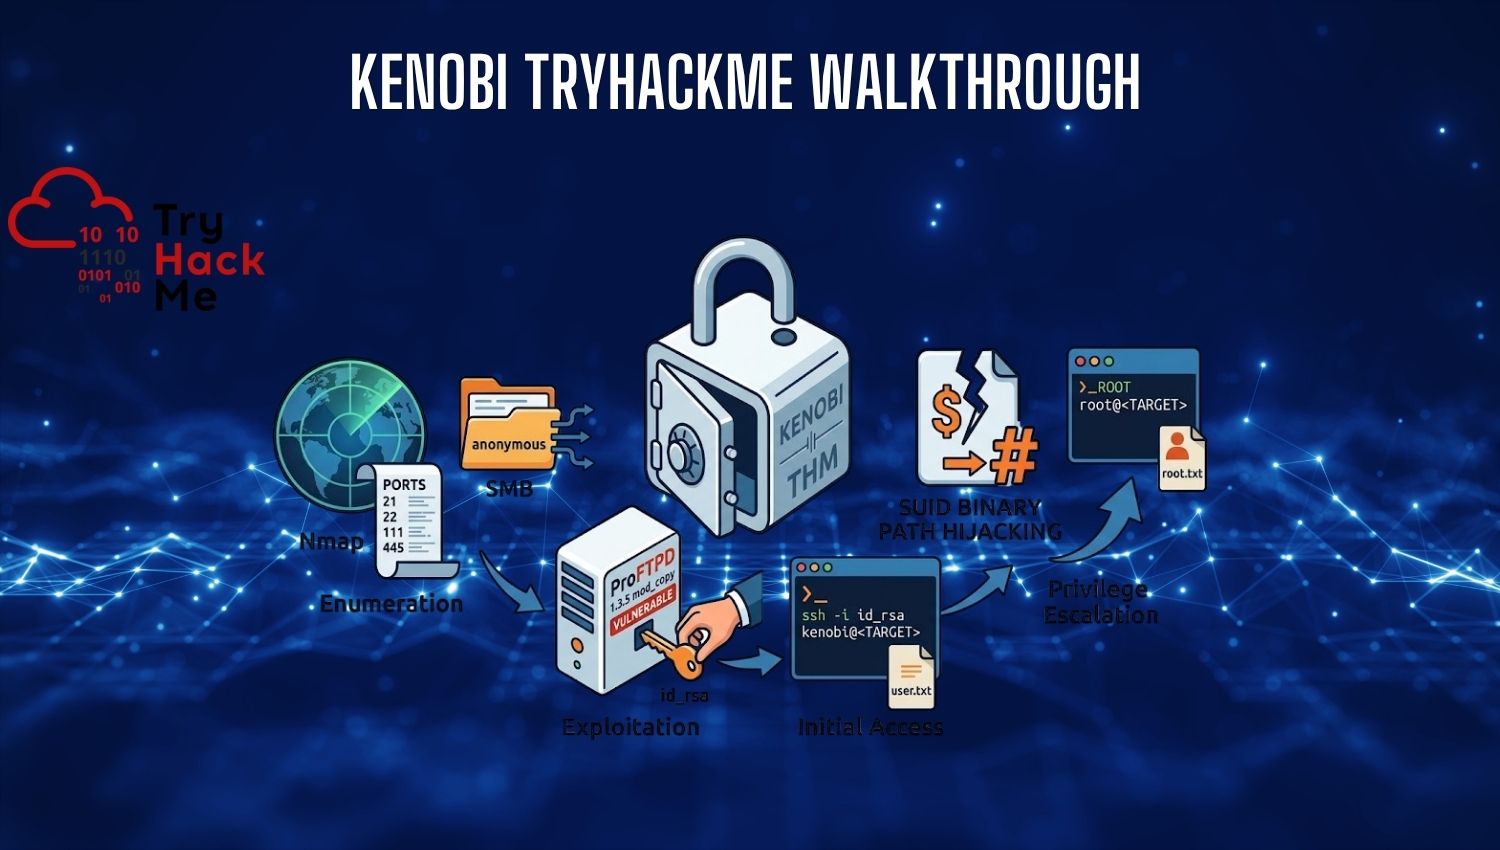
Kenobi TryHackMe Walkthrough

Introduction The Kenobi room on TryHackMe is one of the most fundamental and popular practical labs designed to teach offensive security concepts. Featuring a Linux target machine, this room introduces security researchers and aspiring penetration testers to fundamental network enumeration techniques, service exploitation, and post-exploitation privilege escalation. By walking through a realistic penetration testing scenario, learners gain hands-on experience in identifying misconfigurations and

The Ultimate Guide to 360 TryHackMe Free Rooms: Master Cybersecurity for Free

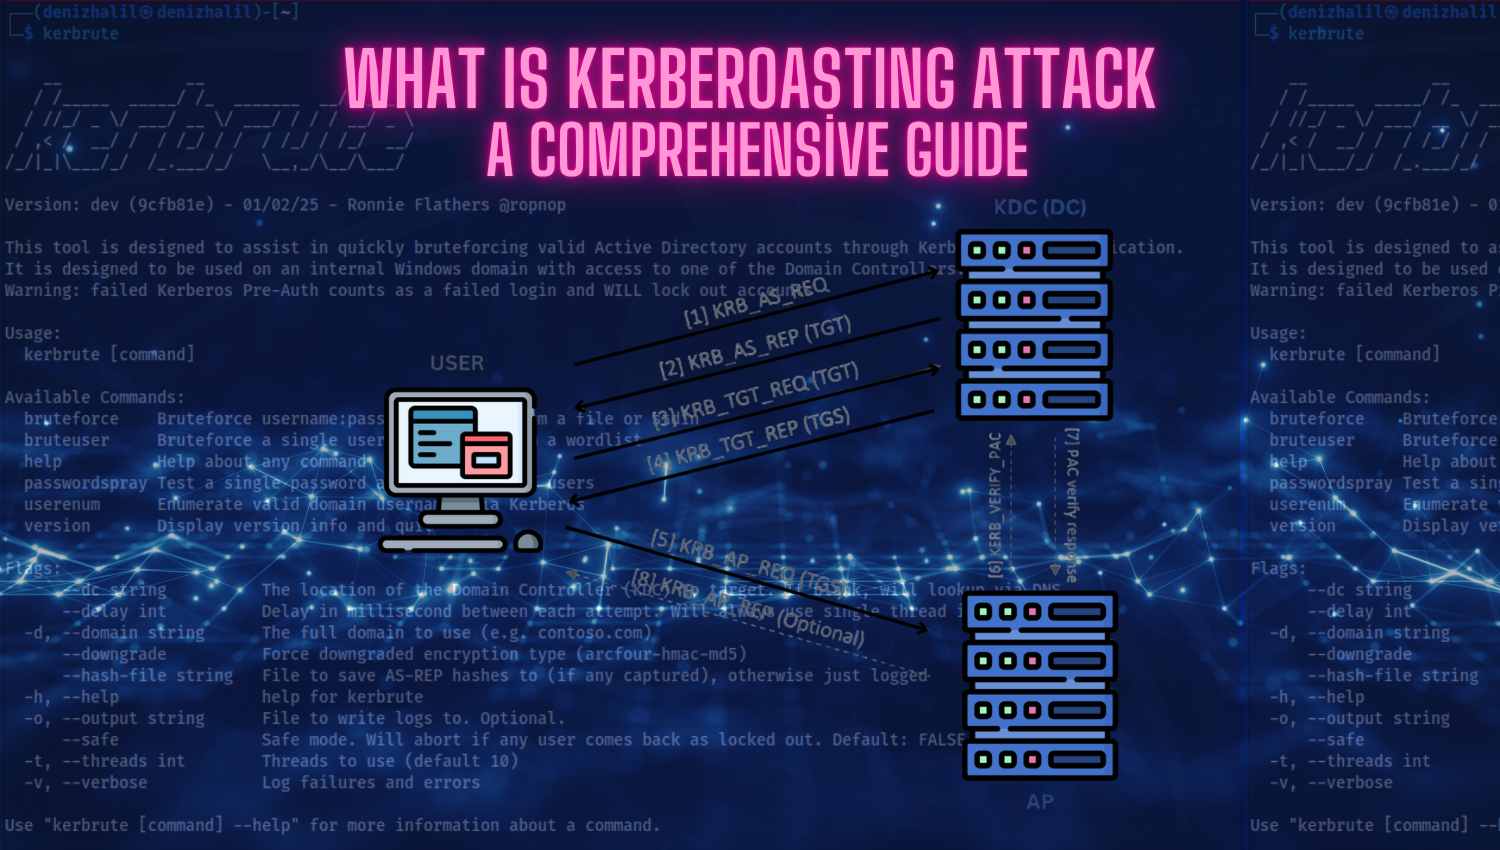
Remote Active Directory Pentesting A Comprehensive Overview

Introduction Starting a career in cybersecurity can feel like standing at the foot of an impossibly tall mountain. With endless sub-fields—ranging from web application security and digital forensics to reverse engineering, malware analysis, and cloud security—it is remarkably easy for beginners to feel overwhelmed about where to start, which path to follow, and what skills to prioritize. Fortunately, hands-on platforms like TryHackMe (THM) have

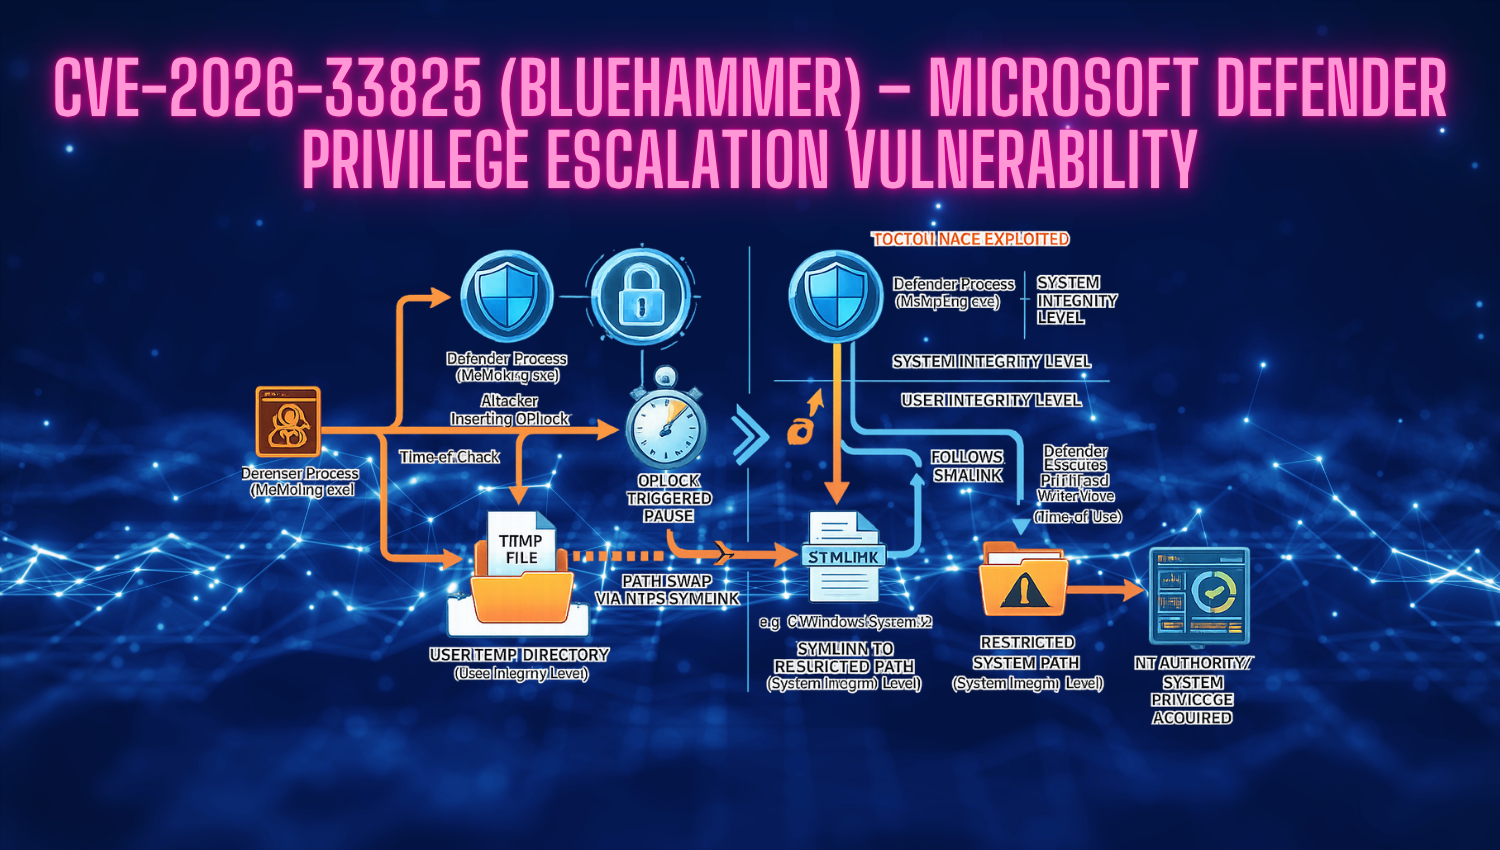
CVE-2026-33825 (BlueHammer) – Microsoft Defender Privilege Escalation Vulnerability

CVE-2026-33825 (BlueHammer) – MIcrosoft Defender PrIvIlege EscalatIon VulnerabIlIty

Introduction To achieve the highest level of privileges within an operating system, cyber threat actors frequently target the OS kernel or security software running with full system administrative rights. Discovered under the moniker “BlueHammer,” CVE-2026-33825 is a high-severity vulnerability that directly targets Windows’ native security mechanism, Microsoft Defender. Added by CISA to its Known Exploited Vulnerabilities (KEV) catalog due to evidence of active real-world exploitation, this

Cybersecurity Interview Questions and Answer Tips

CybersecurIty IntervIew QuestIons and Answer TIps

Introduction Cybersecurity stands out as one of the world’s fastest-growing and most crucial career fields in today’s technology-driven environment. With the rapid integration of digital systems across every industry, the need for skilled security professionals has grown beyond specialist IT departments to become a foundational element in business strategies and national infrastructures. According to the World Economic Forum’s