Vulnerability Analysis: CVE-2026-76461 – Critical Cisco Secure Email Gateway Vulnerability Exploited
CVE-2026-76461 Critical Cisco Secure Email Gateway Vulnerability Exploited

Introduction Email remains one of the primary vectors for enterprise cyberattacks, making secure email gateways critical perimeter defenses. Recently, a severe security flaw identified as CVE-2026-76461 was discovered in Cisco Secure Email Gateway (formerly Cisco Email Security Appliance / ESA). Rated with a maximum-severity CVSS score of 9.8 (Critical), this vulnerability allows unauthenticated, remote attackers to execute arbitrary commands at the highest system privileges. Both Cisco and the
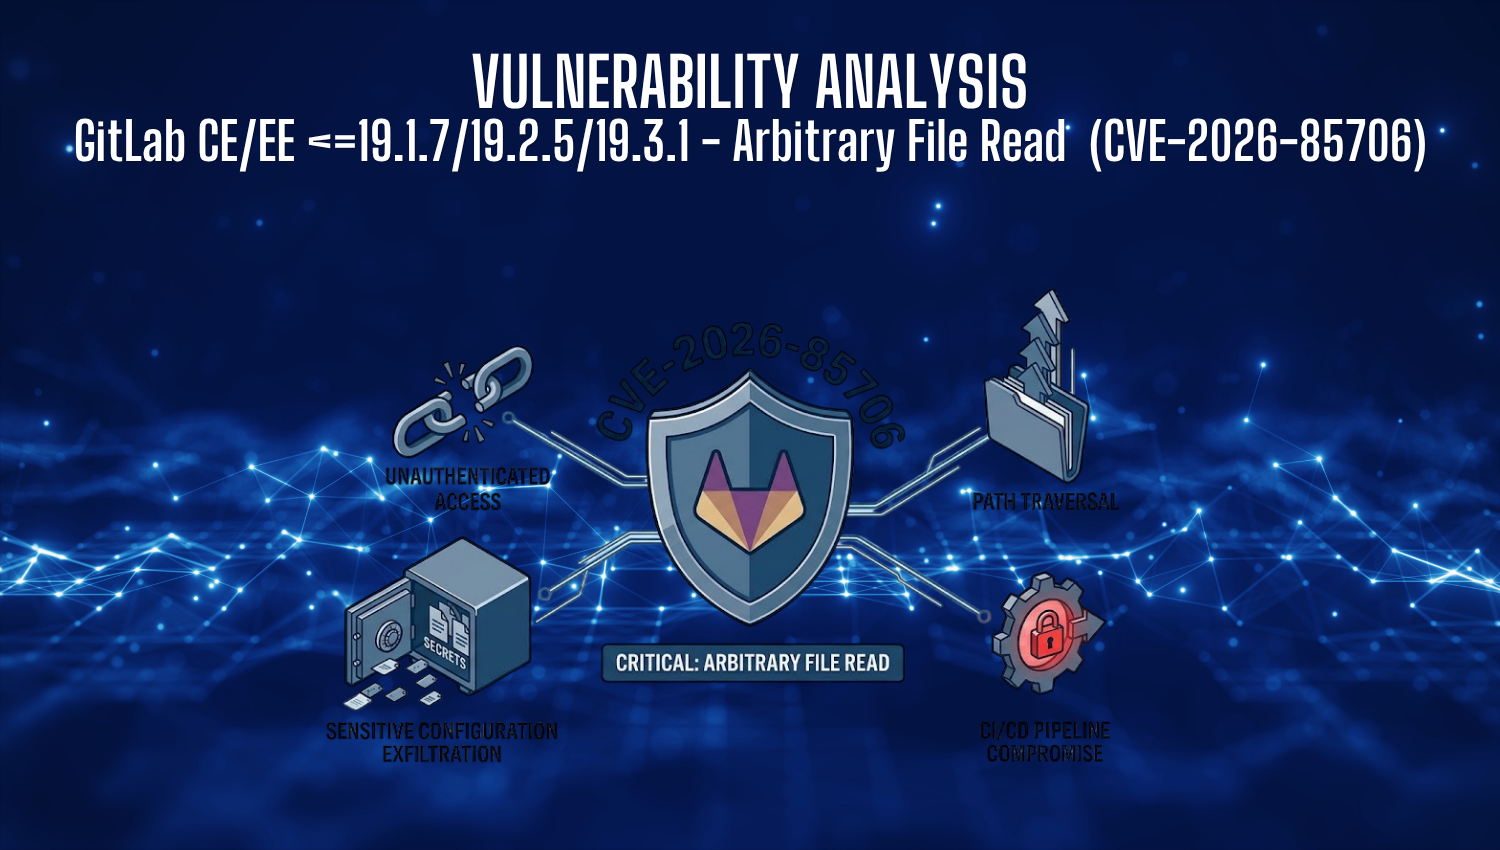
Vulnerability Analysis CVE-2026-85706 GitLab – Arbitrary File Read

CVE-2026-85706 GitLab

Introduction Security flaws in critical software development and deployment infrastructure pose a significant, far-reaching risk to modern organizational supply chains. GitLab, an open-source DevOps platform used worldwide for source code management and continuous integration/continuous deployment (CI/CD) pipelines, released emergency security updates addressing CVE-2026-85706. This maximum-severity vulnerability—rated at CVSS 10.0—allows unauthenticated remote attackers to read arbitrary files directly from the host file system

Critical Check Point VPN Zero-Day Exploited in the Wild (CVE-2026-50751)

CrItIcal Check PoInt VPN Zero-Day ExploIted In the WIld (CVE-2026-50751)

Introduction Perimeter security appliances serve as an organization’s absolute first line of defense, acting as the critical gatekeepers between the untrusted public internet and highly sensitive internal corporate assets. Because of this strategic positioning, edge devices like firewalls and virtual private networks have evolved into a primary, highly lucrative, and relentlessly pursued target for sophisticated state-sponsored groups and ransomware syndicates