Vulnerability Analysis: CVE-2026-12227 Visual Composer <= 45.16.0 – Unauthenticated LFI
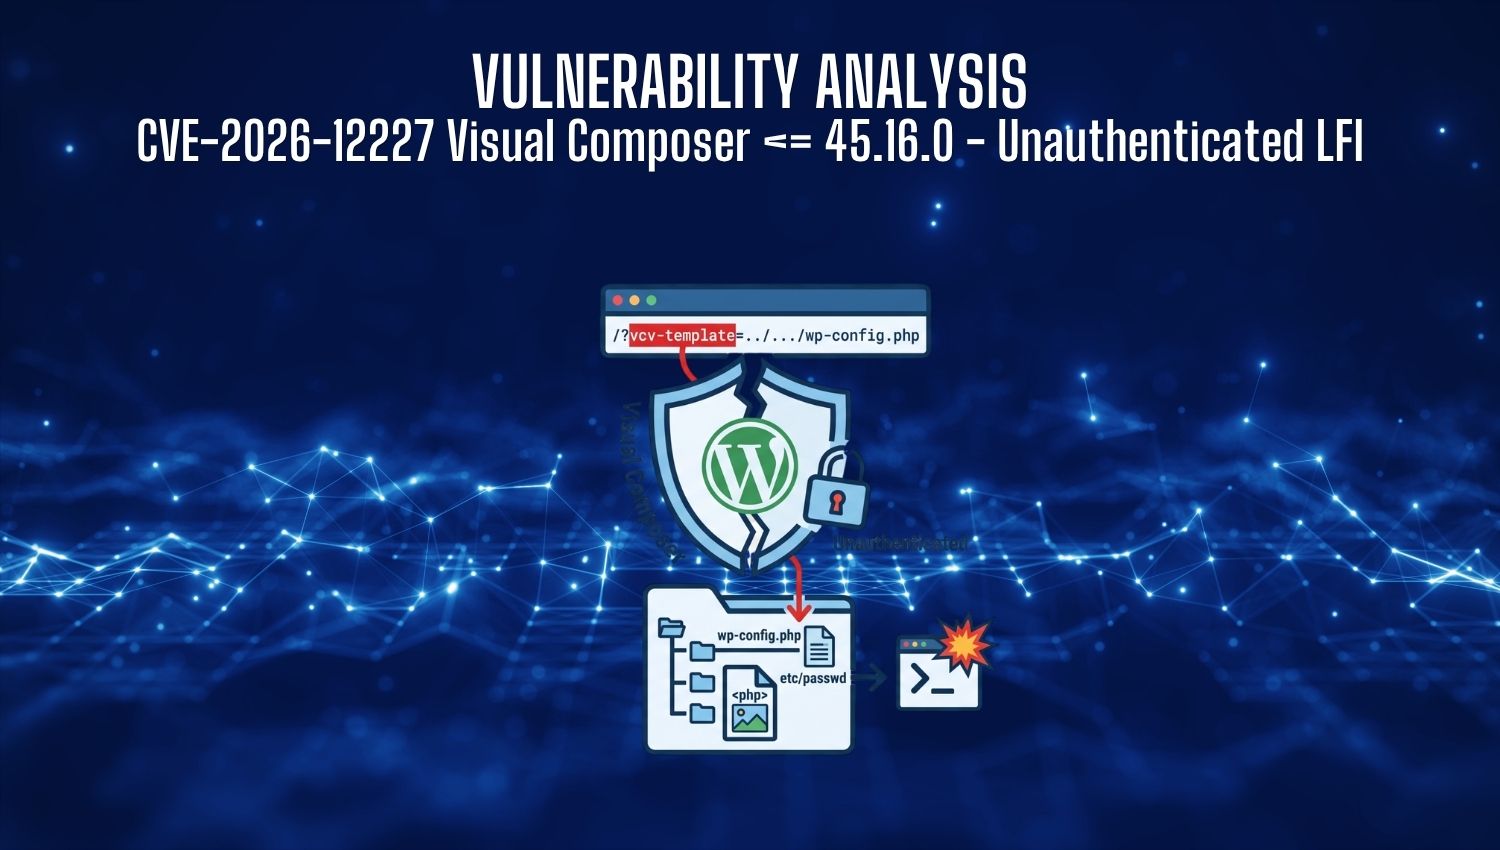
CVE-2026-12227

Introduction In the landscape of web application security, WordPress plugins are frequently targeted due to their widespread deployment. The Visual Composer Website Builder, a highly popular page builder plugin for WordPress, was found to contain a critical security flaw designated as CVE-2026-12227. This vulnerability, affecting versions up to and including 45.16.0, allows unauthenticated attackers to exploit a Local File Inclusion (LFI) vulnerability. Due to its
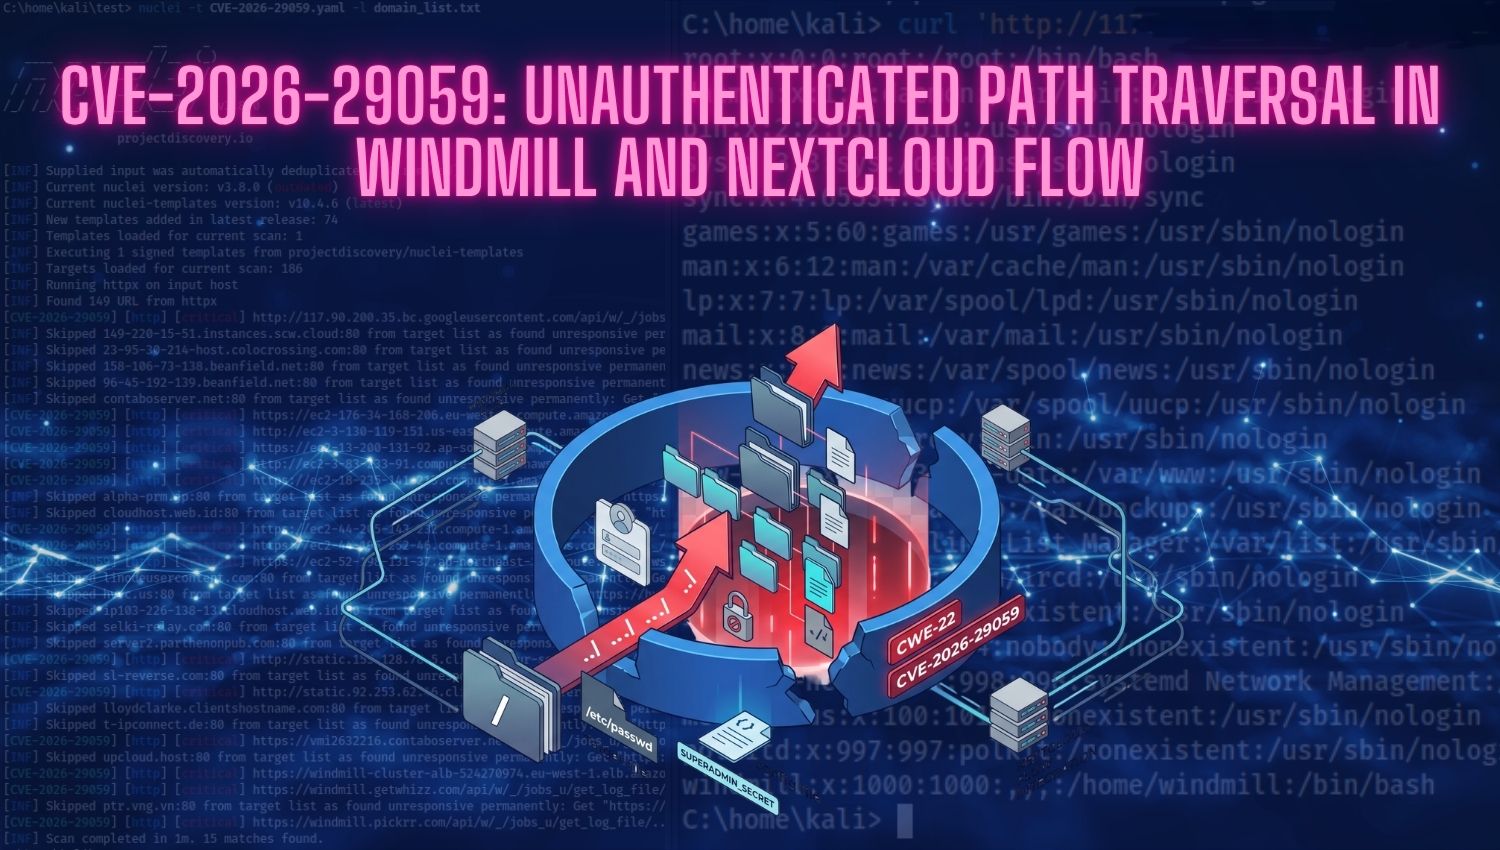
CVE-2026-29059: Unauthenticated Path Traversal in Windmill and Nextcloud Flow

CVE-2026-29059 UnauthentIcated Path Traversal In WIndmIll and Nextcloud Flow

Introduction Modern enterprise automation relies heavily on unified workflow engines to connect disparate infrastructure components, manage background tasks, and streamline internal processes. Platforms such as Windmill and its integrations—including Nextcloud Flow—provide robust execution environments for scripts and automated jobs. However, because these systems process sensitive data and hold elevated permissions across networks, any inherent flaw severely expands an organization’s attack surface. When central infrastructure automation