Vulnerability Analysis: CVE-2026-86426 LibreNMS <= 26.7.0 – Unauthenticated API Access
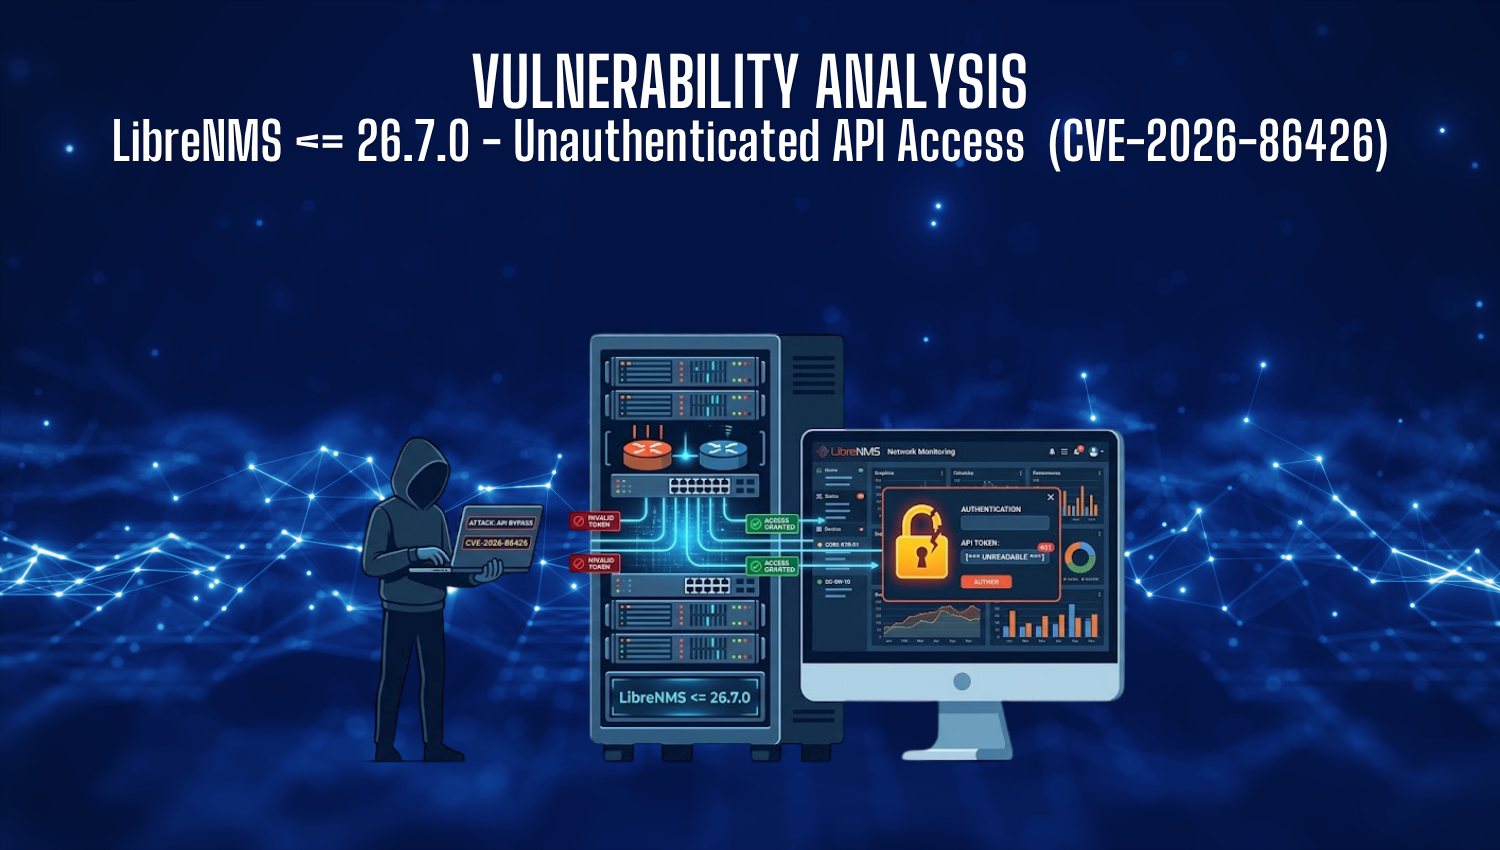
Introduction CVE-2026-86426 represents a critical authentication bypass vulnerability affecting LibreNMS network monitoring installations running version 26.7.0 or earlier. Publicly disclosed and addressed in late 2026, the vulnerability received a severe CVSS v4.0 rating of 9.2 (Critical) due to its low attack complexity and high impact. The underlying flaw resides within the API authentication middleware, which fails to strictly enforce parameter types during input
