Vulnerability Analysis CVE-2026-21589 Atlassian Jira/Confluence/Bitbucket – Pre-Auth Arbitrary File Read
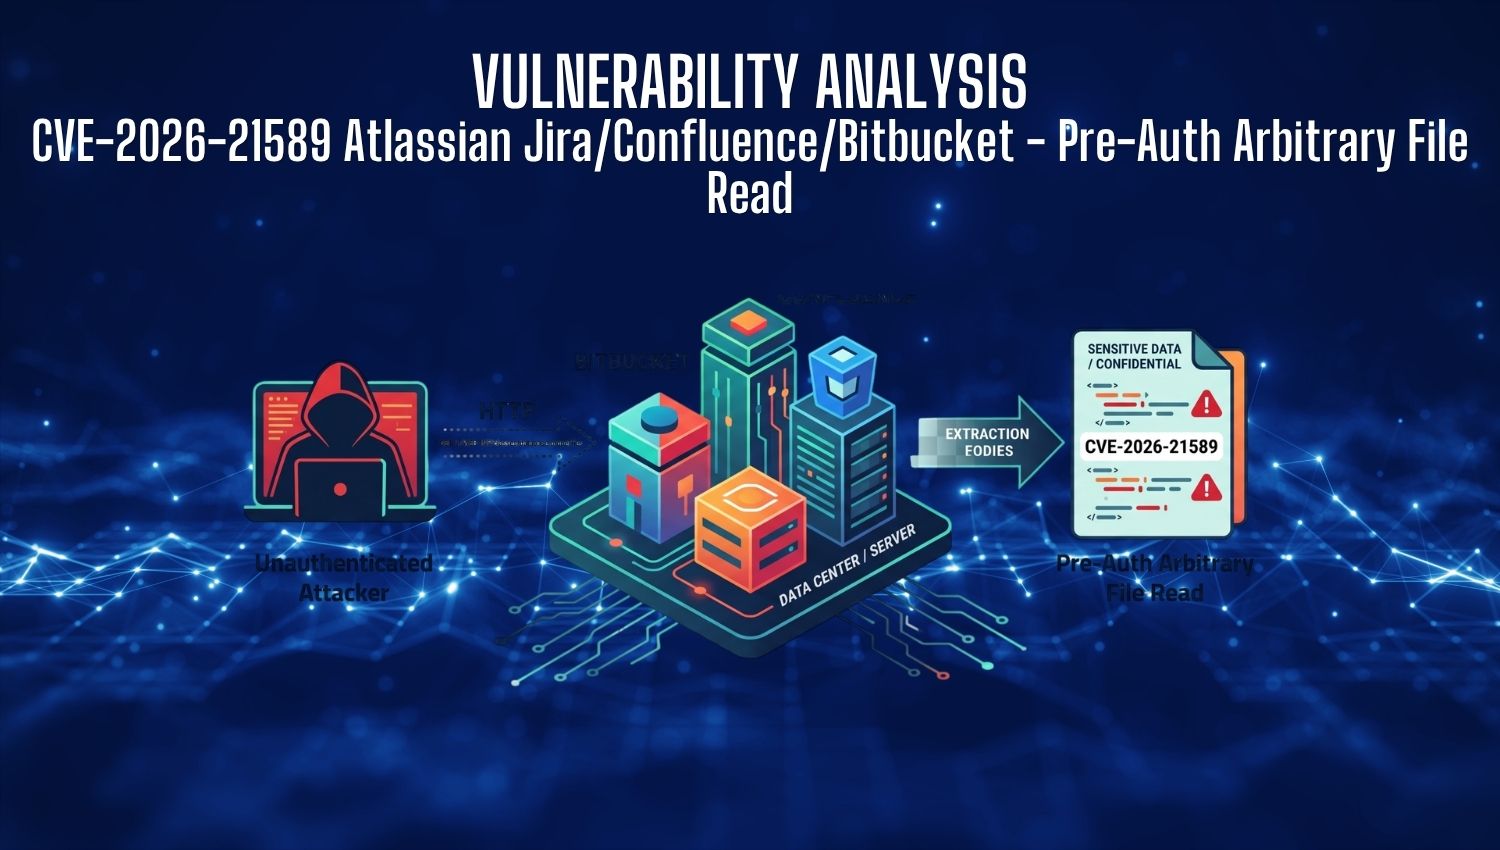
CVE-2026-21589

Introduction In October 2026, Atlassian issued an emergency security advisory disclosing CVE-2026-21589, a critical unauthenticated arbitrary file access vulnerability affecting its core self-hosted product suite. Assigned a CVSSv4 score of 9.3 (Critical), this security flaw allows unauthenticated remote threat actors to read arbitrary files directly from target system directories. Unauthenticated arbitrary file read vulnerabilities represent a severe risk to enterprise infrastructure because
The Hidden Gateway to Enterprise Networks: Unbound DNS Flaw and the Threat to Global Resolvers

Unbound DNS Flaw and the Threat to Global Resolvers

Introduction The Domain Name System functions as the foundational directory of global internet infrastructure, silently resolving human-readable hostnames into network addresses. However, severe memory management flaws and improper packet parsing within DNSSEC (Domain Name System Security Extensions) validation modules can instantly transform these trusted recursive resolvers into high-impact entry points for adversary breach campaigns. Officially tracked as CVE-2026-81642 and publicly disclosed by NLnet