Vulnerability Analysis CVE-2026-21589 Atlassian Jira/Confluence/Bitbucket – Pre-Auth Arbitrary File Read
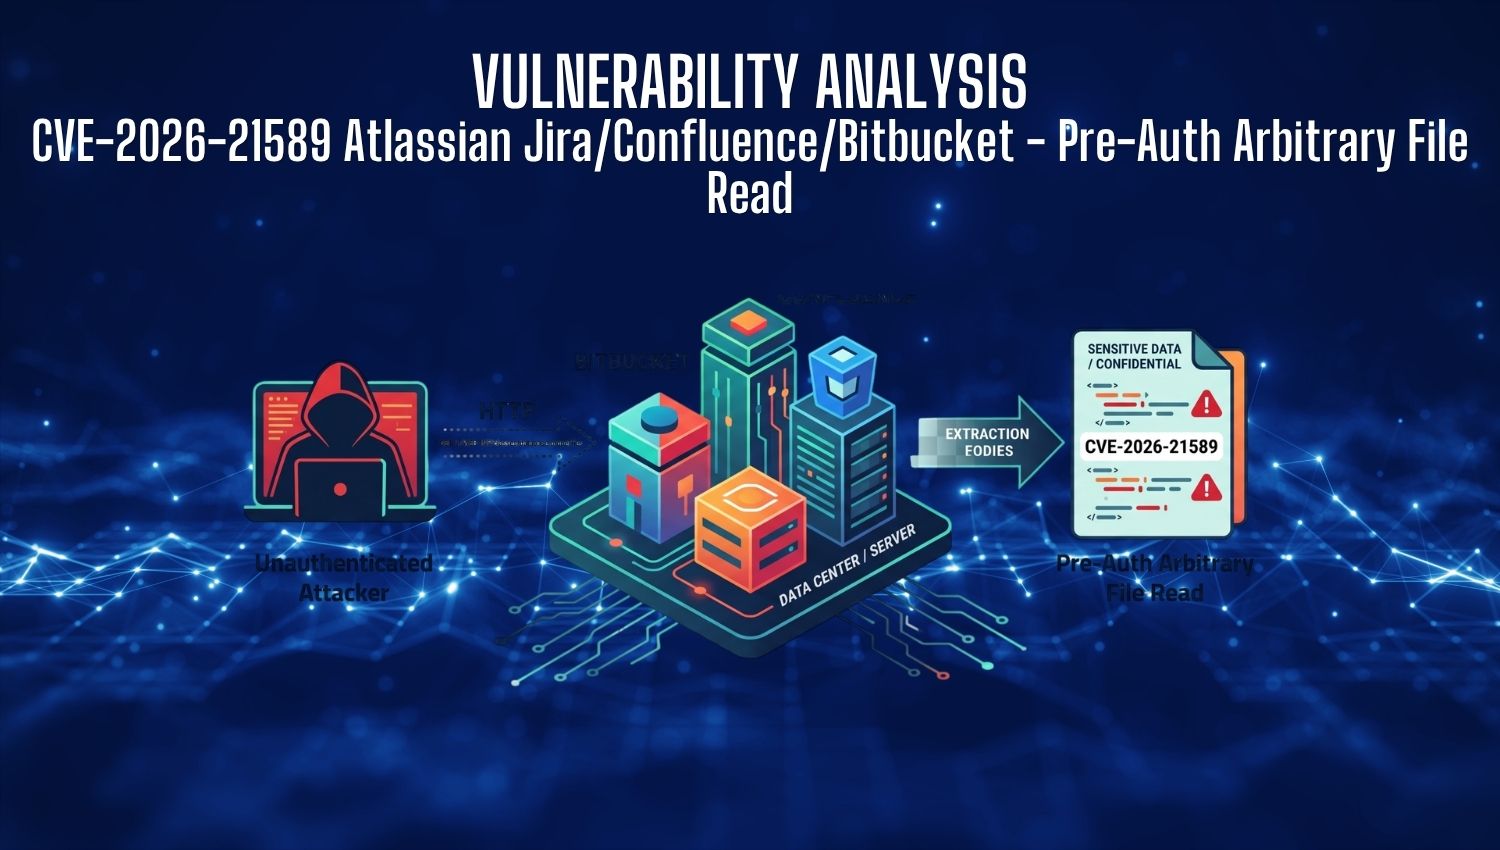
Introduction In October 2026, Atlassian issued an emergency security advisory disclosing CVE-2026-21589, a critical unauthenticated arbitrary file access vulnerability affecting its core self-hosted product suite. Assigned a CVSSv4 score of 9.3 (Critical), this security flaw allows unauthenticated remote threat actors to read arbitrary files directly from target system directories. Unauthenticated arbitrary file read vulnerabilities represent a severe risk to enterprise infrastructure because