Vulnerability Analysis CVE-2026-85706 GitLab – Arbitrary File Read
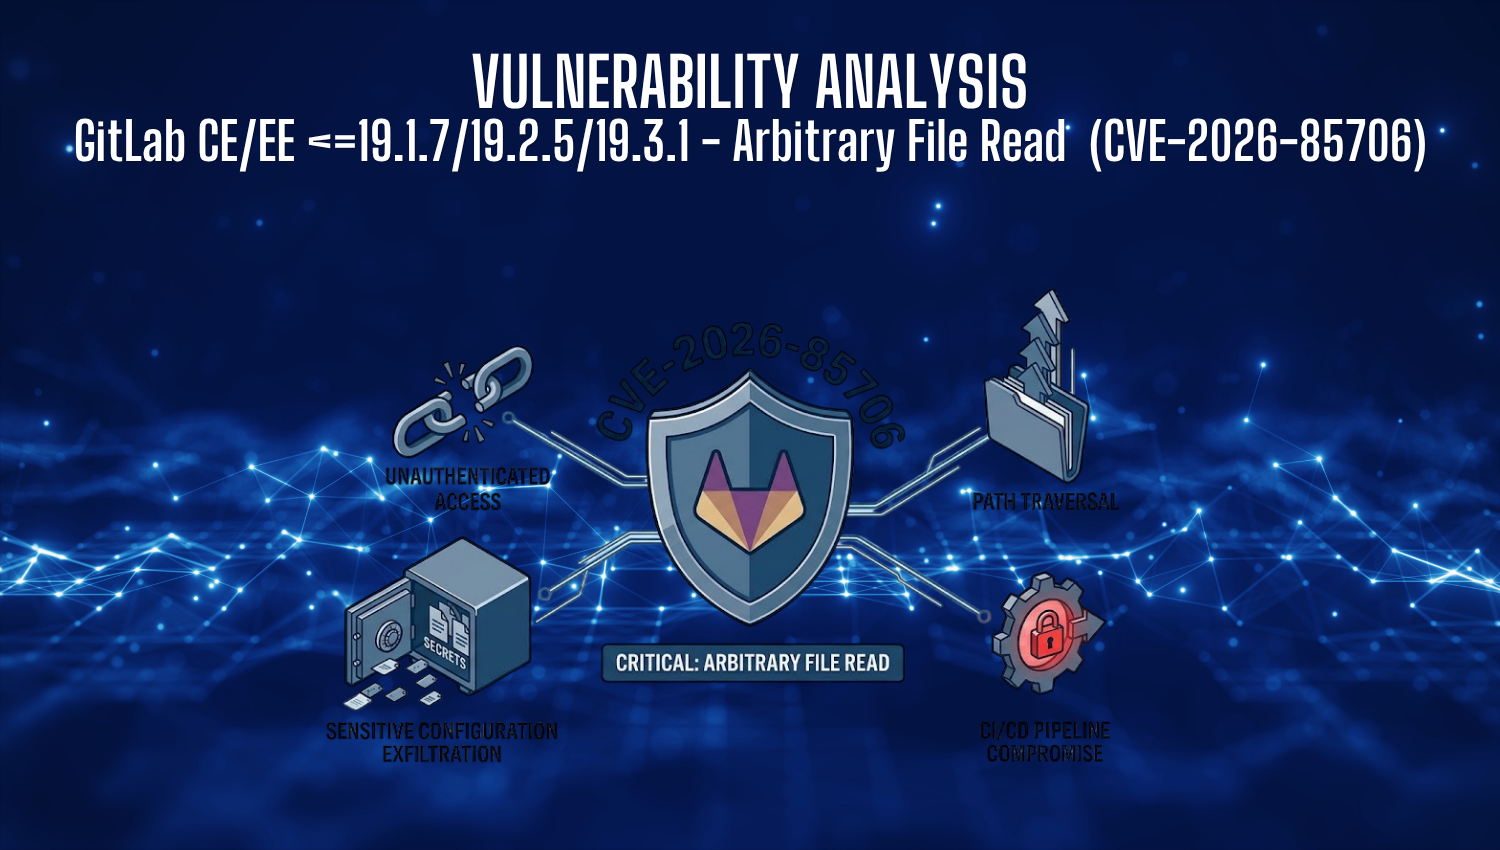
CVE-2026-85706 GitLab

Introduction Security flaws in critical software development and deployment infrastructure pose a significant, far-reaching risk to modern organizational supply chains. GitLab, an open-source DevOps platform used worldwide for source code management and continuous integration/continuous deployment (CI/CD) pipelines, released emergency security updates addressing CVE-2026-85706. This maximum-severity vulnerability—rated at CVSS 10.0—allows unauthenticated remote attackers to read arbitrary files directly from the host file system
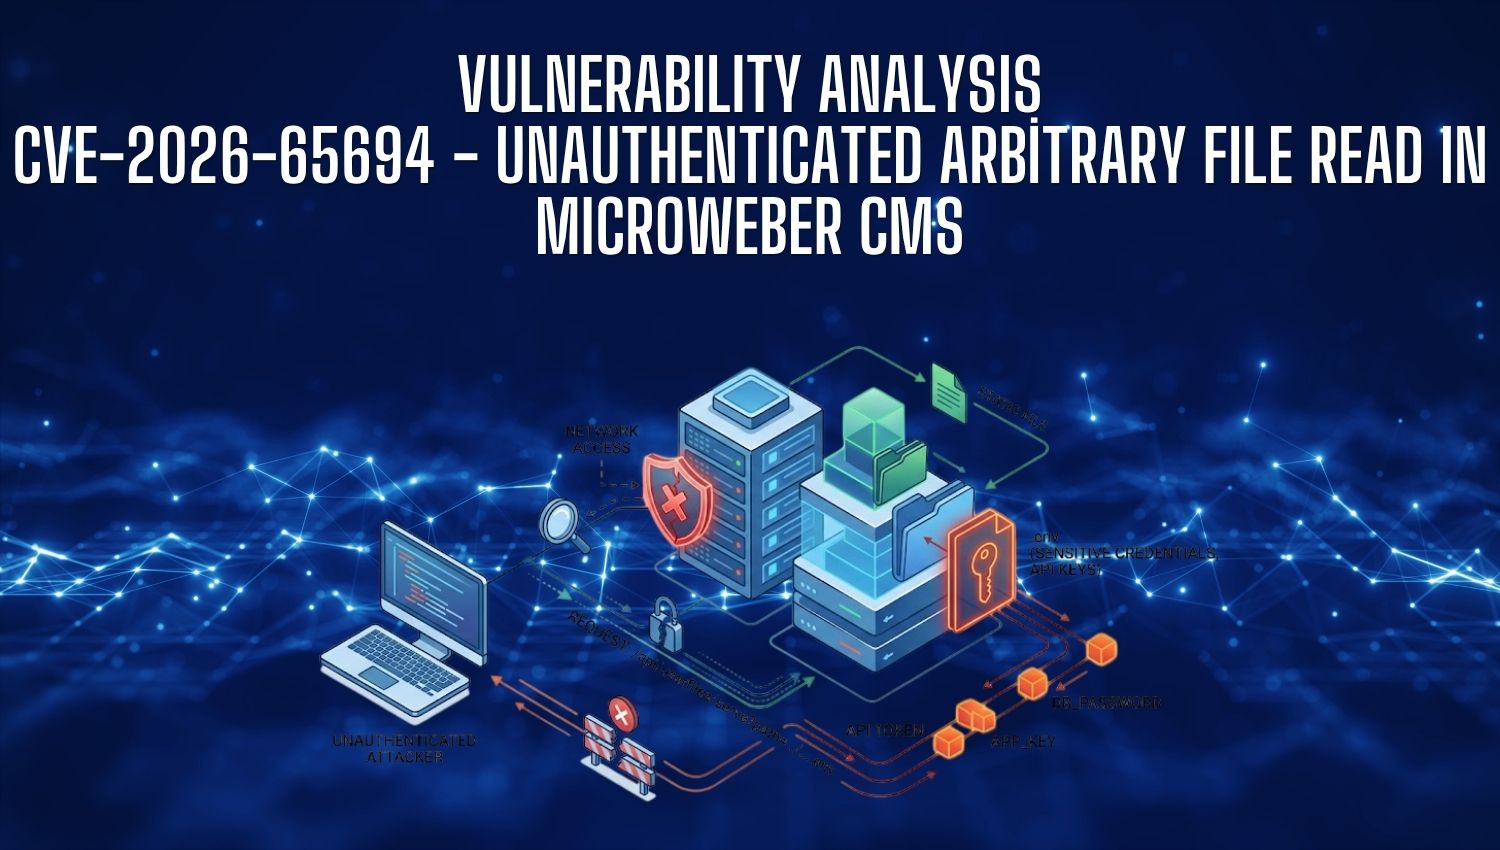
Vulnerability Analysis: CVE-2026-65694 – Unauthenticated Arbitrary File Read in Microweber CMS

Vulnerability Analysis CVE-2026-65694

Introduction Content Management Systems (CMS) form the backbone of modern web applications, handling everything from content publishing and dynamic page creation to user administration and media file management. However, this centralized functionality also presents an attractive attack surface for malicious actors when input sanitization mechanisms fail. When input validation fails within core controllers that serve assets or files, the security impact on