Vulnerability Analysis: CVE-2026-109518 APT MitM Vulnerability Grants Root Access
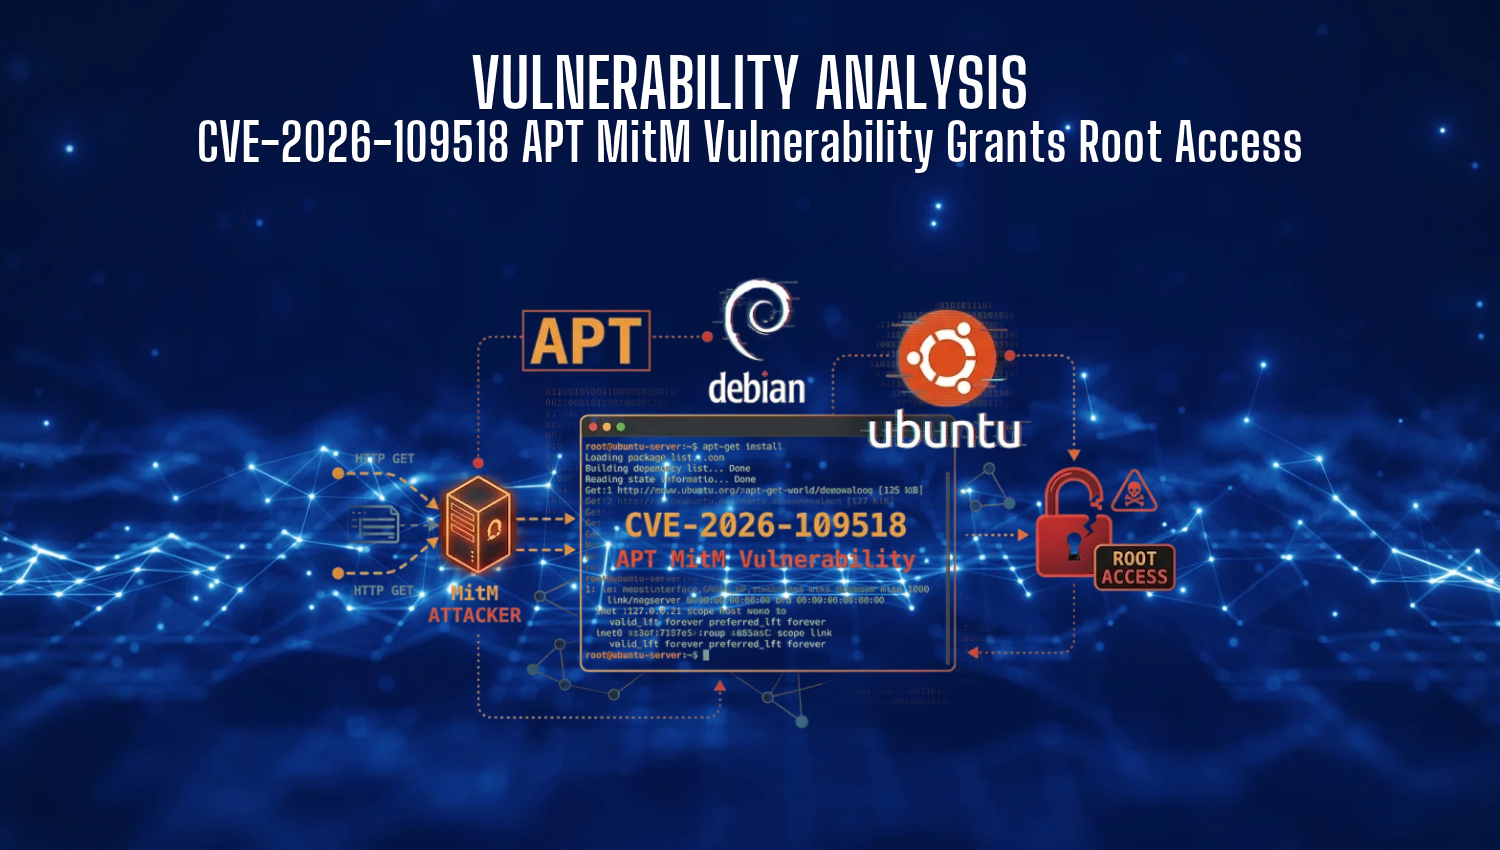
CVE-2026-109518 APT MitM Vulnerability Grants Root Access

Introduction Package managers are the backbone of system maintenance and software deployment in Linux environments. A critical security flaw, designated as CVE-2026-109518, has been identified in APT, the default package manager for Debian and Ubuntu distributions. Discovered by security researcher Max Justicz, this vulnerability allows a Man-in-the-Middle (MitM) attacker to intercept package downloads, bypass verification, and execute arbitrary code with root privileges. Because APT is ubiquitous
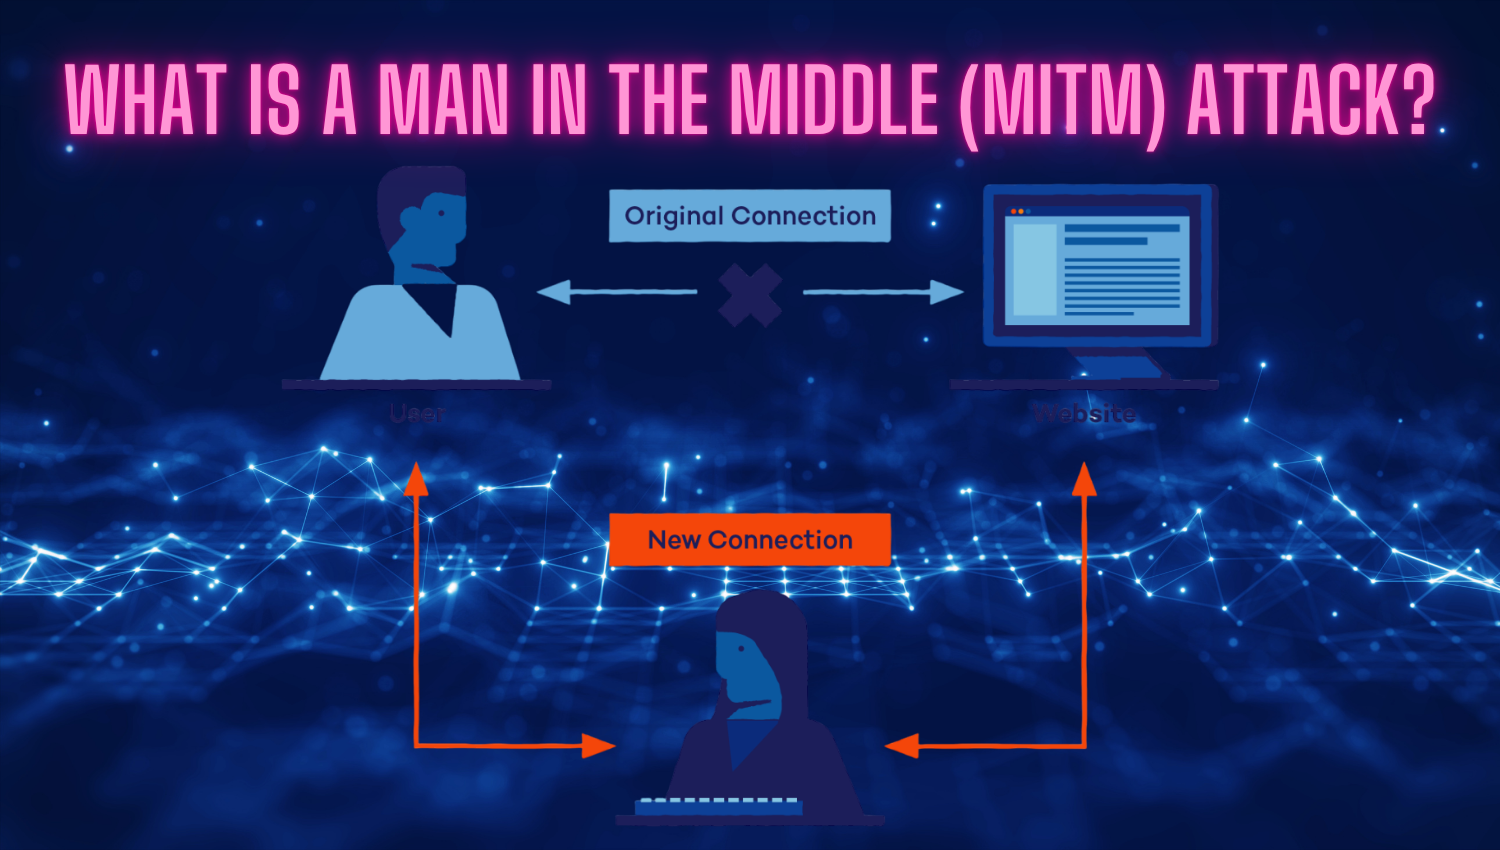
What is a Man-in-the-Middle (MITM) Attack?

What is a Man-in-the-Middle (MITM) Attack

Introduction In today’s interconnected digital environment, the security of our online communications is more crucial than ever. Every day, individuals and organizations exchange sensitive information—such as passwords, financial data, and private messages—across various digital platforms. As dependence on these technologies grows, so does the risk of cyber threats targeting the privacy and integrity of our data. One of the most significant and stealthy