Vulnerability Analysis: CVE-2026-123710 Critical Security Vulnerability in Red Hat Quay
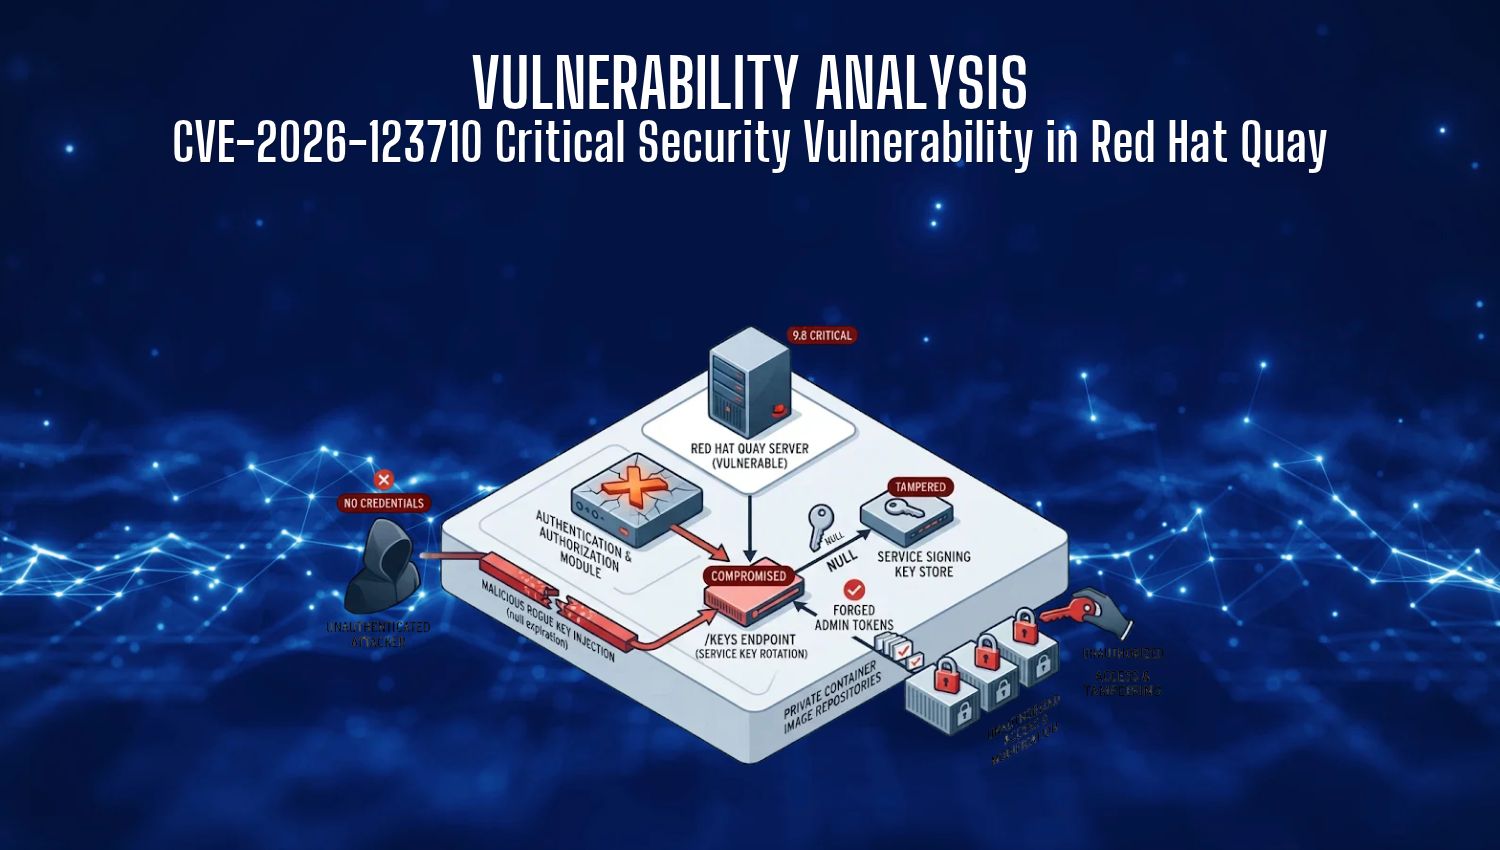
Introduction Containerized applications have become the undisputed backbone of modern enterprise architectures, transforming how software is packaged, shipped, and scaled across complex hybrid-cloud environments. As microservices proliferate, container registries serve as the central repositories for storing, managing, and distributing these vital artifacts, making them high-value targets for malicious threat actors. Red Hat Quay is widely deployed across enterprise ecosystems to ensure seamless, secure image management
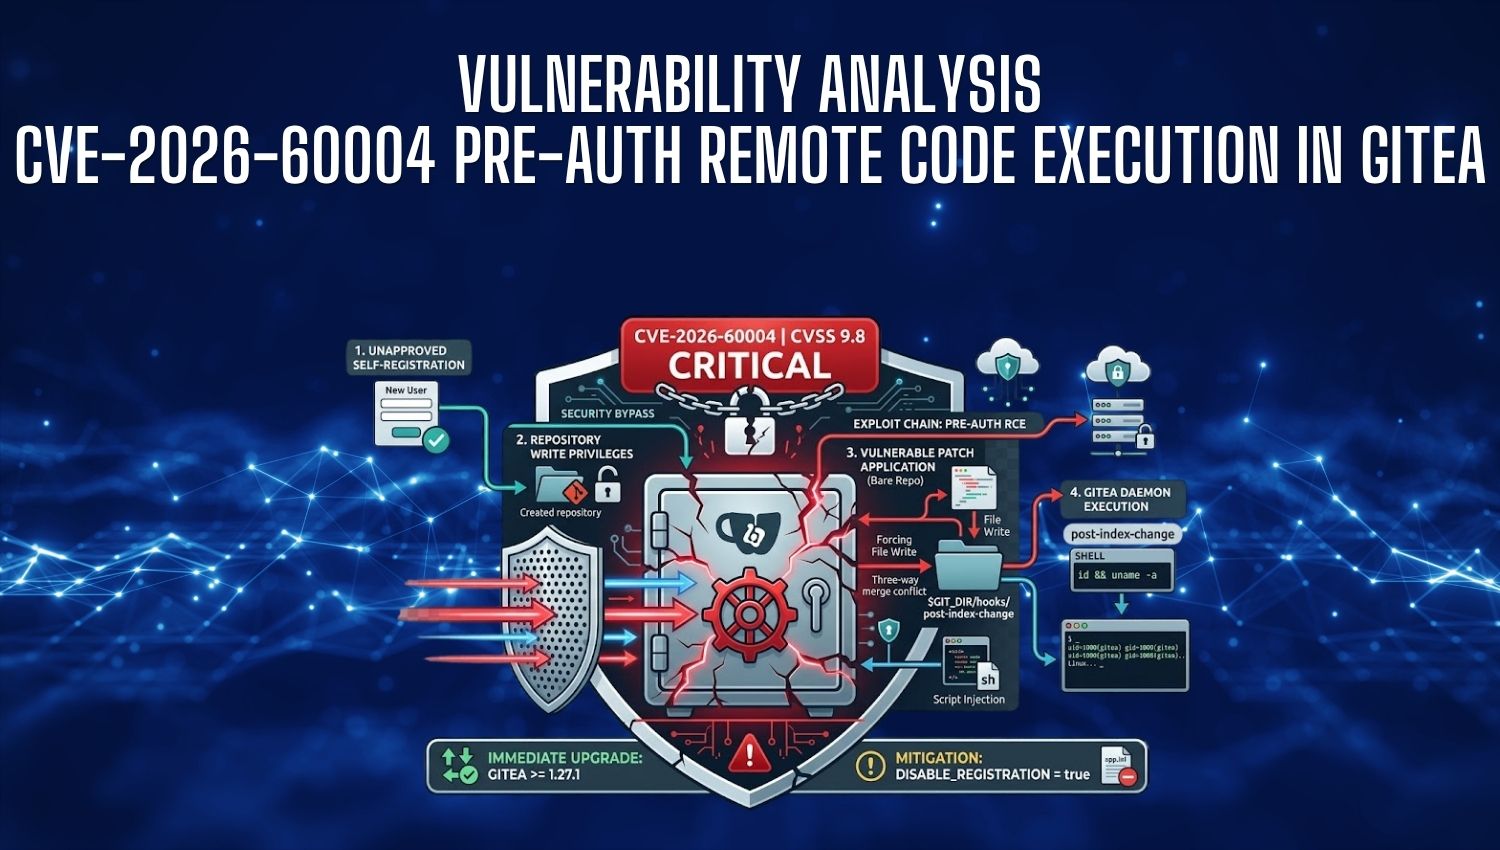
Vulnerability Analysis: CVE-2026-60004 Pre-Auth Remote Code Execution in Gitea

CVE-2026-60004 Pre-Auth Remote Code Execution in Gitea

Introduction Securing self-hosted version control platforms is critical for maintaining the integrity of modern software development pipelines, source code repositories, and automated CI/CD workflows. Gitea, a lightweight and widely adopted self-hosted Git service, recently addressed a critical security vulnerability identified as CVE-2026-60004. Carrying a maximum CVSS v3 score of 9.8 (Critical), this flaw enables unauthenticated remote attackers under default system configurations to achieve arbitrary