Vulnerability Analysis: CVE-2026-123710 Critical Security Vulnerability in Red Hat Quay
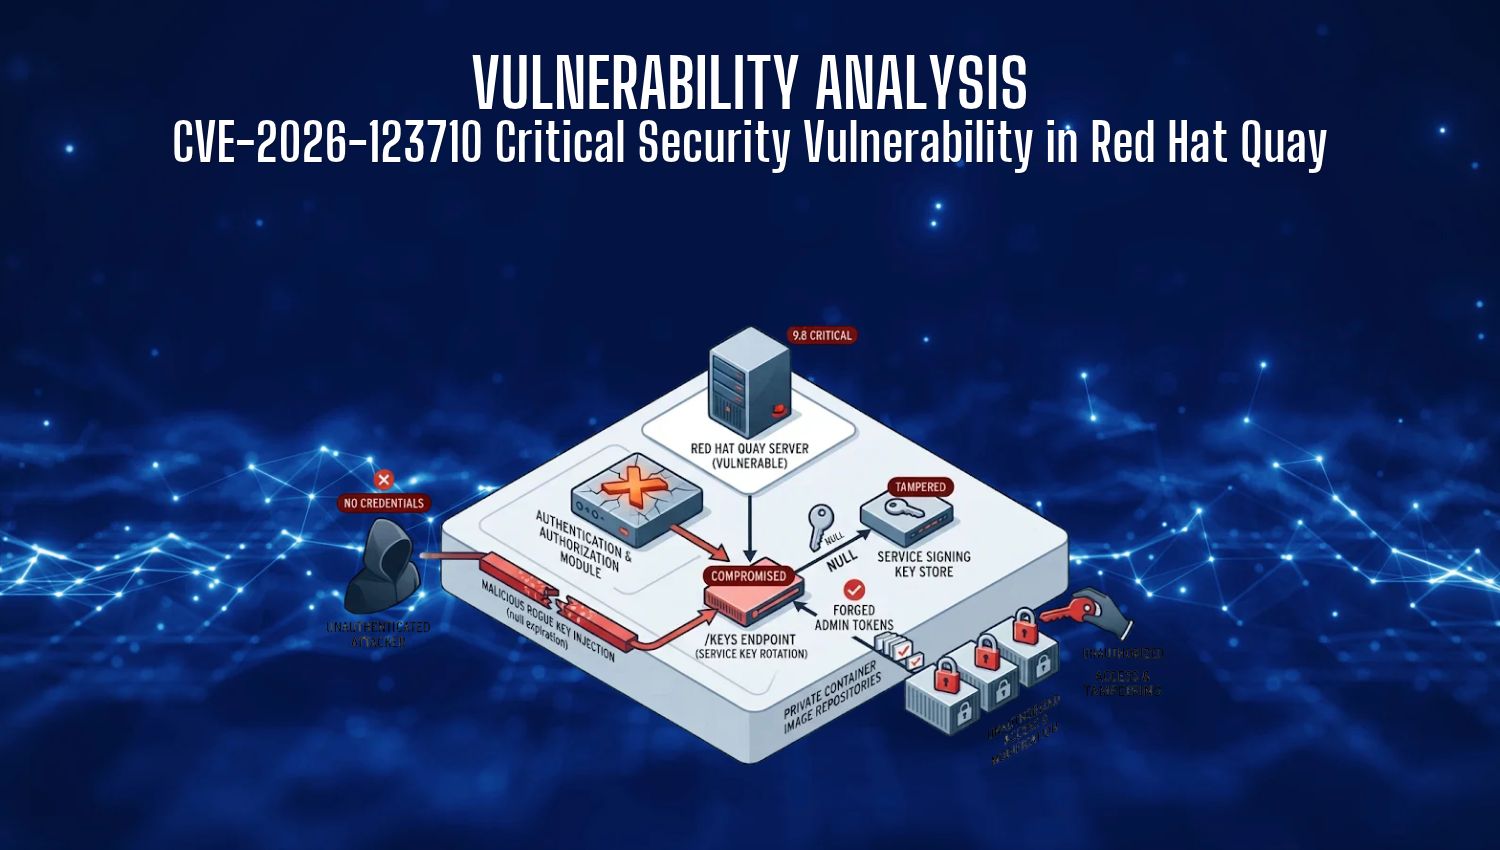
Introduction Containerized applications have become the undisputed backbone of modern enterprise architectures, transforming how software is packaged, shipped, and scaled across complex hybrid-cloud environments. As microservices proliferate, container registries serve as the central repositories for storing, managing, and distributing these vital artifacts, making them high-value targets for malicious threat actors. Red Hat Quay is widely deployed across enterprise ecosystems to ensure seamless, secure image management